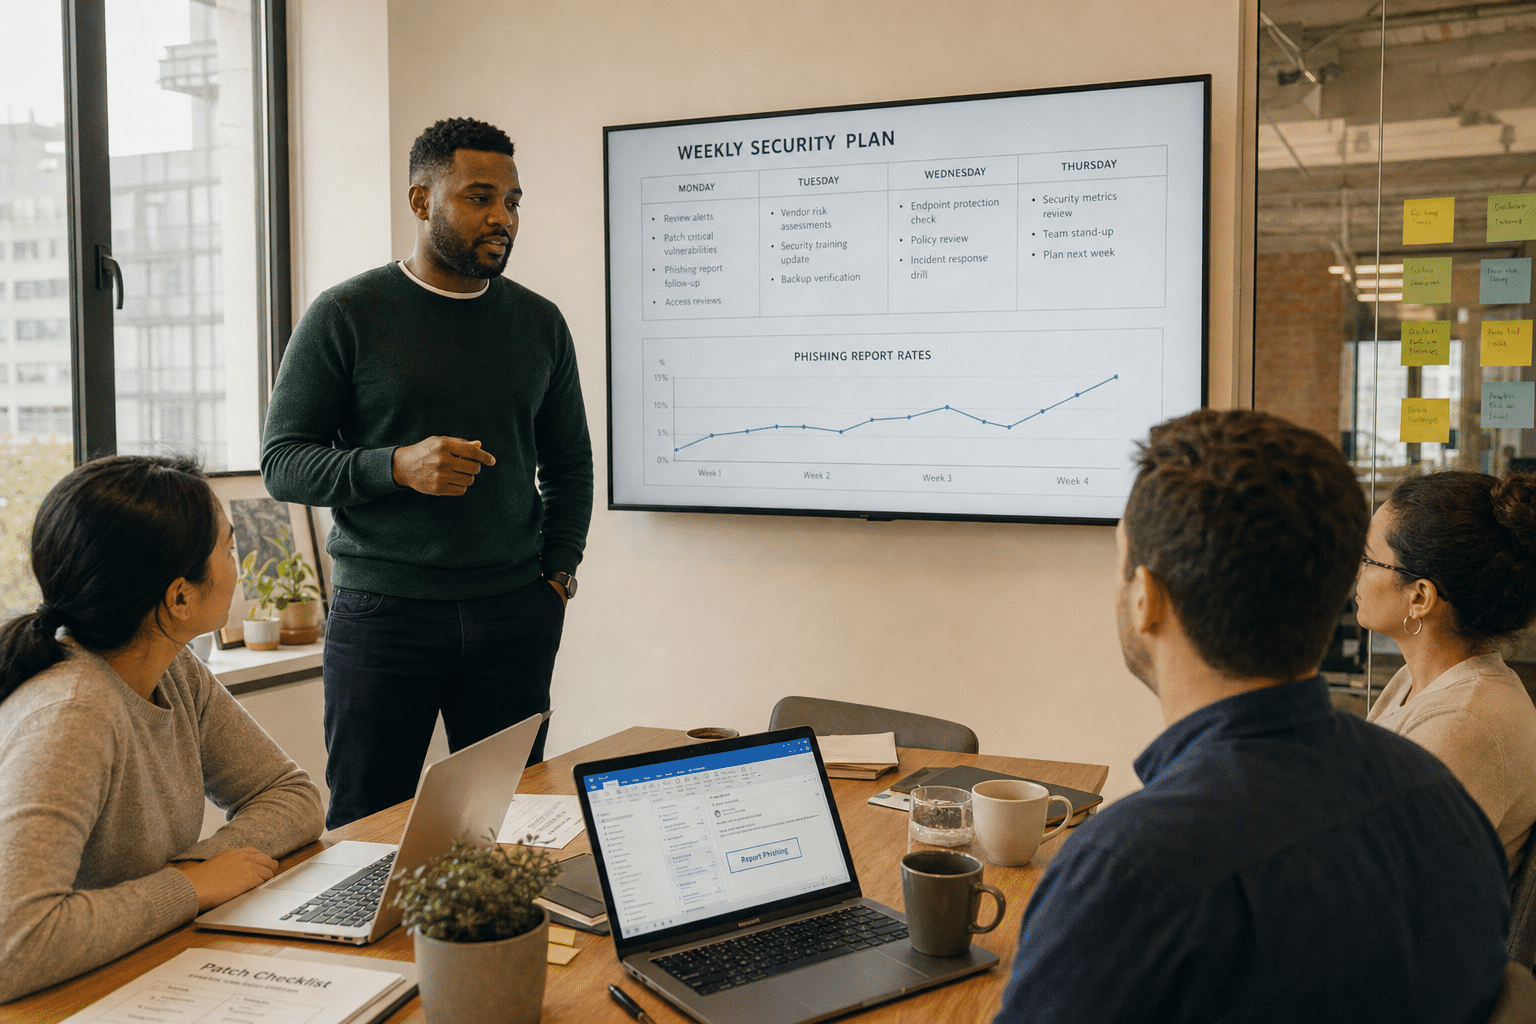
A practical cybersecurity awareness month plan for a 50-person company gives each of four weeks one job: week one tests and teaches phishing reporting, week two closes the patch backlog on laptops and servers, week three moves accounts to passkeys or app-based sign-in approval, and week four rehearses what staff do in the first hour of an incident. The month is judged by two numbers, the share of staff who report a test phish and the age of the oldest missing patch, not by how many people watched a video. Run it in October if you can, then repeat the same four-week cycle every quarter. A company without a full-time security person can deliver all of it with its existing IT provider and roughly two hours of each employee’s time across the month.
Why Awareness Month Kits Miss the Way Attackers Get In Now
The usual awareness month kit is four weeks of posters and videos about phishing, and that leaves out the entry point attackers are using more and more: software nobody patched. Industry breach reports over the last two years show exploited vulnerabilities climbing to sit alongside stolen passwords as a leading cause of intrusions, driven by edge devices such as VPN gateways and firewalls that small firms rarely update on schedule.
In our own client work, the pattern is consistent. A firm runs a phishing course in October, everyone clicks through it, and the firewall still runs firmware from the spring. The training was real and the risk did not move.
Here are the five principles behind the plan below:
- Teach one behavior per week. People remember a single habit, not a curriculum.
- Give the IT owner a week of real work. Patching is not a staff training topic, so it becomes a sprint for whoever runs your systems.
- Measure reporting, not clicking. A click rate rewards hiding mistakes; a reporting rate rewards speaking up.
- Change the sign-in, not just the lesson. Moving staff to phishing-resistant sign-in removes a whole class of attack.
- Rehearse the first hour. Staff who know who to call shorten every incident.
This plan is written for the owner, office manager or operations lead at a company of 30 to 80 people that relies on an outside IT provider or one internal generalist.
Who Owns the Month
A named owner turns awareness month from a calendar note into a program. In a 50-person firm that is usually the operations lead, with the IT provider handling the technical week.
Some owners argue the IT provider should run the whole month. That works for the technical pieces, but staff listen more closely when a manager they know introduces each week. The balance most firms land on is a manager as the voice and the provider as the engine. Budget about four hours of the owner’s time and two hours per employee, spread across the month.
What Two Hours per Employee Buys
Two hours per person across four weeks covers one live 30-minute session, two short micro-lessons, one simulated phish and one tabletop walk-through for team leads. That is small enough that nobody resents it.
Critics say two hours is too thin to change behavior. Our view is that frequency matters more than duration, which is why the plan repeats quarterly. A single eight-hour course in October fades by January; four short touches a quarter tend to stick.
Week One: Phishing Reporting for a Small Team
Week one of the cybersecurity awareness month plan builds one habit: when something looks wrong, report it with one click. Every later week depends on staff trusting that reporting is welcome.
Start the week with a 30-minute session that shows three real lures your own mail filter caught in the last quarter, with names removed. Real examples from your own inbox beat stock slides every time. Then add a report button to Outlook if you do not already have one, and show where it is. Our security awareness training programs start here for the same reason.
Running the First Simulated Phish
Send one simulated phish midweek, modeled on something believable for your business, such as a shared invoice or a voicemail notice. Keep it fair: no fake bonus announcements or layoff notices, which damage trust for months.
Some teams prefer to skip simulations entirely and rely on teaching. Simulations do carry a cost in goodwill if handled badly. Handled well, with no public shaming and a short follow-up lesson for anyone who clicks, they give you the only honest measure of how your team behaves under pressure. Our earlier guide on running employee cybersecurity awareness training covers session formats in more depth.
The Number That Matters in Week One
Track the reporting rate: the percentage of recipients who reported the test message within an hour. A first test at a small firm often lands somewhere near one in five.
Click rate still gets recorded, but it should not be the headline. When leaders celebrate a low click rate, staff learn to quietly delete suspicious mail instead of reporting it, and the security team loses its early warning. Thank every reporter by name in the week-two kickoff.
Week Two: A Patch Sprint Instead of Another Lesson
Week two turns the cybersecurity awareness month plan toward the systems themselves, because unpatched devices are now one of the most common ways into a small network. This is the week staff barely notice and your IT owner works hardest.
The goal is simple: by Friday, no device in the company should be missing a security update older than 30 days. That includes laptops, servers, the firewall, the VPN appliance, wireless access points, printers and any line-of-business software with its own updater.
Building the Inventory in a Day
Patching starts with a list. Ask your IT provider for an export from the device management or remote monitoring tool showing every device, its operating system build and its last update date.
Owners often assume the provider already patches everything. Many do patch Windows laptops automatically, while firewalls, NAS boxes and the accounting server sit outside that routine. The inventory exposes those gaps quickly, and it is worth knowing before an attacker finds them. If you are unsure what this work should cost, our guide to building a cybersecurity budget for a small business breaks down typical line items.
Edge Devices First
Patch internet-facing equipment before anything else: the firewall, VPN gateway, remote desktop gateway and any device with a public management page. These are the boxes attackers scan for within days of a vendor advisory.
Updating a firewall carries real risk of a short outage, which is why some firms put it off. The answer is scheduling, not avoidance. Book an evening window, take a configuration backup, and have the provider confirm remote access works before anyone leaves. Firmware that has fallen out of vendor support should go on a replacement list with a date attached.
Measuring Patch Age
The week-two metric is the age of the oldest missing critical patch across the fleet. Write it down on Monday and again on Friday.
A firm that starts at 140 days and ends at 12 has made more progress against real attacks than any slide deck could. Share the before-and-after number with staff in the week-three kickoff; it shows them the month is about more than their inbox.
Week Three: Moving Accounts to Phishing-Resistant Sign-In
Week three of the plan replaces sign-in methods that phishing can defeat. Text-message codes and simple push approvals can be intercepted or spammed; passkeys and number-matching approvals stop most of those attacks outright.
For a firm on Microsoft 365, the practical steps are turning on number matching for the Authenticator app, enabling passkeys for staff who handle money or client data, and blocking legacy sign-in protocols that skip multi-factor checks entirely.
Who Moves First
Start with the people attackers target most: whoever approves payments, the owner, HR and anyone with administrator rights. In a 50-person firm that is often eight to twelve people.
Some leaders worry that a sign-in change will flood the help desk. It does generate questions for a few days. Running a 15-minute walk-through for each group, and scheduling it rather than forcing it at login, keeps the disruption small. Short refreshers from a Microsoft 365 training session help staff who are uneasy with the Authenticator app.
Tie It to Verification Habits
The second half of week three teaches one rule: any request to change bank details, buy gift cards or send credentials gets confirmed by phone, using a number already on file.
Voice cloning and convincing fake invoices now make the old advice of checking the sender address insufficient. A callback rule is boring and it works. Pair it with the access principles in our article on zero trust security for small businesses, which applies the same never-assume thinking to systems.
Vendor Accounts Count Too
Third-party apps connected to your email or files are part of your sign-in surface. Review which outside tools have been granted access to company mailboxes and remove the ones nobody uses.
This review often surfaces AI tools staff connected on their own. Some are harmless; others read every message. Our checklist on AI vendor review blind spots for small business is a useful companion for that conversation.
Week Four: Rehearsing the First Hour of an Incident
Week four closes the cybersecurity awareness month plan by making sure staff know what to do when something has already gone wrong. The first hour of an incident decides how much it costs, and most of that hour depends on people, not tools.
Run a 45-minute tabletop exercise with team leads, the owner and your IT provider. Walk through one realistic scenario, such as an employee who entered their password on a fake sign-in page and then noticed odd mail rules in their inbox.
What the Tabletop Should Answer
The exercise should produce answers to four questions: who the employee calls first, who can disable an account after hours, who talks to clients if data is exposed, and where the cyber insurance policy and its hotline number are kept.
Some owners feel a tabletop is overkill for a company their size. The opposite tends to be true. Large firms have runbooks and on-call rotations; a 50-person company usually has one person who knows the admin password, and nobody has asked what happens if they are on a plane.
Connecting It to Recovery
The tabletop should end by checking that backups would actually restore the systems the scenario touched. If nobody can say when a restore was last tested, schedule one.
Recovery planning sits next to awareness work, not apart from it. Our article on the parts of a business disaster recovery plan lists what a small firm’s plan should cover. Write the answers from the tabletop onto one page and pin it in every team channel.
Making the Four-Week Plan a Quarterly Habit
The most valuable step in any cybersecurity awareness month plan is repeating it. A single October push fades; a four-week cycle run every quarter, with lighter weeks, keeps habits fresh and keeps patch age low.
Each quarter, send one new simulated phish, rerun the patch-age report, review sign-in methods for new hires and walk one new scenario with team leads. That is roughly one hour per employee per quarter. Track the reporting rate and oldest-patch age on a single chart; leaders will see the trend without needing a security background.
If your firm lacks the internal time to run the cycle, an outside partner can carry the technical weeks while your managers keep the voice. Our cybersecurity services team supports firms in exactly that split.
Frequently Asked Questions
Does a cybersecurity awareness month plan have to run in October?
No, the four-week plan works in any month. October brings free materials and staff attention, but the program matters more than the date, and repeating it quarterly is what keeps results.
How much does a four-week awareness program cost a 50-person company?
Most of the cost is staff time, roughly two hours per employee plus the owner’s coordination. Simulation and training platforms for a firm this size are usually modest annual subscriptions, and patching work may already sit inside an IT support agreement.
Should employees who click a simulated phish be disciplined?
We advise against discipline for simulation clicks. A short follow-up lesson works better, and punishment teaches people to hide real mistakes, which is the opposite of what you want during an actual attack.
Is multi-factor authentication by text message still acceptable?
Text-message codes are better than passwords alone but can be intercepted or redirected through SIM swapping. Passkeys or app approvals with number matching are the stronger choice for staff who handle money, client data or administrator access.
What should we measure at the end of the month?
Measure the reporting rate on simulated phishing and the age of the oldest missing critical patch. Those two numbers track the human and technical sides of risk and are easy to compare quarter to quarter.
Who Stands Behind This Guidance
Mindcore Technologies has helped small and mid-sized organizations run security awareness and patching programs for years, from firms of 20 people to multi-site companies with several hundred staff. The plan above reflects what we see work in practice: short, repeated lessons, a real technical sprint and clear first-hour roles. Our founder and CEO, Matt Rosenthal, focuses on making enterprise-grade security practical for growing businesses, and that approach shapes how our team builds every awareness program.
Start Your Four-Week Cybersecurity Awareness Plan
A four-week plan that teaches reporting, closes the patch backlog, hardens sign-in and rehearses the first hour of an incident does more for a 50-person company than any single training day. Pick an owner, put four kickoff dates on the calendar, ask your IT provider for the patch-age report, and send your first simulated phish within two weeks. Judge the month by reporting rate and patch age, then run the cycle again next quarter with lighter weeks. Each round gets faster, and by the third cycle most teams treat it as normal operations rather than a special event. If you want a partner to run the technical weeks or design the simulations, book a free strategy call and we will map the plan to your people, devices and budget.