

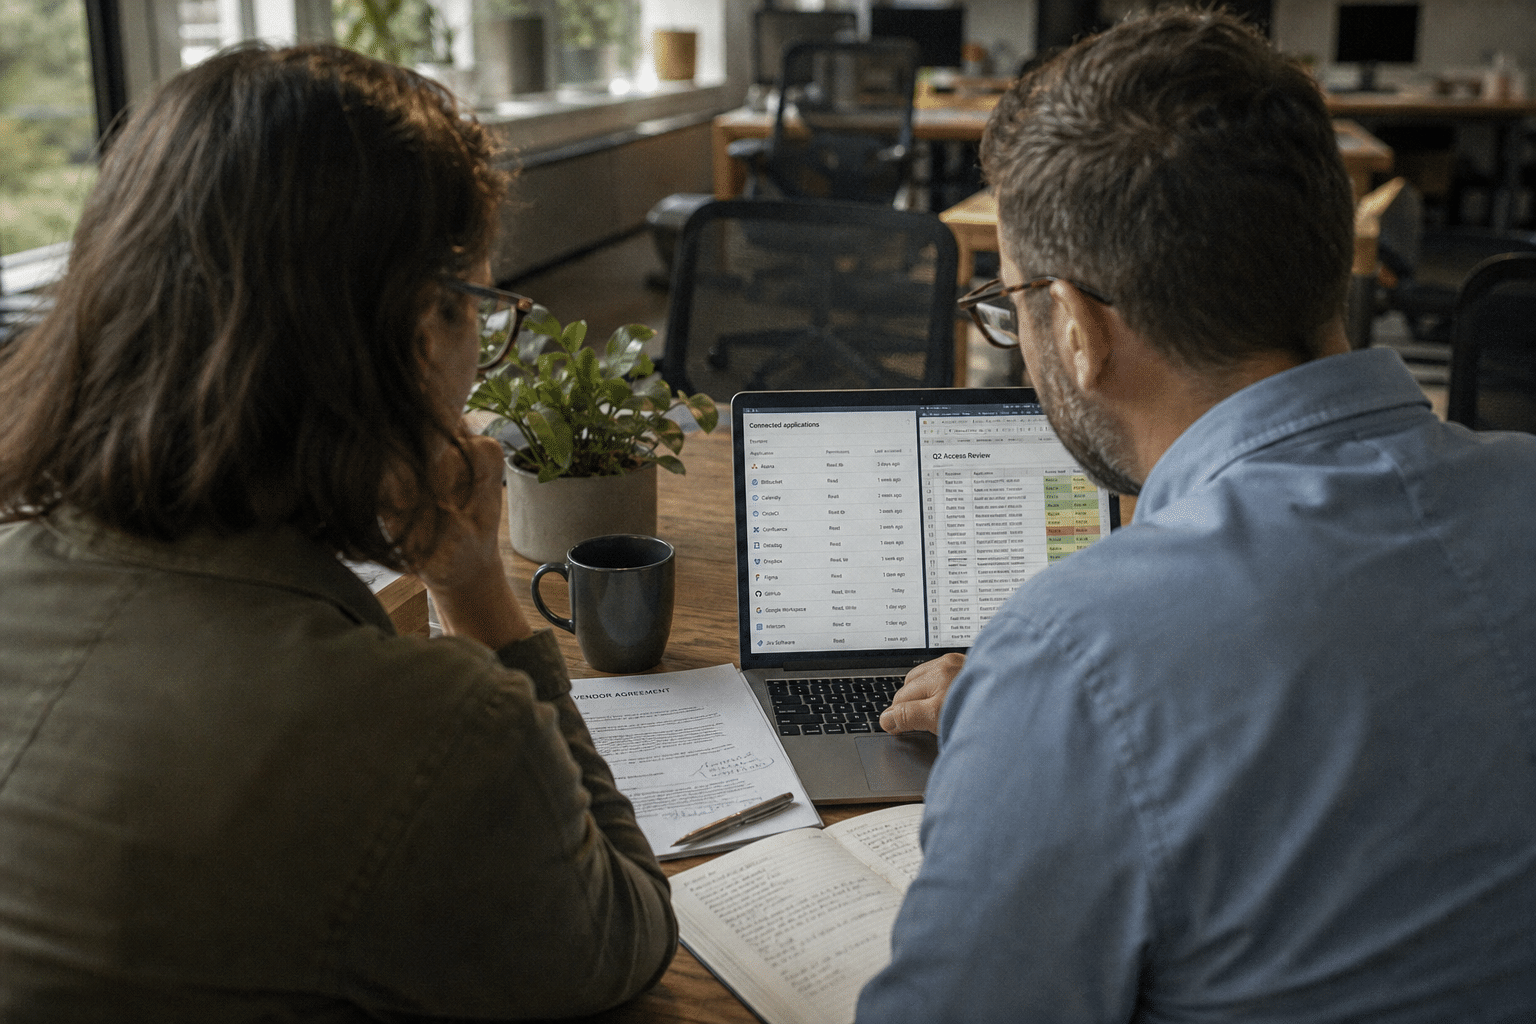
Third-party AI agents in SaaS tools are the assistants, copilots and automated workers that your software vendors switch on inside products you already license, and most of them never authenticate through your single sign-on. That matters because your identity stack can only govern what logs in through it. The 2026 State of Agent Security Report, as covered by The Hacker News, counted roughly 1,280 third-party products embedding AI in the environments it studied, and only about 282 of them sat behind SSO. The other thousand were not hidden by anyone. They simply talk to your data vendor-to-vendor, through API tokens and OAuth grants issued months ago for a different purpose. Our team sees the same pattern in client audits: the agents a business deliberately chose are well governed, and the ones it inherited are not governed at all. This article lays out where those inherited agents live and how to close the five gaps they open.
The Five Points to Take Away
Before the detail, here is the short version our consultants give leadership teams.
- Most agents were never chosen. A help desk platform, a CRM and a document tool can each add an AI feature through a routine release note, and nothing in your approval process fires.
- SSO coverage is not agent coverage. An agent acting through a stored API token or an OAuth refresh token never appears in your identity provider sign-in logs.
- The contract is the control surface. Data use, model training, sub-processors and retention for embedded AI are set by vendor terms, and most were signed before the AI feature existed.
- Discovery is a log and paperwork exercise. OAuth consent records, SaaS admin consoles and renewal documents reveal more agents than any network scan.
- Ownership beats tooling. Every embedded agent needs a named internal owner who can switch it off, otherwise inventory work decays within a quarter.
This piece is written for IT managers and security leads at firms of 50 to 500 people who already run Microsoft 365 or Google Workspace with SSO, and who assume that coverage extends further than it does.
Why Third-Party AI Agents in SaaS Tools Slip Past Your Identity Stack
Third-party AI agents in SaaS tools slip past identity controls because they authenticate as the vendor’s service, not as a person in your directory. When your staff sign in to a project tracker through Okta or Entra ID, that session is visible and revocable. When the tracker’s built-in assistant later reads every ticket to summarize them, it uses the vendor’s own back-end access, which your identity provider never sees.
Does SSO still protect the data an embedded agent reads?
SSO protects the front door, and in that sense it still does real work: a terminated employee loses access to the tool, and with it the ability to prompt the assistant. The opposing view is just as true. The agent itself does not depend on any one user session. It keeps running against the data set you uploaded, often with tenant-wide read rights, after every individual login has expired. Both statements hold at once, which is why we tell clients to treat SSO as a user control and to look elsewhere for an agent control. The practical test is simple: if you disabled every user account tomorrow, would the vendor’s AI still be able to process your records? In most products we review, the answer is yes.
Why do API tokens outlive the people who created them?
Integration tokens are usually created by one administrator during a setup afternoon, and they rarely expire. Some teams argue this is fine because the token is scoped to one integration. In practice, the scope was chosen for the original use case, such as syncing contacts, and a later AI feature reuses the same connection to read far more than contacts. We find tokens owned by people who left the company years earlier on almost every assessment. Those tokens are the plumbing that third-party agents ride on, and nobody reviews them because they do not look like an AI decision.
What changes when the vendor ships an agent through a release note?
A release note is the most common way an agent arrives. Vendors argue, reasonably, that customers asked for these features and that the data never leaves the platform. Critics counter that “never leaves the platform” often means the vendor passes it to a model provider acting as a sub-processor. Neither side is lying. The point for you is that the decision was made by the vendor’s product team, on the vendor’s schedule, and your change process never saw it. Our guidance on managing third-party cyber security risks applies directly here: a material change to what a vendor does with your data is a risk event, even when it ships as a feature.
Where Embedded Agents Hide in the Software You Already License
Embedded agents concentrate in the tools that hold the most text: support desks, CRMs, document libraries, meeting platforms and HR systems. Those are exactly the places where client records, contracts and personnel files live.
Which SaaS categories carry the most agent exposure?
Meeting recorders and note takers top our list, because they capture full conversations and often join calls automatically once one person installs them. Support platforms come next, since their assistants read entire ticket histories to draft replies. CRMs, e-signature tools and document platforms follow. A fair counterpoint is that these vendors usually invest heavily in security, and many hold SOC 2 reports. That is true, and it is also beside the point: a SOC 2 report describes the vendor’s controls, not whether you approved an AI feature reading your data. Document libraries deserve separate attention, as we covered in our look at AI integration tools for SharePoint document libraries, where permission inheritance decides what an assistant can surface.
How do OAuth grants turn a browser extension into an agent?
An OAuth grant lets a third-party app act on a user’s behalf with whatever scopes the user clicked through. Supporters of the model say it is far safer than sharing passwords, and they are right. The weakness is consent fatigue: one employee approving “read your mail and files” for an AI writing assistant hands that vendor persistent access to their mailbox. Industry surveys report that most organizations lack full visibility into the apps connected this way. For businesses that handle claims or member data, such as the third-party administrators we support, one consent screen can expose regulated records to a vendor nobody vetted.
Are vendor-to-vendor integrations agents too?
Many of the 1,000 unseen products in that report are integrations between two SaaS platforms, connected once and left running. Purists argue an integration is not an agent unless it makes decisions. We think that distinction is fading. When a sync connector starts using a model to classify, route or rewrite records, it is making decisions about your data, whatever the vendor calls it. Treat any connector that now carries an AI label as an agent for inventory purposes.
The Vendor Contract Is Your Real Agent Control
The contract, not the firewall, decides what a third-party agent may do with your data, because the agent operates entirely inside the vendor’s environment. That makes procurement and legal review the strongest controls you have.
Which clauses matter most for embedded AI?
Four clauses carry most of the weight. First, model training: does the vendor or its model provider train on your content, and is that opt-in or opt-out? Second, sub-processors: is the model provider named, and do you get notice before it changes? Third, retention: how long are prompts, outputs and intermediate data kept? Fourth, the right to disable: can an administrator switch the AI feature off at tenant level without losing the core product? Vendors often argue that standard terms already cover this. Sometimes they do. Often the AI addendum is a separate click-through accepted by whichever admin first enabled the feature.
Should you renegotiate or accept the standard terms?
Smaller firms rarely have leverage to rewrite a large vendor’s paper, and insisting can stall a renewal for months. That concern is legitimate. On the other side, most vendors already offer an enterprise data processing addendum and tenant-level AI switches, and simply asking for them at renewal costs nothing. Our recommendation is to request the existing options first and escalate only where regulated data is involved. A HIPAA covered entity or a defense contractor cannot accept an undefined sub-processor list, whatever the leverage.
How does renewal season become your inventory checkpoint?
Renewal is the one moment each year when the vendor relationship is reviewed anyway. Add three questions to every renewal: what AI features are now enabled in our tenant, which model providers process our data, and how do we disable them. Finance teams sometimes resist adding steps to renewals, and we understand why. The questions take ten minutes and turn a recurring cost event into a recurring security review. Pair that with the access practices in our guide to managing third-party vendor access to your systems.
How to Find Third-Party AI Agents in SaaS Tools This Quarter
Finding third-party AI agents in SaaS tools starts with records you already hold: OAuth consent logs, SaaS admin consoles and your accounts payable ledger. You do not need a new platform to build a first inventory.
Step one: pull the consent and token records
Export enterprise application consents from Entra ID or the third-party app access report from Google Workspace. Sort by scopes that include mail, files or directory read. In parallel, list API tokens and integrations in each major SaaS admin console. Some teams prefer to buy a SaaS security posture tool first. That works, and it is worth it at scale, but a manual export finds the highest-risk grants in an afternoon and tells you whether the tool is worth buying.
Step two: reconcile against what you pay for
Your accounts payable and corporate card statements list every SaaS vendor you fund. Cross-reference them with the consent export. Anything paid for but missing from SSO is a candidate for the unseen thousand. Anything consented to but not paid for is usually a free AI tool an employee connected. Both lists matter, and the second one tends to be longer than leadership expects.
Step three: assign an owner and a kill switch
For each agent found, record the business owner, the data it touches, the contract terms that govern it and the exact steps to disable it. Where an agent cannot be disabled without losing the product, document that as an accepted risk signed by the owner. Agents that act autonomously need tighter review still, as we describe in our piece on autonomous workflow agents and the risks before you let them run. For vendor sessions that need hands-on access, controlled entry points like the approach in securing third-party vendor access with ShieldHQ keep that access visible and time-bound.
The five risks to close, in order
- Unowned tokens. Revoke or reassign every integration token whose creator has left.
- Broad OAuth scopes. Restrict user consent to verified publishers and require admin approval for mail and file scopes.
- Silent feature enablement. Set tenant-level AI features to off by default where the vendor allows it, and turn them on deliberately.
- Undefined sub-processors. Get the model provider named in writing for every tool holding regulated data.
- No disable path. Document how to switch off each agent before an incident forces you to find out.
Frequently Asked Questions
What are third-party AI agents in SaaS tools?
Third-party AI agents in SaaS tools are AI features a software vendor runs inside a product you license, such as ticket summarizers, meeting note takers and CRM assistants. They act on your data using the vendor’s own access rather than a login in your directory, so your identity provider usually cannot see them.
Why does single sign-on miss embedded AI agents?
Single sign-on only governs sessions that authenticate through it. Embedded agents typically use stored API tokens, OAuth refresh tokens or the vendor’s back-end access, which never produce a sign-in event in your identity logs.
How can a small business inventory embedded agents without new tools?
Start with the enterprise app consent export from Entra ID or Google Workspace, the integration lists in each major SaaS admin console, and your accounts payable records. Reconciling those three sources finds most agents in a few days of work.
Can we turn off AI features a vendor has already enabled?
Most major vendors now offer a tenant-level switch for their AI features, though the setting is often buried in admin settings rather than the main console. Where no switch exists, ask for one at renewal and record the agent as an accepted risk with a named owner.
Which contract terms should we request for embedded AI?
Ask for a written position on model training with your data, a named list of model sub-processors with change notice, defined retention for prompts and outputs, and the right to disable AI features without losing the core service.
Who Is Behind This Guidance
Mindcore Technologies has spent years helping small and mid-sized businesses govern the vendors that touch their data, from managed security for healthcare practices to zero-trust access for firms with large contractor footprints. Our assessments now routinely include an embedded AI review, because the same third-party risk work our clients already rely on has to account for agents their vendors add without notice. You stay in control of the decisions; we bring the checklists, the log analysis and the contract questions that make those decisions faster. Mindcore is led by CEO Matt Rosenthal, who focuses on helping growing organizations adopt AI and cloud services with security designed in from the start rather than added after an incident. That perspective shapes how our team approaches AI agents for business: adopt deliberately, inventory everything, and keep a named person able to switch any agent off.
Book a Free Strategy Call to Map Your Unseen Agents
The agents most likely to expose your data are the ones nobody in your company chose, and closing that gap is a matter of records, contracts and ownership rather than another security product. Pull your OAuth consents and integration tokens, reconcile them against what you pay for, rewrite your renewal checklist to ask about AI features and sub-processors, and give every embedded agent an owner who can disable it. Do those four things and the thousand unseen products described in the 2026 State of Agent Security Report become a list you can manage instead of a blind spot. If you want a second set of eyes on that first inventory, our consultants can walk through your tenant with you and identify the highest-risk grants in a single session. Schedule a free strategy call and we will help you turn the agents you did not choose into agents you govern.

