

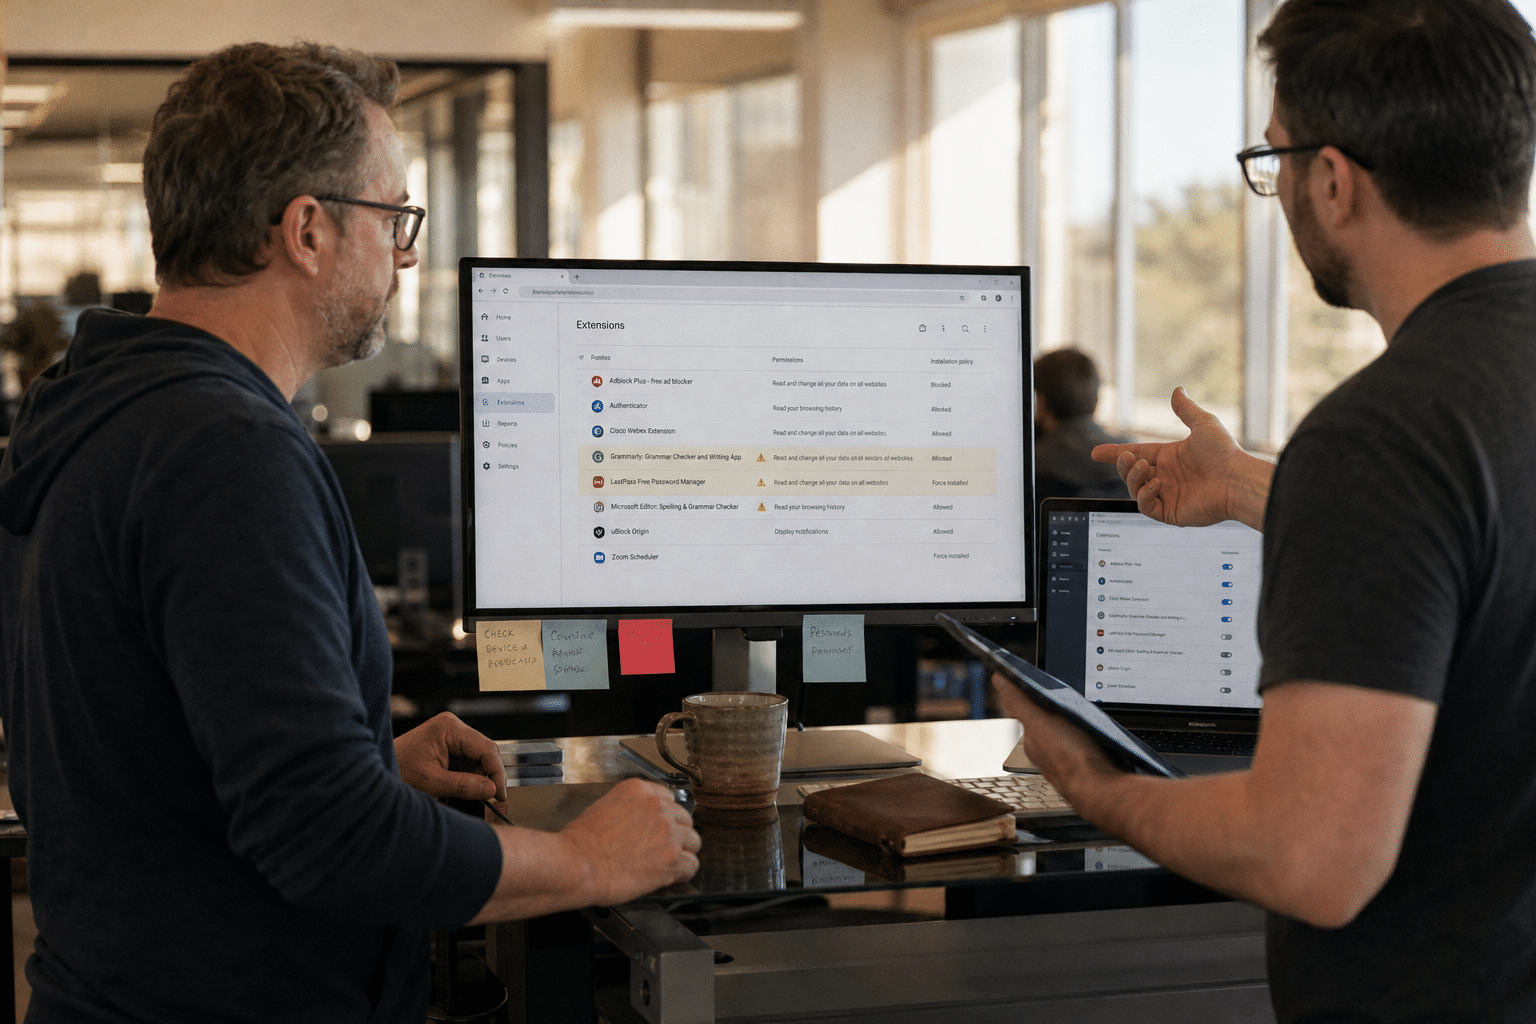
Malicious browser extensions are dangerous because they live inside the one application your staff keep open all day, with permission to read and change every page they visit. An extension that can read a page can read your Microsoft 365 inbox, your banking portal and your CRM, and it can copy the session tokens that keep those accounts logged in. In its ThreatsDay roundup of October 8, 2026, The Hacker News reported malicious code turning up in developer packages and editor extensions again, alongside exposed attacker tooling and a ransomware affiliate who cheated his own partners. The headline stories change every week. The lesson for a 50 to 500 person company does not: the browser is now a supply chain, and most firms we assess have never written down what is allowed into it. This article covers the six risks we find most often and the controls that close them.
Five Points to Hold Onto Before the Detail
Here is the short version our team gives clients when we first open their browser management console and find it empty.
- Every extension is third-party code with your login. It runs with the same access as the person using the browser, which usually means email, files and finance tools.
- Passing review once proves nothing later. Researchers at Koi described a campaign they call ShadyPanda in which extensions behaved cleanly for years, built a following, then received a malicious update. Koi estimated the reach at roughly 4.3 million browser instances.
- Stolen sessions skip MFA. A copied session cookie lets an attacker act as the user without a password or a second factor, so your MFA rollout does not cover this.
- Developers carry extra exposure. Code editors such as VS Code have their own extension marketplaces, and a poisoned editor extension can reach source code, cloud keys and deployment credentials.
- The fix is policy, not awareness alone. A managed allowlist pushed from Microsoft Intune, Google Admin or Group Policy stops most of this without asking anyone to judge code they cannot read.
Why Rogue Add-Ons Reach Work Machines
Rogue add-ons reach work machines because, by default, Chrome and Edge let any user install anything from the public store with two clicks and no approval. That default suits a home laptop. It does not suit a device that holds a signed-in Microsoft 365 session for your controller.
In the wild, we see three entry routes. The first is the helpful tool: a PDF converter, a screenshot utility, a coupon finder or an AI writing assistant someone installed to save ten minutes. The second is the inherited extension, installed years ago, now sold to a new owner who pushes an update. The third is the personal profile: an employee signs into Chrome with a personal Google account, syncs their home extensions, and brings every one of them onto the company laptop.
None of these routes involves a user doing anything they would recognise as risky. That is why we treat extension control as part of our managed security services rather than a training topic. Training helps people notice odd behaviour, but nobody on your staff can audit minified JavaScript, and they should not have to.
It also explains why this problem stays invisible. Endpoint antivirus tends to trust the browser process, firewalls see ordinary HTTPS traffic to ordinary cloud hosts, and the extension never drops a file that looks like malware. The first sign is often a mailbox rule nobody created, or an invoice paid to the wrong account.
The 6 Risks Malicious Browser Extensions Create
The six risks below are the ones we document most often during browser reviews, ordered roughly by how much damage each causes when it lands.
1. Session Token Theft That Bypasses MFA
Session token theft is the most damaging risk because a copied cookie lets an attacker reuse a live, already-authenticated session. Some argue that conditional access and short token lifetimes make this a small concern. Others point out that most SMB tenants still run default session lifetimes measured in days. Both views hold some truth: token binding and compliant-device rules shrink the window, but very few firms under 500 staff have turned them on. Until they do, an extension with access to cookies on login.microsoftonline.com is equivalent to a stolen password plus a stolen phone.
2. Silent Reading of Email, Files and CRM Records
Broad host permissions, shown in the store as “read and change all your data on all websites”, let an extension scrape whatever page is open. A study from Spin.AI found that about half of the extensions it reviewed posed a high risk to data held in Google Workspace and Microsoft 365. Some of that is overstated, since many tools request broad access out of laziness rather than intent. The counterpoint is that intent can change with a single update, and the permission was already granted.
3. Payment and Banking Page Manipulation
An extension that can change a page can change the account number shown on an invoice portal or inject a fake login prompt on your bank’s site. We have seen finance staff approve transfers on a page that looked perfect because the edit happened inside their own browser, after the bank’s security checks had already passed.
4. Poisoned Developer and Editor Extensions
The ThreatsDay roundup is a reminder that code editors are browsers for developers. A malicious VS Code extension can read workspace files, environment variables and saved cloud credentials. If you employ even one developer or outsource to an agency that works on your systems, their editor belongs in scope. The opposing view is that developers understand risk better than most staff. In practice they install more extensions than anyone, and they hold the most valuable keys.
5. Traffic Redirection and Malware Delivery
Extensions can rewrite links and redirect searches, pushing users to lookalike pages or to downloads that install a remote access tool. This is where browser risk joins ordinary phishing. DNS filtering that blocks malicious domains catches a share of these redirects, though not the ones hosted on legitimate cloud platforms.
6. Ownership Changes Nobody Sees
The quietest risk is the sale. Popular extensions with large user counts are bought by new owners, sometimes openly and sometimes through a shell company, and the next update ships to every installed copy automatically. Nothing on the device changes visibly. This is why a one-time cleanup decays within months unless something watches for permission changes and new publishers.
How to Find the Extensions Already Installed
You find the extensions already installed by pulling a device-level inventory from your management platform rather than asking staff what they use. People forget, and synced personal profiles hide entries nobody chose deliberately.
For Microsoft-managed fleets, Intune and Microsoft Defender for Endpoint can report browser extensions across Edge and Chrome, including the extension ID, version and requested permissions. For Google Workspace, the Chrome Browser Cloud Management console lists every extension on every enrolled browser. On unmanaged machines, the honest answer is that you cannot see them at all, which is itself a finding worth recording.
When we run this as part of a cyber security audit, we sort the results into four groups:
- Business-required and low permission, such as a password manager from your approved vendor. Keep and pin the version policy.
- Business-required and high permission, such as a CRM sidebar tool. Keep, but restrict it to the sites it needs with runtime host permissions.
- Personal convenience tools, such as shopping, weather or video downloaders. Remove.
- Unknown publisher or abandoned project, with no update in two years or a publisher using a free email address. Remove first, ask questions later.
The first inventory usually surprises leadership. A 120-person firm we reviewed this year averaged just under seven extensions per browser, and nobody in IT could name the purpose of a third of them.
Controls That Stop Malicious Browser Extensions
The control that stops rogue add-ons is a default-deny allowlist enforced by policy, so only approved extension IDs can install and everything else is blocked or removed automatically.
Build a Default-Deny Allowlist
In Chrome and Edge, the ExtensionInstallBlocklist policy set to “*” blocks everything, and ExtensionInstallAllowlist names the IDs you approve. Push both from Intune, Google Admin or Group Policy. Some teams worry this will flood the help desk with requests. In our experience the request volume spikes for about two weeks, then settles to a handful a month, and each request becomes a short documented review rather than a silent install.
Restrict Host Permissions and Block Personal Sync
Use the ExtensionSettings policy to limit approved extensions to the domains they need, and use runtime_blocked_hosts to keep every extension away from your identity provider, banking portals and payroll site. Disable sign-in with personal accounts on company browsers, or at least block sync of extensions from personal profiles. That single change removes the route most extensions use to arrive uninvited.
Watch for Permission Changes and New Publishers
Approval is a point in time, so pair it with monitoring. Pin approved extensions to reviewed versions where the business can tolerate it, and alert when an approved extension requests new permissions or changes publisher. Feed browser telemetry into the same place you review sign-in alerts, so network security monitoring can connect an odd extension update with an odd login from a new country an hour later. Keep the browser itself current too; our guide to browser security updates for business covers patch cadence.
What to Tell Your Staff About Extensions
Staff need two plain messages: do not install extensions yourself, and report anything that changes how your browser behaves. Long lectures about JavaScript permissions do not stick, and they push responsibility onto people who cannot evaluate it.
Fold extensions into the same habit you build for suspicious links. Our article on training employees to spot malicious SharePoint links uses the same pattern: a short rule, a clear reporting channel, and no blame for asking. Signs worth reporting include a new toolbar or sidebar, a changed search engine, unexpected pop-ups on sites that never had them, or a login prompt appearing on a page where the user was already signed in.
Treat AI browser assistants with particular care. Many request access to every page in order to summarise it, which is exactly the permission an attacker wants. The same goes for agentic tools that browse on a user’s behalf; how malicious websites target AI agents explains why those tools can be steered by the pages they read. Approve one assistant centrally rather than letting each department pick its own. Security awareness training works best when it reinforces a policy that already exists, rather than replacing it.
Frequently Asked Questions
Are malicious browser extensions a real risk for small businesses?
Yes, harmful add-ons affect small businesses as often as large ones, because they spread through public stores rather than targeted attacks. Smaller firms are often more exposed, since few run a managed allowlist or review extension permissions at all.
Does MFA protect us if an extension steals a session?
No, MFA does not stop session theft, because the attacker reuses a session that already completed MFA. Conditional access rules that require a compliant device, shorter session lifetimes and token protection features reduce that window.
How do we check which extensions our staff have installed?
You check installed extensions through Microsoft Intune, Defender for Endpoint or Chrome Browser Cloud Management, which report every extension on enrolled browsers. Machines that are not enrolled cannot be inventoried reliably, which is a reason to enrol them.
Should we block all extensions?
Blocking everything by default and approving a short list is the approach we recommend for most firms. A total ban without exceptions tends to push staff toward workarounds, while a reviewed allowlist keeps the tools people genuinely need.
Do code editor extensions need the same controls?
Yes, editor extensions in tools such as VS Code carry similar or higher risk, since they can reach source code and cloud credentials. Apply an approved list to developer machines and include outside agencies in that requirement.
Who Is Behind This Advice
Mindcore has spent years managing endpoints, identity and email security for growing firms across New Jersey, Florida and beyond, and browser control has moved from a footnote to one of the first things we check. The patterns in this article come from that work: inventories that surprise leadership, extensions with no clear owner, and session theft that slipped past MFA. Our role is to give your team the policy and visibility to decide what runs in its browsers, so you stay in control of that choice. Mindcore is led by CEO Matt Rosenthal, who focuses on helping mid-sized businesses close the security gaps that attackers reach first.
Get Your Browser Fleet Under Control
Harmful add-ons succeed because the browser grew into the most trusted application on every desk while the rules around it stayed at their home-user defaults. The fix is not a heroic cleanup. It is an inventory you can trust, a default-deny allowlist enforced by policy, host permissions that keep extensions away from identity and payment pages, and monitoring that notices when an approved tool changes owner or asks for more. Firms that put those four pieces in place stop treating each new headline as a fresh emergency, because the next poisoned extension simply cannot install. If you want a clear picture of what is running in your browsers today and a policy your team can enforce from Intune or Google Admin, book a free strategy call and we will walk through it with you.

