Most providers know their security stack has grown past what it needs to be. Far fewer can say, on a Tuesday, how many products are billed per seat across the same 4,000 endpoints, which two of them raise an alert on the same event, and what it would cost to leave any one of them before its term ends. Consolidation is discussed as a security architecture question and settled as a commercial one, and the analysis that changes the outcome is an inventory of overlapping spend and exit cost rather than a capability matrix. The tooling in this category is useful to the extent it produces that inventory from systems you already run.
Overview: 5 Questions Consolidation Has to Answer
- What overlaps, specifically. Two products claiming endpoint detection are not necessarily redundant. Two products billing per endpoint for the same detection are.
- What does each contract cost to leave. Minimum commitments, remaining term, and data export terms decide sequencing more than product quality does.
- Which alerts arrive twice. Duplicate alerting inflates workload and hides the signal, and it is measurable from ticket data rather than from a vendor claim.
- What breaks in the integrations. A product removed from the stack takes its connectors with it, and something downstream was consuming them.
- What is the concentration risk of the result. A single platform covering endpoint, identity, email and network is efficient until its own outage or compromise becomes yours.
Why Security Stacks Accumulate Past the Point of Usefulness
Security stacks grow because every addition was justified individually and nothing triggers a review of the whole. A client incident adds a product, a compliance requirement adds another, a vendor promotion makes a third cheap for a year. Each decision was defensible and the total was never decided by anyone. Our cybersecurity practice starts consolidation work with the inventory rather than the architecture for that reason.
Overlapping coverage is easy to assert and hard to prove
Three products in a typical stack will each claim to stop ransomware. Whether they actually overlap depends on where each sits, what telemetry it uses, and what it does on detection, which is not answerable from a feature grid. A DNS filter and an endpoint agent both stopping a malicious download are doing different work at different points, and dropping either changes the outcome in some scenarios.
The argument for keeping apparent overlap is defence in depth, and it is a real principle rather than a justification. Layers exist so that one failure is not total, and a provider who consolidates to a single control point has removed a layer, whatever the vendor calls the product.
The distinction that resolves it is whether the layers are independent. Two agents from the same vendor sharing a detection engine are not two layers, they are one layer billed twice. Two products from different vendors using different telemetry genuinely are two. Map each product to what it observes and what it can block rather than to its category name, and the real overlaps become obvious. Our overview of AI cybersecurity tools covers where the current products genuinely differ.
Duplicate alerting is a measurable cost nobody measures
When two products alert on the same event, the service desk handles it twice, or worse, handles it once and closes the second as a duplicate without checking that it was. Over a year across a client base that is a meaningful number of hours, and it is recoverable from your own ticket data by correlating alerts on time, host, and indicator.
Some engineers argue duplicate alerts are a useful confirmation signal, and in a mature security operation with correlation in place that can be true. The confirmation has value when something consumes it deliberately.
Where nothing correlates them, the second alert is pure cost and it degrades attention for the alerts that matter. Measuring the duplication rate before consolidating gives you a number for the business case that is yours rather than a vendor’s, and it often turns out to be the largest single saving. This is the same operational discipline that makes a vulnerability management process work: measure the queue before changing what feeds it.
Exit terms decide sequencing more than product quality
The best product to remove is rarely the one you can remove next. Annual commitments renew on different dates, several vendors require notice, and some hold your historical detection data in a form you cannot export cleanly. A consolidation plan built purely on capability produces a sequence the contracts will not permit.
There is a case for paying to exit early where a product is genuinely harmful to operations, and occasionally that is right. It is an expensive decision and it should be made knowingly rather than discovered halfway through a migration.
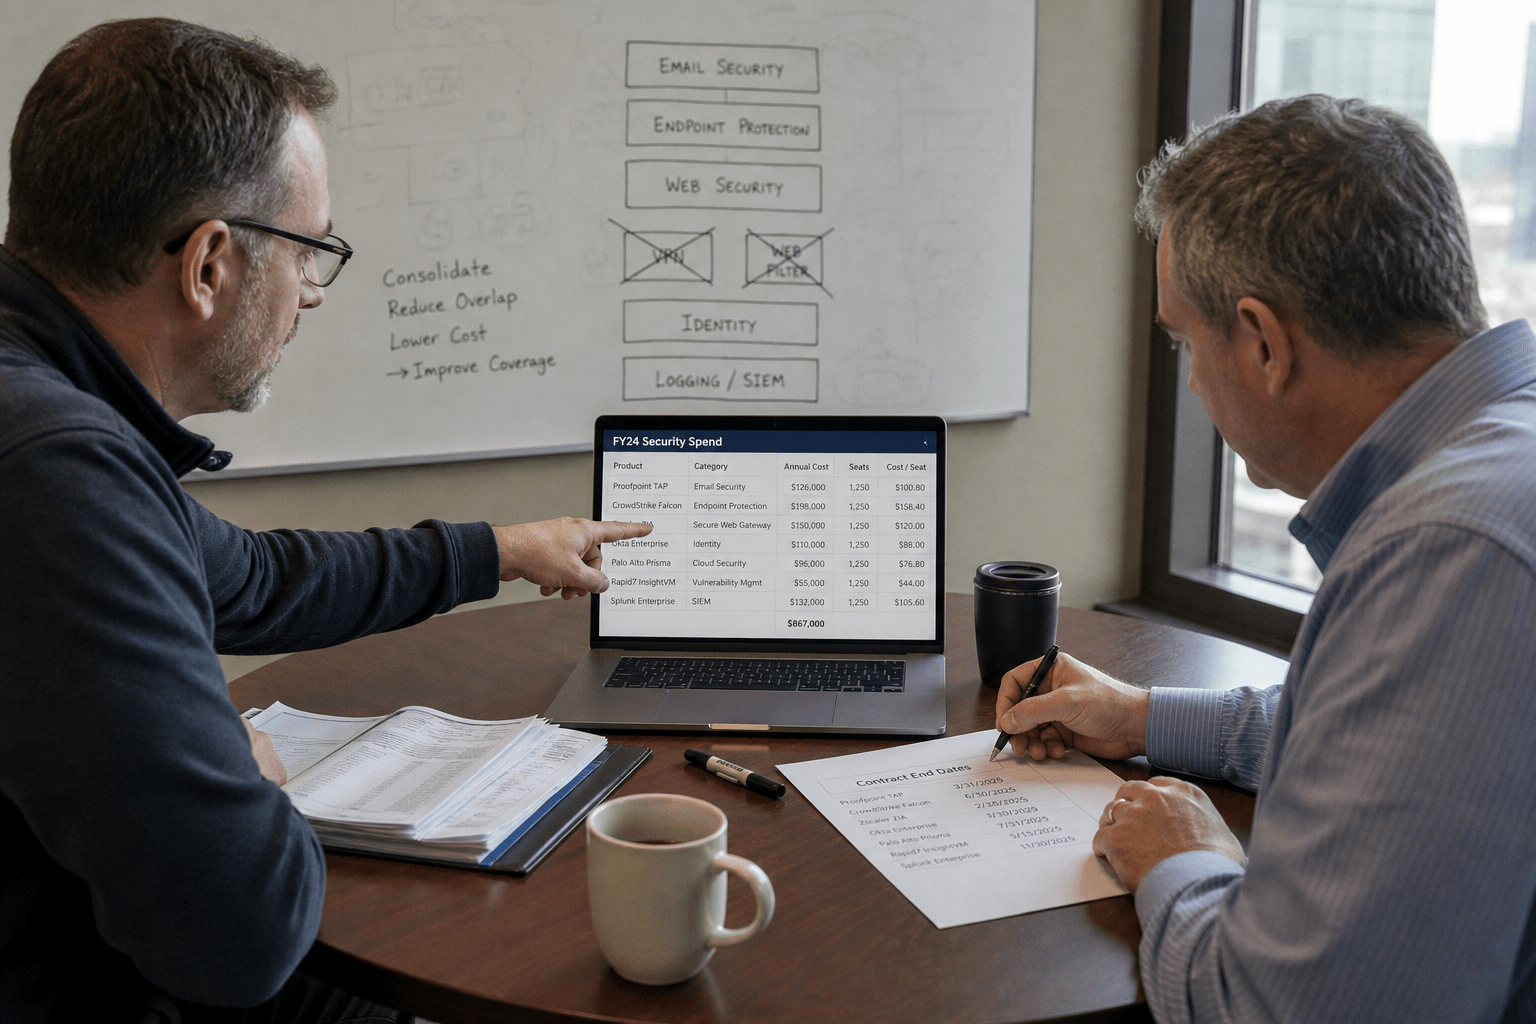
Build the contract calendar first: term end, notice period, minimum commitment, and data export terms for every security product in the stack. That single table usually reorders the whole plan, and it is the artefact most providers do not have. Tooling helps here by extracting those terms from the agreements themselves, which is the same extraction problem as any contract review and is well handled now.
Historical detection data is the clause people read last and regret first. If a product holds a year of alert history and its export is a paginated interface with no bulk option, you either leave the history behind or spend a week retrieving it. That matters for a client under an obligation to retain security records, and it matters again the first time an incident investigation needs to ask what was happening on a host eight months ago. Establish the export format and the retention window before signing anything new, and treat a vendor who cannot answer as having priced the answer into your next renewal.
Where Automation Helps a Consolidation Project
Three places, and none of them is choosing the product. That decision needs judgement about your client base and your team’s skills.
Building the overlap and spend inventory
Joining the license records from your distributor or vendor portals against the endpoint inventory tells you how many seats of each product you are paying for and where they land on the same machines. Done manually this is a week of spreadsheet work that is stale on delivery. Automated, it is a live view, and the surprises are consistent: seats billed for decommissioned devices, products still licensed for a client who left, and two agents on the same endpoints across a subset of the fleet.
The limitation is that vendor portals differ wildly in what they expose, and some give you a monthly invoice rather than an API. Expect a hybrid where the largest three or four vendors are automated and the tail is maintained by hand. That is still a large improvement over nothing, and the tail is usually the small spend.
Reconciling the seat count against what you bill the client is the second half of the same exercise, and it is the half that finds money. Providers commonly discover a client billed for 90 security seats while 104 are deployed, or the reverse, because the two counts are maintained in different systems by different people on different schedules. Neither direction is comfortable, and both are cheaper to correct when you found them than when a client’s finance team did. Run that comparison monthly once the inventory is automated, since the effort after setup is near zero and the drift restarts the moment onboarding resumes.
Correlating alerts to measure genuine duplication
Pulling alerts from each product with host, timestamp, and indicator, then clustering them, gives the duplication rate directly. This is a narrow, verifiable analysis, and it is the kind of correlation work automation does well because the volume defeats manual review.
Be careful about what counts as duplication. Two alerts on the same host within a minute for the same file hash are duplicates. Two alerts on the same host within an hour for different behaviours may be one intrusion progressing, and treating those as duplicates is exactly the wrong lesson to draw. Set the clustering rules deliberately and review a sample by hand before trusting the number. Providers running a formal service will recognise this as the same tuning problem that managed security services face continuously.
Modelling the margin effect before committing
The commercial case is arithmetic: current cost per seat per client against the consolidated cost, with migration effort and any early exit fees amortised across the term. It is not complicated, and it is frequently not done, because the inputs sit in three systems. Automating the inputs makes the model something you can re-run when a vendor changes pricing rather than a one time exercise that ages immediately.
What the model will not tell you is the retention effect. Clients notice a stack change, particularly one that replaces a product they recognise, and that conversation has a cost that does not appear in any spreadsheet. Plan the client communication as part of the project rather than as an afterthought, and lead with what improves rather than what is being removed.
Pricing structure deserves a line in the model of its own. Moving from several per seat products to one platform frequently shifts you into a tier with a minimum commitment, which is a different risk profile: a client loss that previously reduced your cost proportionally now leaves you carrying unused capacity until renewal. Model the consolidated cost at your current seat count and again at 80 percent of it, since the second number tells you what a normal year of churn does to the margin you are buying. Providers who skip that step tend to discover the shape of the commitment during their first bad quarter. Our look at managed IT services software covers how the rest of the operational stack fits around this.
How to Judge a Consolidation Move Before Committing
Four tests. Does removing this product remove an independent layer, or a duplicated one. What does the contract cost to leave and when is the earliest clean exit. What consumes this product’s integrations today, and what happens to those. What is the concentration risk in the result, and what is your plan for the day that single vendor has an outage.
The fourth question has become more pressing as platform vendors extend across categories. A single platform covering endpoint, identity, email and network is operationally simpler and commercially attractive, and it also means one vendor’s bad update or breach is your whole security posture. That is not an argument against consolidation, it is an argument for deciding the floor deliberately: which two or three layers stay independent regardless of what any platform offers. Providers under formal obligations should check that decision against their compliance requirements, since some frameworks expect specific separations. The long running pattern of MSPs rebuilding their stack every few years is one we wrote about in our piece on cybersecurity trends MSPs must address, and the underlying dynamic has not changed.
Frequently Asked Questions
How many security products should an MSP stack contain?
There is no correct number, and any vendor offering one is selling. The useful test is whether each product covers a layer nothing else covers, and whether you can explain what it does that its neighbours do not. Most stacks fail that test on two or three products.
Does consolidation reduce security?
It reduces security if it removes independent layers and improves it if it removes duplicated ones. The difference lies in whether the products shared telemetry and a detection engine, not in how many logos are on the diagram.
What is the biggest hidden cost of consolidating?
Migration labour, almost always. Agent removal, policy rebuilding, and client communication across a fleet consume more hours than the planning suggests, and the removal of an old agent is frequently messier than the installation of the new one.
How do we handle a client who insists on a specific product?
Price it as a client specific exception rather than absorbing it into the standard stack. That keeps the standard clean, makes the cost visible to the client, and avoids one client’s preference quietly becoming everybody’s baseline.
Can we consolidate and keep defence in depth?
Yes, by choosing which layers must stay independent before evaluating platforms. Most providers settle on keeping email security or DNS filtering separate from the endpoint platform, so a single vendor failure does not remove every control at once.
The Team Behind This Guidance
Our team has run these consolidations and inherited the results of ones done badly, which shapes the order we work in. The inventory and the contract calendar come first, because a plan that ignores either produces a sequence that stalls at the first renewal date. The capability comparison, which is where most projects start, is the part that turns out to matter least once the overlaps are actually mapped. Matt Rosenthal, our chief executive, keeps the practice focused on operational resilience for growing firms, which here means a stack a provider can explain, afford, and still defend after the consolidation is finished.
Start With the Contract Calendar
Before any product comparison, build one table: every security product in your stack, its term end, its notice period, its minimum commitment, and what happens to your data when you leave. It takes a day, it needs no software, and it will change your plan. Most providers discover that the product they most want to remove is locked for another 14 months, and that a product they had not considered removing expires next quarter with no notice required.
If you want a second opinion on that table, or help measuring the duplication rate across your current alerting before you commit to a direction, book a free strategy call with our team.