

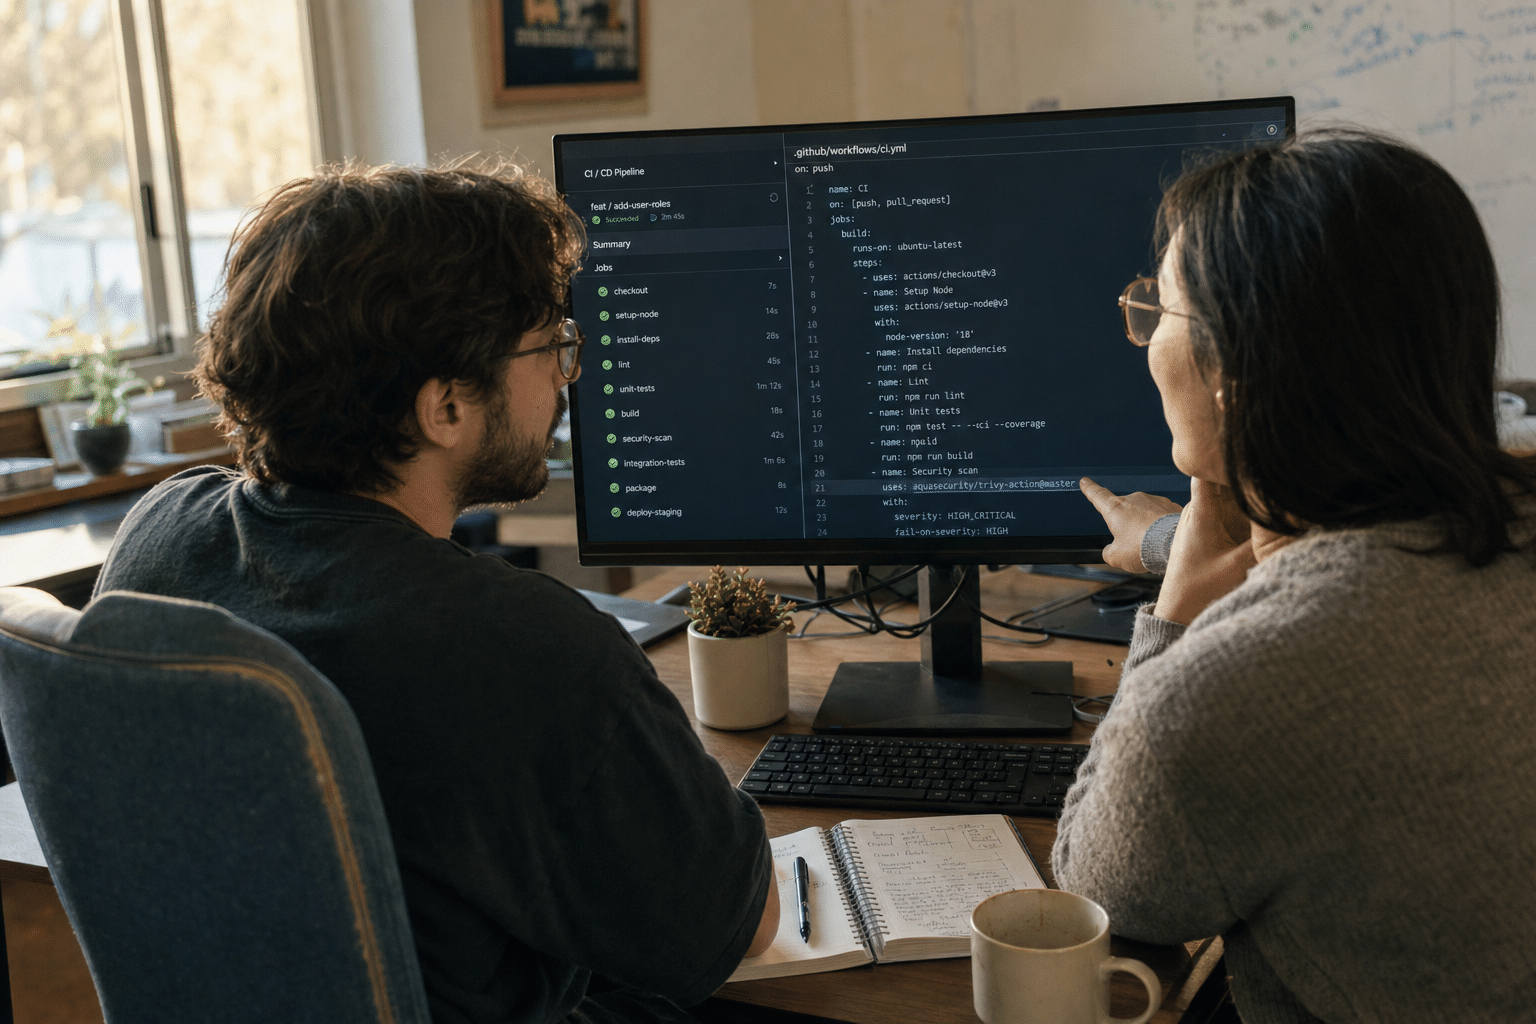
GitHub Actions secrets are the passwords, cloud keys and deployment tokens your build pipeline uses to ship software, and in October 2026 attackers showed how cheaply they can be stolen. Security researchers at StepSecurity, as reported by The Hacker News, traced a campaign that hijacked two well-known open-source maintainer accounts and pushed a malicious workflow file into more than 340 repositories. Using the account of the author of a popular Python game engine, the attacker pushed that workflow to 27 repositories in one burst. Nobody rewrote the application code. The attacker added one YAML file, the pipeline ran it with full trust, and the secrets walked out. If your company pays in-house or contracted developers to build anything on GitHub, the lesson is not “watch the news.” It is to measure how much your pipeline trusts any committer, and how much a single run can read.
Overview: Five Things Every Business Owner Should Know
These five points summarize the article for owners, operations leaders and IT managers at companies with 10 to 500 employees that build or customize software on GitHub, either with their own staff or through an outside development firm.
- The workflow file is the attack surface. A change to the
.github/workflowsfolder runs code on your build servers with access to your secrets. It deserves the same review as a payment change. - A trusted account is not a trusted change. The October campaign worked because commits came from real, respected maintainer accounts. Account reputation proved nothing.
- Secret scope decides the size of the loss. A pipeline holding an all-powerful cloud key loses everything in one run. A pipeline holding a narrow, short-lived credential loses very little.
- Third-party actions are code you did not write. Every
uses:line pulls someone else’s software into your pipeline, and a moved tag can change what runs without anyone touching your repository. - Your development vendor owns half of this risk. If an agency or freelancer has write access to your repositories, their account hygiene is now your security posture, and you should ask them about it in writing.
Why GitHub Actions Secrets Became the Target
GitHub Actions secrets became the target because they sit at the one point where code, cloud access and automation meet, and most small teams never revisit how they were set up. When a developer first wires up automated deployment, the fastest path is to paste an administrator cloud key into the repository settings and move on. It works, the release ships, and that key quietly stays there for years.
Our team sees this pattern constantly in client assessments. A company hires a contractor to build a customer portal, the contractor connects GitHub to the cloud account, and two years later nobody inside the business can say which keys exist, what they can touch, or who could trigger a workflow that reads them. The campaign described above simply industrialized that gap. As we covered in our credential theft fixes for SMBs, stolen credentials are attractive because they skip every perimeter control you paid for.
Why a Single Workflow File Is Enough
A single workflow file is enough because GitHub runs whatever the workflow says, using the permissions and secrets the repository grants it. In agreement with that view, the attack required no exploit at all: commit access plus a file named something routine, such as a CI maintenance job, was sufficient. In opposition, some engineers argue that a branch protection rule requiring review stops this, and for protected branches that is often true. Both positions hold. Review helps where it is enforced, but many repositories allow pushes to unprotected branches, and certain triggers run workflows from those branches with secrets attached. The honest answer is that a workflow file is a program, and you should treat changes to it like a code deployment to production, because that is what they are.
Why Account Reputation Failed as a Control
Account reputation failed because the campaign used the real accounts of respected maintainers, so every signal a reviewer relies on looked normal. Supporters of trust-based review point out that most projects would never accept an unknown contributor’s workflow change, and that is fair. Critics answer that the risk here was never unknown contributors: it was a known account being used by someone else. Both are correct, and the takeaway for a business is concrete. Require phishing-resistant MFA, such as FIDO2 security keys, for every account with write access, including your vendor’s developers, and watch for workflow changes that arrive outside normal working patterns.
Why Attackers Prefer Pipelines Over Servers
Attackers prefer pipelines because a CI/CD run concentrates credentials that would otherwise be scattered across many systems. One view holds that a pipeline is just another server and should be hardened the same way. The opposing view is that pipelines are worse than servers, because they are designed to reach production, package registries and cloud consoles on purpose. The balanced position is that a pipeline is a privileged identity, and it should be inventoried, monitored and restricted like an administrator account. Our managed security services team treats build systems exactly that way during onboarding.
Risk 1: Secrets Scoped Far Wider Than the Job Needs
The first risk is scope: most small-company pipelines hold credentials that can do far more than the job that uses them. A workflow that uploads a static website needs permission to write one storage bucket. In practice we often find it holding a key that can create servers, read every database and change billing.
How Wide Scope Turns a Leak Into a Breach
Wide scope turns a leak into a breach because the attacker inherits everything the stolen credential can do. Some teams accept wide keys on the grounds that a leak of any key is serious, so narrowing it only changes details. Others argue that narrowing is the most valuable fix available, because it caps the damage before anything goes wrong. Both carry weight, yet the math favors narrowing: a key that can only write one bucket gives an attacker a defacement, while an administrator key gives them your whole cloud account.
What to Change This Quarter
Replace long-lived cloud keys with short-lived credentials issued per run. GitHub supports OpenID Connect federation with AWS, Azure and Google Cloud, so the pipeline requests a token that expires within the hour and is bound to a named repository and branch. Then set the default GITHUB_TOKEN permission to read-only at the organization level and grant write access per workflow, only where needed. Finally, split secrets by environment so a test workflow can never read production credentials.
Risk 2: Workflow Changes That Nobody Reviews
The second risk is that workflow files change without review, even in companies that review every line of application code. Pull request templates and reviewer habits focus on features, so a modified YAML file in a large change slides through.
Should Workflow Changes Need a Second Approver?
Workflow changes should usually need a second approver from someone who owns security, though there is a fair counterargument. Small teams say mandatory approvals slow releases and that a two-person shop cannot staff a separate reviewer. That concern is real. The workable middle path is a CODEOWNERS rule that assigns the .github/workflows folder to one named person or to your security provider, plus branch protection on the default branch. That adds review only where the danger lives, and leaves ordinary feature work untouched.
Which Triggers Deserve Extra Scrutiny
Triggers that run with secrets on code you have not reviewed deserve the most scrutiny, chiefly pull_request_target and workflow_run. Defenders of these triggers note they exist for legitimate jobs, such as labeling or commenting on outside contributions. Critics point out that they are the most common route to secret exposure in public repositories. The resolution is to allow them only in workflows that never check out or execute the contributor’s code, and to flag any new use of them during review.
Risk 3: Third-Party Actions Pinned to Moving Tags
The third risk lives in every uses: line, because third-party GitHub Actions referenced by a tag such as v3 can change underneath you. A tag is a pointer, and whoever controls the action’s repository can move it to new code at any time.
Tags Versus Commit Hashes
Pinning to a full commit hash is the stronger control, though it has a cost. Advocates of tags say they deliver security fixes automatically, which is true. Advocates of hashes say an automatic change is exactly what an attacker wants, and past incidents in which every tag of a popular action was repointed to malicious code support them. The balanced practice is to pin to commit hashes and let an automated dependency tool, such as Dependabot, propose updates you review. You keep fixes, and you see every change before it runs.
Reducing the Number of Actions You Trust
Reducing the number of third-party actions is the cheapest control available. Some developers prefer a marketplace action for every small task because it saves time. Others write a few lines of shell instead and avoid the dependency entirely. Both are reasonable, but each action is a vendor with access to your secrets. GitHub lets an organization allow only actions from verified creators or an explicit list, and we recommend turning that on. The same reasoning applies to package registries, which we discussed in our breakdown of the npm supply chain attack.
Risk 4: Secrets That Never Rotate and Logs Nobody Reads
The fourth risk is time: a secret that never rotates stays useful to an attacker indefinitely, and an attack nobody notices never gets stopped. In the October campaign, stolen secrets were sent to an outside server within the run itself, so the only record was the job log and the outbound connection.
How Often Should Pipeline Secrets Rotate?
Pipeline secrets should rotate at least every 90 days and immediately after any suspicious workflow change, although short-lived federated tokens make the question mostly disappear. Teams that resist rotation say it breaks deployments, and badly managed rotation does. The answer is to automate it or remove static secrets entirely. Either way, keep an inventory that lists each secret, its owner, what it can access and when it last changed.
What Good Monitoring Looks Like
Good monitoring means someone reviews workflow runs that make unexpected outbound connections, read secrets they normally do not, or run from new branches. Some argue small companies cannot afford this attention. Others counter that GitHub audit logs and a network egress filter on runners, such as StepSecurity Harden-Runner, cost little. Both hold depending on scale, and this is a common gap a vulnerability assessment will surface.
Risk 5: A Development Vendor You Have Never Audited
The fifth risk is your development partner, because an agency or freelancer with write access to your repositories carries your pipeline risk on their own accounts and laptops. If one of their developers is phished, the attacker gets the same access the October campaign used.
Questions to Ask Your Development Vendor
Ask your vendor these questions in writing, and expect clear answers:
- Do all developers with access to our repositories use phishing-resistant MFA?
- Which of our secrets exist in GitHub, who created them, and what can each one access?
- Are third-party actions pinned to commit hashes, and is workflow folder review enforced?
- How quickly do you remove access when a developer leaves your team?
- Will you notify us within 24 hours of any suspected account compromise?
Some owners worry that pressing a vendor this hard damages the relationship. A competent firm will welcome it, and a firm that cannot answer is telling you something. Our article on supply chain ransomware and vendor risk covers contract language that backs these questions up.
Testing Instead of Trusting
Testing the pipeline is the only way to confirm the answers you were given. A focused penetration testing engagement can attempt exactly what this campaign did: gain a developer foothold and see what secrets a workflow exposes. Pair it with the review practices in our cybersecurity audit mistakes guide so the test leads to fixes rather than a filed report. For the broader picture beyond pipelines, see our supply chain attacks guide for small businesses.
Frequently Asked Questions
What are GitHub Actions secrets?
These secrets are encrypted values, such as API keys, cloud credentials and deployment tokens, that a repository or organization stores for its automated workflows. They are masked in logs, but any workflow allowed to read them can use or send them elsewhere.
Can a malicious workflow steal secrets from a private repository?
Yes, a malicious workflow can steal secrets from a private repository if someone with write access, or a hijacked account, adds it to a branch that runs with secrets. Private visibility hides your code from the public, but it does not restrict what a workflow inside the repository can do.
Is pinning GitHub Actions to a commit hash really necessary?
Pinning to a full commit hash is the most reliable way to guarantee that the code you reviewed is the code that runs. Tags can be moved by whoever controls the action, so pin hashes and use an automated tool to propose reviewed updates.
What should we do first if we suspect a workflow leaked secrets?
Revoke and rotate every secret the affected workflow could read, starting with cloud and package-registry credentials. Then freeze the branch, preserve the Actions logs, review recent runs for unusual outbound connections and check cloud audit logs for actions taken with the stolen keys.
Does this matter if we only use an outside developer?
Yes, it matters more, because your exposure then depends on a vendor’s account security that you do not control. Confirm in writing who has access, how secrets are scoped and how the vendor will notify you of a compromise.
Who Is Behind This Guidance
Mindcore Technologies has spent years securing the systems small and midsize businesses depend on, and build pipelines are now part of that picture for any company shipping its own software or paying a firm to do it. Our security team reviews GitHub organizations, cloud identity and vendor access as one connected risk, because the October campaign proved they are one risk. The goal is to give your developers and your leadership a clear, prioritized list they can act on, not a stack of findings. Matt Rosenthal, Mindcore’s CEO, leads the company’s focus on practical, zero-trust security for growing businesses, the approach behind our ShieldHQ platform and our managed security work.
Close the Gaps in Your Pipeline Before an Attacker Finds Them
The October campaign did not need a clever exploit, only one trusted account and one workflow file. That is the durable lesson for any business building on GitHub: your real exposure is how much your pipeline trusts whoever commits, and how much a single run is allowed to read. Narrow every secret to the job that uses it and prefer short-lived tokens. Put workflow files under named review, pin third-party actions to commit hashes, rotate and inventory what remains, and hold your development vendor to the same standard in writing. None of these steps requires a large security team, but each one shrinks what a stolen account is worth. If you are not sure where your repositories stand today, our team can map your secrets, workflows and vendor access and hand you a short, ordered fix list. Book a free strategy call and we will walk through your pipeline with you.

