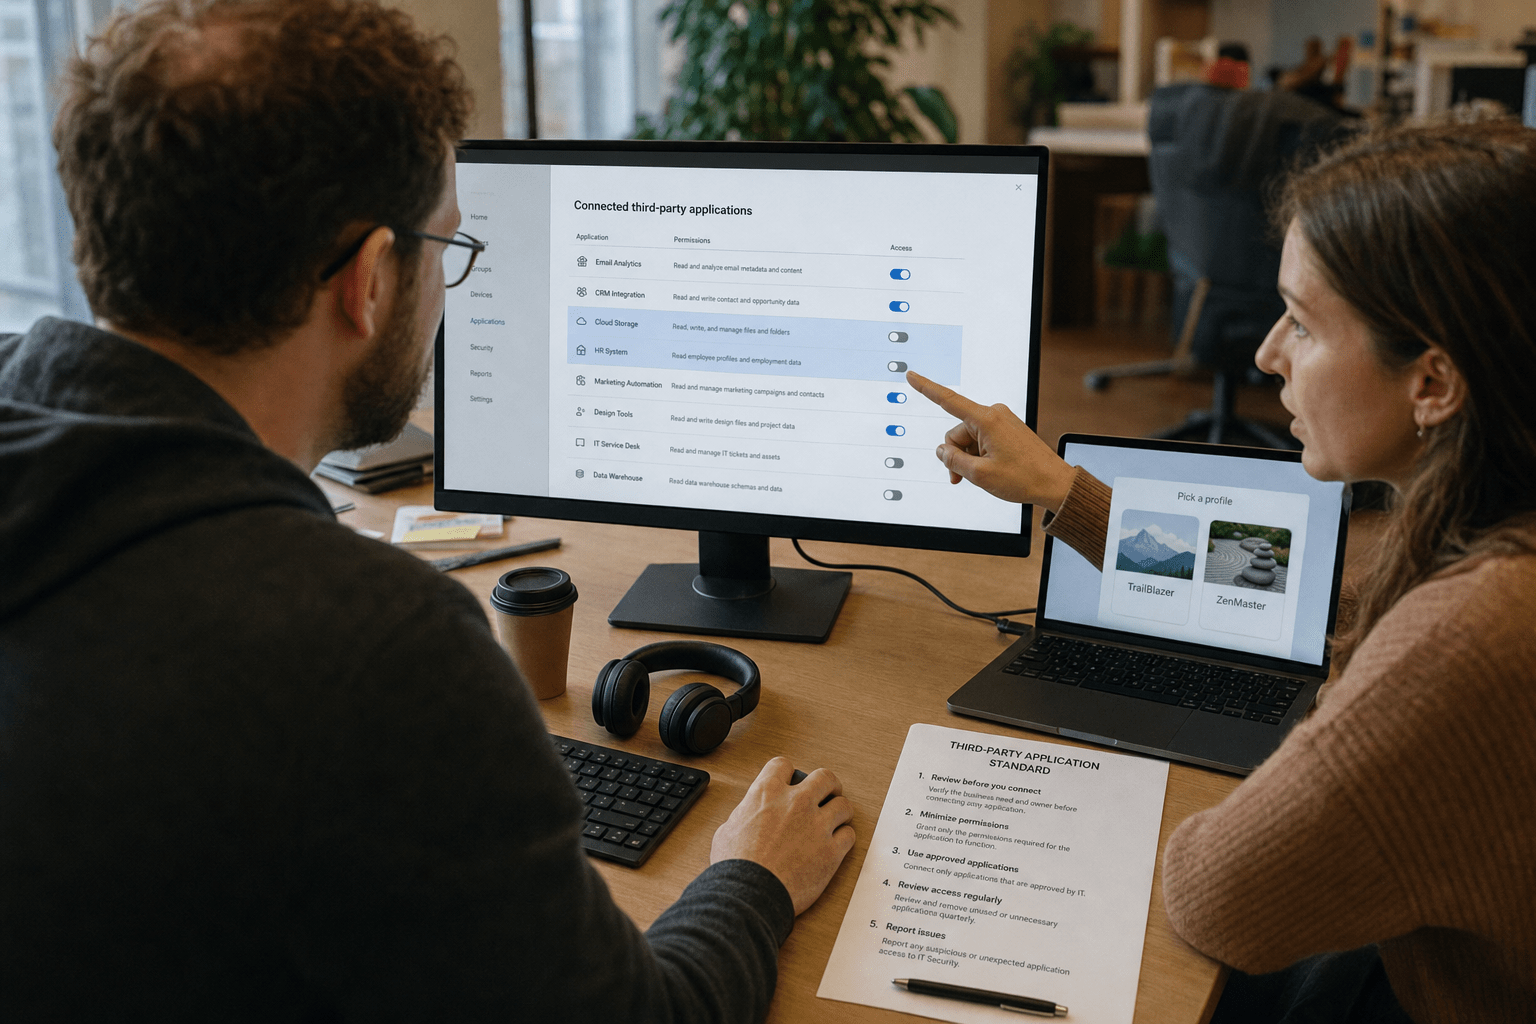
An AI browser agent works inside a browser that is already signed in to everything you use, which means it operates with your identity rather than with its own. Ask it to complete a task involving a third-party service and it will encounter the same consent screen a person would, the one listing what the application is requesting access to. A person pauses there. An agent treats it as an obstacle between itself and the goal you set, and clicking it is the obvious way through. The permission granted is real, standing, and indistinguishable in the audit log from one you granted deliberately. Very few businesses have thought about this before somebody installs one.
The Six Controls to Set Before Anyone Installs One
None of these require a product. All of them require a decision somebody has not yet made.
- Decide which browser profile an agent may use. The one signed in to your business systems should not be the one running autonomous tasks.
- Ban consent grants outright. State plainly that an agent may never accept terms or authorize access on the business’s behalf.
- Require admin consent for third-party applications. If users cannot grant access, an agent acting as a user cannot either.
- Control extension installation. Most of these tools arrive as a browser extension, which is a managed setting rather than a policy request.
- Separate agent work from privileged accounts. An administrator’s browser is the worst possible place for autonomous clicking.
- Write down what the agent may buy or send. Purchases, emails and form submissions need an explicit boundary before a task hits one.
Our note on the risks to settle before letting autonomous workflow agents run covers the same question for agents that operate outside a browser.
Why an AI Browser Agent Inherits More Than You Intended
The agent is not given access, it is placed inside a session that already has it, which is a different security model from every integration your business has bought before. When you connect a conventional application to your business systems, somebody approves a defined scope, and that approval is recorded and revocable. A browser agent skips all of that by operating the browser itself. Whatever your browser is signed in to, it can reach. Whatever your account can do, it can do. There is no scope to define because there was never an integration to define one for, which is precisely what makes these tools useful and precisely what makes them difficult to govern.
The Consent Screen Was the Last Human Check
Third-party application access exists in almost every business platform, and the only thing standing between a service and standing access to your data is a person reading a screen and deciding. That design assumption is now wrong wherever an agent is operating. The screen looks the same, the click is the same, and the resulting grant carries the same permissions as one a human considered for a minute. Worse, agents are goal-directed: a tool asked to complete a workflow will treat an authorization prompt as a step rather than as a decision, because that is what it is from the task’s perspective. Our note on what the Hugging Face agent attack means for business security covers the adjacent case where the agent itself is the target. The counterargument is that vendors are adding confirmation steps for consequential actions, and the better ones are. Those confirmations are a product feature that can be turned off, deferred, or absent in the next tool somebody installs.
Turn Off User Consent and the Problem Mostly Disappears
Requiring administrator approval for third-party application access removes this risk at the platform level rather than at the agent level, which is why it is the highest-value control here. If a user cannot grant an application access to business data, then an agent operating as that user cannot either, regardless of what it clicks. In most business platforms this is a single tenant-wide setting, and it is off by default because the default favors convenience. Turning it on generates a stream of approval requests in the first fortnight and then settles, because most of the volume is people connecting things they connect once. The objection is real: administrator-approved consent puts a bottleneck in front of staff who are trying to work, and a slow approval process pushes people toward unapproved alternatives. That is an argument for approving quickly rather than for leaving the gate open.
Where These Tools Actually Get Installed
Browser agents arrive as extensions installed by individuals, which means they are governed by whatever your extension policy is, and most businesses do not have one. The tool is genuinely useful, an employee installs it to save time on a repetitive task, and nobody is told. This is the same shape as every shadow software problem, with the important difference that the thing being installed operates your logged-in sessions rather than storing a file somewhere. Our note on browser security for business covers the wider management question, and extension control is the part of it that suddenly matters much more than it did.
Manage Extensions Rather Than Asking Nicely
Extension installation is a managed browser setting, so this is a configuration decision rather than a policy anyone has to remember. You can allow a defined list, block a defined list, or require approval. Given how quickly this category is moving, an allow list is the only approach that holds, since a block list is out of date the week a new tool launches. That will feel heavy-handed to staff who are used to installing what they like, and it is worth pairing with a genuinely fast approval path so the control does not become a reason to work around it. The reasonable objection is that locking down extensions hurts productivity in a business that runs on browser tooling. Our position is that an allow list with a same-day approval turnaround costs very little, and that the alternative is an unknown number of tools operating your sessions.
Give Agent Work Its Own Profile
Running agent tasks in a separate browser profile signed in to nothing important is the cheapest structural control available, and it takes minutes to set up. A second profile, signed in only to what a given task genuinely needs, means the agent’s reach is bounded by design rather than by its own restraint. That is the same reasoning we apply to administrative accounts and it transfers cleanly. Staff will find it mildly annoying and will forget which window they are in, which is an argument for making the profiles visually distinct rather than for abandoning the separation. Our guidance on implementing agents in a local business and on custom agent development both end up at the same principle: bound what the thing can reach before you tune what it can do.
Actions That Should Never Be Autonomous
Some categories of action need a human regardless of how capable the agent is, and naming them in advance is easier than adjudicating them afterward. Spending money. Sending external communication. Submitting a form that creates a legal or contractual obligation. Deleting anything. Granting access to anybody. Those five cover the overwhelming majority of the outcomes a business would consider unacceptable, and they are easy to write into a one-page standard that people actually read. What makes this work is deciding the list before somebody is mid-task and improvising.
Say It in the Tool and in the Instruction
A rule that exists only in a policy document is not reaching the point where the decision happens, so put the boundary in the instruction you give the agent as well as in the standard. Most of these tools accept persistent instructions or a system-level preamble, and stating plainly that it must stop and ask before authorizing access, spending money, or sending external messages costs one line and applies to every task afterward. It is not a guarantee, since instruction-following is probabilistic and can be overridden by content the agent encounters, which is why it sits alongside the platform controls rather than replacing them. The counterargument that instructions are unreliable is correct and is not a reason to omit them, because a control that works most of the time layered on top of one that works structurally is a better position than either alone. Our note on the blind spots in AI vendor review covers what to ask a vendor about their own guardrails.
Review the Consent List Monthly Until You Trust the Controls
Checking which third-party applications hold access to your business data, monthly at first, is how you find out whether any of this is working. The list lives in your platform’s administration console and reading it takes ten minutes. What you are looking for is anything nobody can explain, which is the signal that a grant happened without a decision. Once two or three months pass with no surprises, drop to quarterly. This is deliberately a detective control rather than a preventive one, because the preventive controls above can be misconfigured and nobody would know, and our Copilot Studio governance guidance makes the same argument about verifying that a setting you turned on is still on.
Decide How You Will Tell an Agent’s Actions From a Person’s
Your audit logs will not distinguish the two, so if you want that distinction you have to create it rather than expect it. Every action an agent takes in a browser session is recorded as the signed-in user doing it, at a normal time, from a normal device. There is no agent field, no separate identity, and no marker in the record. That matters the first time somebody asks who approved a change, because the honest answer is that the log says a person did and nobody can confirm whether they were at the keyboard.
The practical fix is the separate profile again, this time for a second reason. If agent work runs under a distinct account rather than a distinct profile, the log answers the question by itself, and for tasks that touch systems where attribution matters, that is worth the extra setup. For lower-stakes work a profile is enough, paired with the habit of noting in a ticket or a shared channel when an agent ran a task against a business system. That sounds like bureaucracy and mostly it is, which is why it should apply narrowly. The objection that nobody will maintain a manual note is well founded, and it argues for the separate account wherever the question would actually be asked, rather than for a logging convention everyone abandons by March.
Frequently Asked Questions
What makes a browser agent different from a normal integration?
An integration is granted a defined, revocable scope. A browser agent operates inside a session that is already signed in, so its reach is whatever your account can do, with no scope anyone approved.
Can an agent really grant a third party access to our data?
If your platform allows users to consent to third-party applications, then yes, since the agent acts as the user. Requiring administrator approval for consent removes the path entirely.
How do we stop staff installing these tools?
Extension installation is a managed browser setting. An allow list with a fast approval path works better than a block list, because a block list is out of date as soon as a new tool launches.
Is telling the agent not to do something enough?
No, but it is worth doing. Instructions are probabilistic and can be influenced by content the agent reads, so they belong alongside platform controls rather than instead of them.
What should we check to know if this has already happened?
Your platform’s list of third-party applications with access. Anything nobody can account for suggests a grant occurred without a decision.
Who You Are Taking This Advice From
Mindcore deploys agent tooling for businesses and then has to live with the governance afterward, which is why we set the consent and extension controls before anyone installs anything rather than after the first surprise. We turn off user consent, build the allow list with a same-day approval path, split agent work onto its own browser profile, and put the monthly consent review in somebody’s calendar, and the guidance above comes from rollouts we have run rather than from a vendor’s safety page. Matt Rosenthal, who leads Mindcore, keeps the firm focused on bounding what a tool can reach rather than on predicting how it will behave, which for browser agents means the profile and the consent setting do the work. You decide what the agents are for. Our job is to make sure they cannot sign anything on your behalf.
Your Next Move Before Someone Installs One
Assume somebody in your business is already using one, because in most firms we assess somebody is. Open your platform’s administration console and read the list of third-party applications that hold access to your data, looking for anything nobody can explain. Then change the setting that lets ordinary users grant that access, and commit to approving requests the same day so the control does not breed workarounds. Set your browser extension policy to an allow list while the category is moving this fast. Create a separate browser profile for agent work and make it visually obvious, so nobody runs an autonomous task in the window signed in to your finance system. Finally, write the five-line list of actions that always need a human, put it in the agent’s persistent instructions as well as your standard, and diary the consent review monthly. None of that slows down the useful work these tools do. All of it stops the one outcome nobody wants, which is discovering that something was authorized on your behalf and nobody chose it. If you want help setting the controls before a rollout, book a free strategy call and we will start with your consent settings.