The best AI agents for employee onboarding are the ones that own the whole identity lifecycle, not the ones that send a good welcome email. New-hire experience is the part that gets demonstrated, and it is the part a determined HR coordinator can already do well with a checklist. What a checklist cannot do is guarantee that the accounts created on day one are the accounts removed on the last day, eighteen months later, when the person leaving reported to a manager who has also left. Provisioning and deprovisioning are two halves of one record, and the products worth buying treat them that way. Judge these agents on the leaver path.
Why Onboarding Breaks in the Second Month, Not the First
Onboarding problems rarely show up in week one, because week one has everyone’s attention. The damage accumulates afterward. Five patterns account for most of what we find during access reviews:
- Access is copied from a colleague. The fastest way to provision a new starter is to mirror somebody similar, which inherits every permission that person accumulated over four years.
- Nobody records why an account exists. Six months later there is no way to tell a deliberate grant from an accidental one, so nothing gets removed.
- Movers are treated as joiners. An internal transfer gains the new team’s access and keeps the old team’s, and internal movement is more common than joining.
- Contractors have no end date in the system. The engagement ended in March and the account is still active in November because nothing was scheduled to close it.
- The leaver process depends on HR telling IT. That notification is manual, and it is the step most likely to be late during a difficult departure.
Every one of these is a records problem rather than a workflow problem, which is why buying a better workflow tool often changes very little. Our piece on AI and employee management covers the wider people-operations picture.
Provisioning Correctly Rather Than Quickly
Provisioning speed is easy to demonstrate and easy to get wrong. Our team looks at three questions before anything else: where the role definition comes from, whether the agent can act across every system rather than the two it integrates with, and what it records about each grant.
Roles From an Actual Definition, Not From Copying a Colleague
Role-based provisioning is the difference between an onboarding agent and a fast way to spread access sprawl. In favour: an agent driven by role definitions creates exactly the accounts and group memberships that role requires, so two people hired into the same job get identical access, and the definition is a document somebody can review. That reviewability is what makes an access audit tractable later.
Against, and this is the honest obstacle: most mid-sized firms do not have role definitions, and building them is weeks of work with department heads who have other priorities. The temptation is to derive roles automatically from what existing staff have, which reproduces the sprawl you were trying to fix and gives it the authority of a system. We start clients with the five or six highest-volume roles rather than attempting the whole organisation, and we derive those from what the job actually needs, checked with the manager, not from a permission dump. Partial coverage done properly beats complete coverage derived from the mess.
Acting Across Every System, Including the Ones With No API
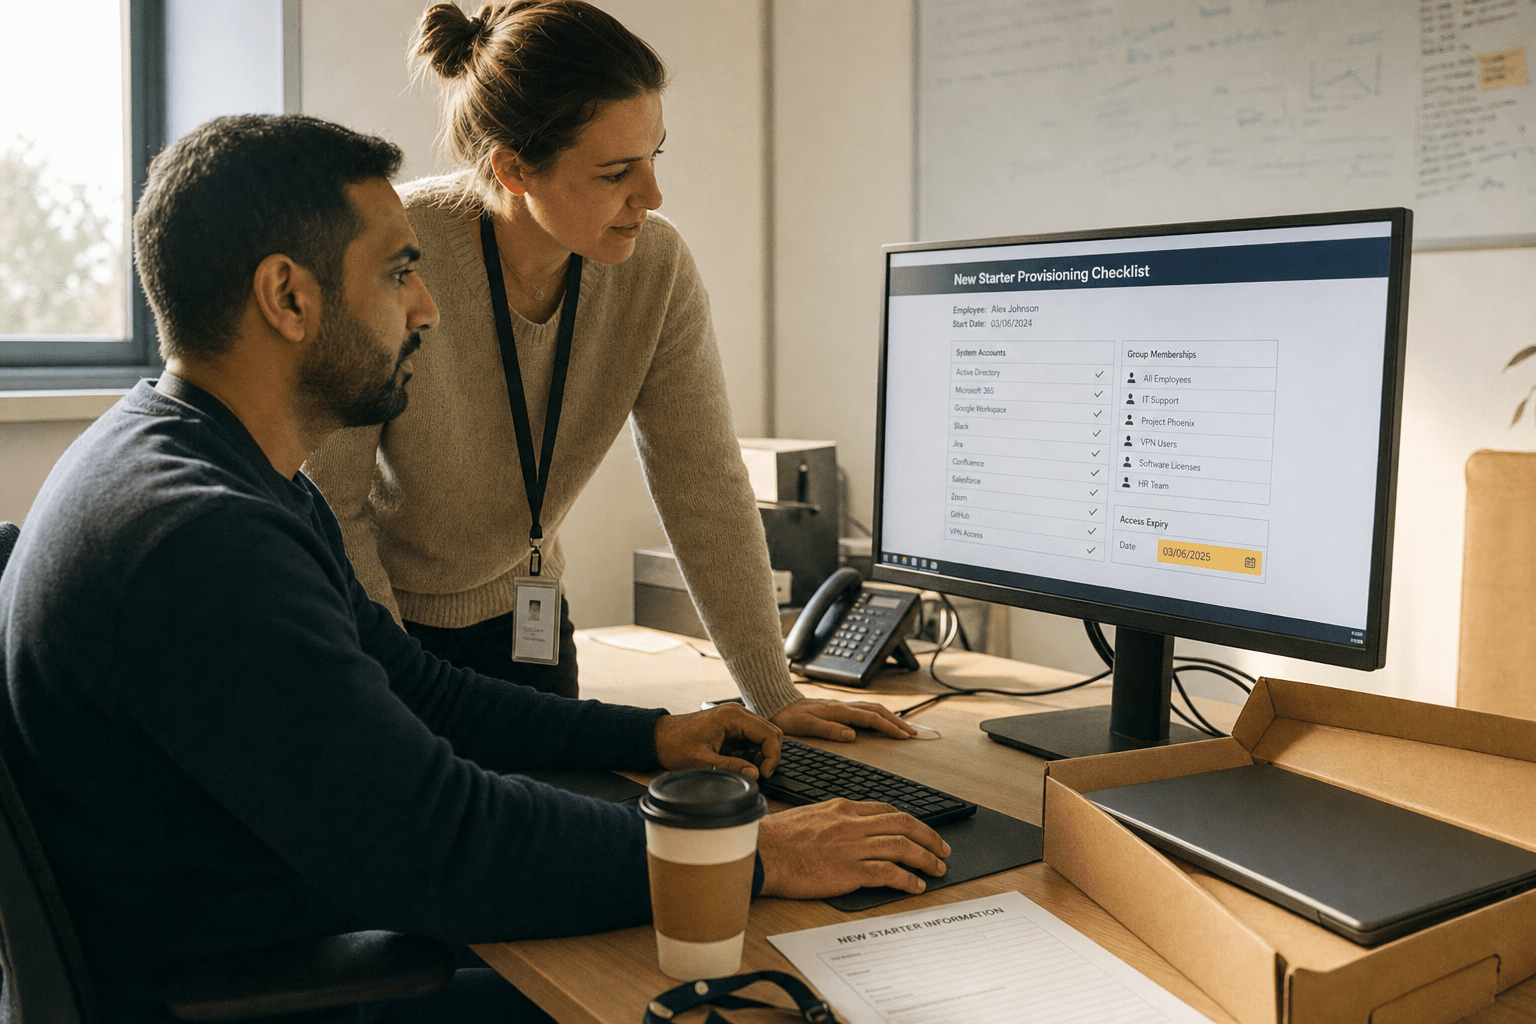
Breadth of reach determines whether automation removes work or relocates it. Supporting agent-based provisioning: for cloud identity, the main productivity suite, and mainstream SaaS with proper APIs, an agent can create, group, licence, and enrol a device in minutes, and it does so identically every time.
The limitation is the long tail, and the tail is where the effort has always been. The practice management system with no API, the vendor portal where accounts are created by emailing a support desk, the legacy application with a per-seat licence file. An agent that handles eighty percent of systems and silently ignores the rest produces a new starter who appears fully provisioned and cannot do their job. We insist that unhandled systems generate an explicit task with an owner rather than being absent from the workflow, because a visible manual step is fine and an invisible gap is not. That distinction is the same one we draw in our write-up on AI agents for IT operations.
Recording Why Each Grant Happened
Grant provenance is the record that makes everything downstream possible, and almost nothing captures it by default. Arguing for it: if every permission carries the role that justified it and the date it was applied, then a later access review can separate deliberate grants from exceptions, and the exceptions are a short list rather than the whole estate. Reviews stop being an archaeology exercise.
Against expecting perfection: exceptions get granted in a hurry, often verbally, and a system that makes recording the reason burdensome will simply be bypassed by an administrator with the rights to do it directly. We keep the exception path deliberately fast, with a required expiry date rather than a required justification, on the reasoning that a grant which expires cannot become permanent sprawl even if nobody wrote down why it happened. Expiry is the control that survives human shortcuts.
The Leaver Path Is Where the Value Is
Deprovisioning is the half of the lifecycle that carries genuine risk, and it is chronically under-built because nobody demonstrates it in a sales meeting. A departure is a security event, an access review trigger, and a compliance artifact all at once.
Closing Every Account Opened, Because You Know Which Ones They Were
Complete deprovisioning is only possible when provisioning was recorded. In favour of the lifecycle approach: an agent that created the accounts holds the list, so closing them is deterministic rather than a search. It can also produce the evidence, a dated record showing what was disabled and when, which is exactly what an auditor asks for and what most firms reconstruct by hand.
Against assuming completeness: accounts created outside the agent, before it was deployed or by an administrator working directly, are invisible to it. A leaver report that lists nine closed accounts looks authoritative and says nothing about the three it never knew about. We pair automated closure with a periodic reconciliation against directory and SaaS admin exports, and we report coverage as a percentage of known accounts rather than implying it is everything. Reporting what a system cannot see is more useful than a clean number.
Handling Movers, Which Are More Common Than Leavers
Internal moves are the largest source of access accumulation and the least automated transition. Supporting a mover-specific path: an agent that computes the difference between the old role and the new one, adds what is needed, and schedules removal of what is not, prevents the accumulation that makes long-serving staff the highest-privilege accounts in the business.
The counterargument is operational reality. A person moving teams usually needs to finish work in the old role, and stripping access on the transfer date breaks a handover that has weeks to run. Aggressive removal here generates real friction and a reputation for the system being obstructive. We schedule old-role access to expire thirty days after transfer, with one extension available on request, which handles the handover and still closes the gap. The point is that removal is scheduled by default rather than requiring somebody to remember.
Making Departure Trigger Itself
Trigger reliability decides whether the leaver path runs at all. In favour of integrating with the HR system as the source of truth: when a termination date is entered once, the agent can act on it without a separate notification, which removes the step most likely to be missed and the one most likely to be delayed in a contentious departure.
Against relying on it alone: HR systems are updated on payroll timelines, and a person walked out on Tuesday may not be recorded until Friday. For that scenario an emergency path is needed, one that a manager can trigger directly and that disables access immediately without waiting for records to catch up. We build both, and we test the emergency path on a schedule, because a path nobody has exercised is a path nobody should trust. The general caution about handing agents authority is in our piece on autonomous workflow agents.
Equipment and the Things That Have to Arrive Physically
Hardware logistics is the part of onboarding no agent can finish, and pretending otherwise produces the most visible failure a new starter experiences. In favour of automating the coordination: an agent can raise the order at offer acceptance rather than at start date, track the delivery, trigger device enrolment when the machine first checks in, and tell the manager three days out if nothing has shipped. That early warning is the whole value, because a laptop ordered late cannot be fixed on the morning it is needed.
Against expecting more: supply timelines are outside your control, and an agent that reports a confident ready status based on an order confirmation rather than a delivery will mislead everyone right up to the day. We tie the status to device check-in, an event that cannot be faked, rather than to any upstream promise. Anything before check-in is reported as pending, however encouraging the tracking page looks.
There is a quieter benefit worth naming. Ordering at offer acceptance rather than at start date typically buys two extra weeks, and in periods of constrained supply that margin is the difference between a starter who works on day one and one who borrows a spare machine for a fortnight and never quite gets set up properly.
How We Score AI Agents for Employee Onboarding
We score AI agents for employee onboarding on four questions. Does it treat joiner, mover and leaver as one record, so the same definitions drive all three. Does it record the justification and an expiry for every grant. Does it generate explicit owned tasks for systems it cannot reach, rather than omitting them. Can it produce a dated deprovisioning report an auditor would accept, and does that report state its own coverage.
New-hire experience features, the welcome sequences and the buddy assignments and the day-one checklists, are pleasant and are not what we buy on. They are also the part a small HR team can run well without software. The identity lifecycle is the part that degrades silently over years and that nobody notices until an access review or an incident. Getting it in place is ordinary enterprise AI integration and intelligent process automation work, described further under our AI agents services, and the deployment sequence is in our guide to integrating AI agents.
Frequently Asked Questions
Do we need role definitions before we start?
You need them for the handful of roles you hire into most often, not for the whole organisation. Start with five or six, build them from what the job requires rather than from what current staff happen to have, and extend as hiring patterns justify it.
What about systems with no API?
Have the agent raise an explicit task with a named owner and a due date. That keeps the manual work visible and inside the same record. The failure to avoid is a system quietly missing from the workflow, which produces a starter who looks provisioned and is not.
How quickly should access be removed on departure?
Immediately for a walked-out departure, via an emergency path a manager can trigger without waiting for HR records. For planned exits, on the recorded last working day. For internal moves, schedule old-role access to expire about thirty days after transfer.
Can an agent handle contractor accounts?
It handles them better than people do, provided every engagement carries an end date at creation. Contractor sprawl is almost entirely a missing-expiry problem, and requiring a date on the way in solves most of it without any ongoing effort.
Will this satisfy an access review or audit?
It helps substantially, because the dated record of what was granted and removed is the evidence reviewers ask for. It will only satisfy them if the report also states which accounts fall outside the agent’s coverage, since an unqualified claim of completeness invites the question you cannot answer.
Who Is Behind This Advice
Our team runs these lifecycles for clients, which means we are the ones reading the access review when it lands and explaining why a departed employee’s mailbox was still active. That experience is why this article spends more words on the leaver path than on the welcome sequence. The onboarding half is the visible half and the deprovisioning half is where the findings come from, every time.
We have also seen how quickly the copied-colleague habit reasserts itself. A firm can build proper role definitions, deploy them, and be back to mirroring an existing user inside a year, because mirroring is faster on a busy Monday. The automation only holds if the correct path is the easy path, which is a design constraint more than a technology one.
Matt Rosenthal leads Mindcore and pushes for controls that hold up over years rather than ones that look right at go-live, which in identity work means designing for the busy Monday rather than the demonstration.
Build the Leaver Path First
The takeaway is worth acting on before your next hire. Onboarding automation earns its cost through the identity lifecycle, so design the leaver path first and let provisioning follow from the same definitions. Build role definitions for your five or six most common roles from what the work requires, not from what existing staff have accumulated. Record a justification and, more importantly, an expiry on every grant, since expiry survives the shortcuts that justification does not. Make unreachable systems raise an owned task rather than disappearing from the workflow. Give movers a thirty-day expiry on old-role access so handovers work and gaps still close. Wire termination to the HR record and build a separate emergency path a manager can trigger, then test that path on a schedule. Report deprovisioning coverage as a share of known accounts and say plainly what sits outside it. Done in that order, the new-hire experience improves as a by-product and the access review stops producing surprises. If you want a look at what your current lifecycle would show under review, book a free strategy call and we will start with your last set of leavers. A related view on tooling and staff productivity is in our piece on using technology to boost employee efficiency.