Compliance reporting platforms are sold on framework coverage, the number of standards a product claims to map. That is the easiest thing to demo and close to the least useful thing to evaluate. What decides whether a client’s report survives contact with an assessor is evidence provenance: can each artifact be traced back to the system that produced it, on a stated date, with a collection method the assessor can verify without taking your word for it. A screenshot pasted into a template fails that test. An API pull with a timestamp and a source identifier passes it. This piece judges the 2026 tooling on provenance, on how control mapping behaves when a client carries three overlapping frameworks, and on whether tenant separation holds when one platform serves forty clients at once.
The Five Things This Guide Answers
Written for MSP and MSSP owners producing recurring compliance reporting for client portfolios, typically covering HIPAA, SOC 2, PCI DSS, or FTC Safeguards across a mixed base of 15 to 60 clients.
- Why evidence provenance beats framework coverage. The failure mode at audit is almost never a missing framework. It is an artifact nobody can source.
- How the platforms differ on control mapping. A client under two frameworks has overlapping controls, and tools handle that overlap in ways that produce very different report volumes.
- What multi tenant separation has to guarantee. Cross tenant leakage in a compliance report is a client-losing event, not a bug report.
- Where AI genuinely reduces effort. Evidence classification and narrative drafting, both real. Control interpretation, not yet.
- What to ask a vendor in the demo. Four questions that separate a reporting tool from a report generator.
Why Evidence Provenance Decides the Audit
Evidence provenance is the property that lets an assessor confirm an artifact came from the system it claims to, on the date it claims to, without trusting the party that assembled the report. It is the single attribute that most cleanly separates compliance tooling that holds up from tooling that looks finished.
What an Assessor Actually Challenges
In our experience sitting in on client assessments, the challenge is rarely “you have no control for this requirement.” It is “show me how you know this was true in March.” A report asserting that MFA was enforced across all administrative accounts is a claim. A report carrying the tenant identifier, the policy name, the query run, and the date it returned is evidence. The reasonable counterargument is that assessors vary widely, and plenty accept a well organised screenshot pack without challenge. That is true and it is also a poor thing to design around, because the assessor who does challenge it tends to be the one attached to a client’s largest contract renewal. Building for the strict case costs little once the collection is automated.
Where Screenshots Break Down at Portfolio Scale
For a single client, a screenshot workflow is merely tedious. Across forty clients on a quarterly cycle it becomes structurally unreliable, because the person capturing evidence in month eleven is not the person who captured it in month one, and neither documented which console view they used. Some MSPs argue that a strong internal checklist solves this without new tooling, and at firms with low technician turnover that argument holds better than it sounds. Set against it, checklists record what should have been captured rather than what was, and the gap between those two only becomes visible during an audit. Our team’s view is that the checklist and the automation solve different halves, and the automation is the half that survives staff changes. The wider relationship between service delivery and regulatory obligation is covered in our piece on managed IT services and meeting regulatory requirements.
The Date Problem Nobody Mentions in a Demo
Most frameworks assess a period rather than a moment, so a control that was enforced when you generated the report tells an assessor very little about the preceding quarter. Continuous collection with retained snapshots answers the period question, and point in time collection does not. Tools differ sharply here and demos obscure it, since a demo is by definition a point in time. The counterpoint worth holding is that retained snapshots carry storage and data handling obligations of their own, and evidence retention that itself breaches a client’s data policy is a genuine own goal. Scope the retention deliberately rather than accepting a default.
How the Platforms Compare on Control Mapping
The best AI tools for MSP compliance reporting for clients separate on how they handle a control that satisfies several frameworks at once, because that single behaviour determines whether your report reads as coherent or as three reports stapled together.
Platforms Built for the Service Provider Model
Centraleyes is positioned for MSSPs and virtual CISOs, with AI generating client-ready summaries, surfacing risks, and mapping requirements while automation drives assessments and reporting. The service provider orientation matters concretely: the data model assumes many client organisations rather than one, so tenant boundaries and per client reporting are native rather than retrofitted. Optro takes a comparable position for compliance, audit, and risk in one platform, using AI to classify evidence, map controls to frameworks, detect anomalies, and monitor controls continuously. Evidence classification is the capability doing real work in both, since sorting a quarter of collected artifacts against the right control is exactly the tedious, high volume, low judgment task these models handle well.
Security Platforms That Produce Compliance Output
A second group approaches from the security side. Guardz is built specifically for MSPs, combining endpoint protection, identity security, email security, cloud monitoring, awareness training, and threat detection, which means the compliance reporting it produces is a by product of controls it already operates. That has a real advantage: the evidence has clean provenance because the platform generated it rather than collected it from elsewhere. The limitation is coverage boundaries, since anything outside the platform’s own control surface has to be evidenced some other way, and a client’s physical safeguards or vendor management programme sit outside every tool in this category. Splunk Security Cloud organises security data into dashboards and simplifies regulatory reporting, which suits clients already generating the underlying telemetry and suits nobody else. Our overview of essential managed IT tooling sets out where these sit in a wider stack.
AI Governance Tools Are a Different Category
A third group gets recommended into this conversation and mostly should not be. WitnessAI, Credo AI, and Holistic AI address governance of AI systems: model risk, bias, fairness, and obligations under emerging AI regulation. Credo AI suits organisations building formal AI governance programmes with significant regulatory exposure, and Holistic AI suits bias, fairness, and EU AI Act requirements. These are real products solving a real problem, and that problem is not producing a client’s quarterly HIPAA evidence pack. The overlap is a naming collision. Where the distinction genuinely blurs is a client deploying AI inside a regulated workflow, in which case both categories apply and you need both. We have written separately about using AI on the audit and reporting workload itself, which is the adjacent question.
What Multi Tenant Separation Has to Guarantee
Multi tenant separation in compliance reporting has to guarantee that no artifact, control narrative, or risk finding from one client can surface in another client’s report, and this is worth testing rather than assuming.
The Failure Mode Is a Report, Not a Breach
Cross tenant leakage in this context rarely looks like a data breach. It looks like a paragraph of narrative in Client A’s report describing a remediation that happened at Client B, because the summarisation model was given a corpus spanning both. The client reading it learns two things immediately: their report contains someone else’s information, and their own information is presumably in someone else’s report. There is a fair objection that shared learning across a portfolio is genuinely valuable, and it is, at the level of aggregate benchmarks. The line we hold is that aggregate patterns may cross tenants and specific artifacts, narratives, and findings may not.
Testing It Before You Commit
The practical test is cheap. Load two sandbox tenants with deliberately distinctive evidence, generate a report for one, and search the output for the other’s markers. Vendors who have built this properly welcome the exercise. The counterargument from the vendor side, that a sandbox does not reflect production tenancy, is occasionally legitimate for platforms whose isolation is provisioned per contract rather than per workspace, so ask which model applies before treating a passed test as conclusive.
Access After Offboarding
The third separation question is what happens when a client leaves. Their evidence is theirs, retention obligations may outlive the relationship, and a platform with no clean export leaves you holding regulated data for a company you no longer serve. Confirm the export format and the deletion path before onboarding rather than during an exit, which is the same discipline we recommend around ending an underperforming provider relationship.
Where the Overlap Actually Bites
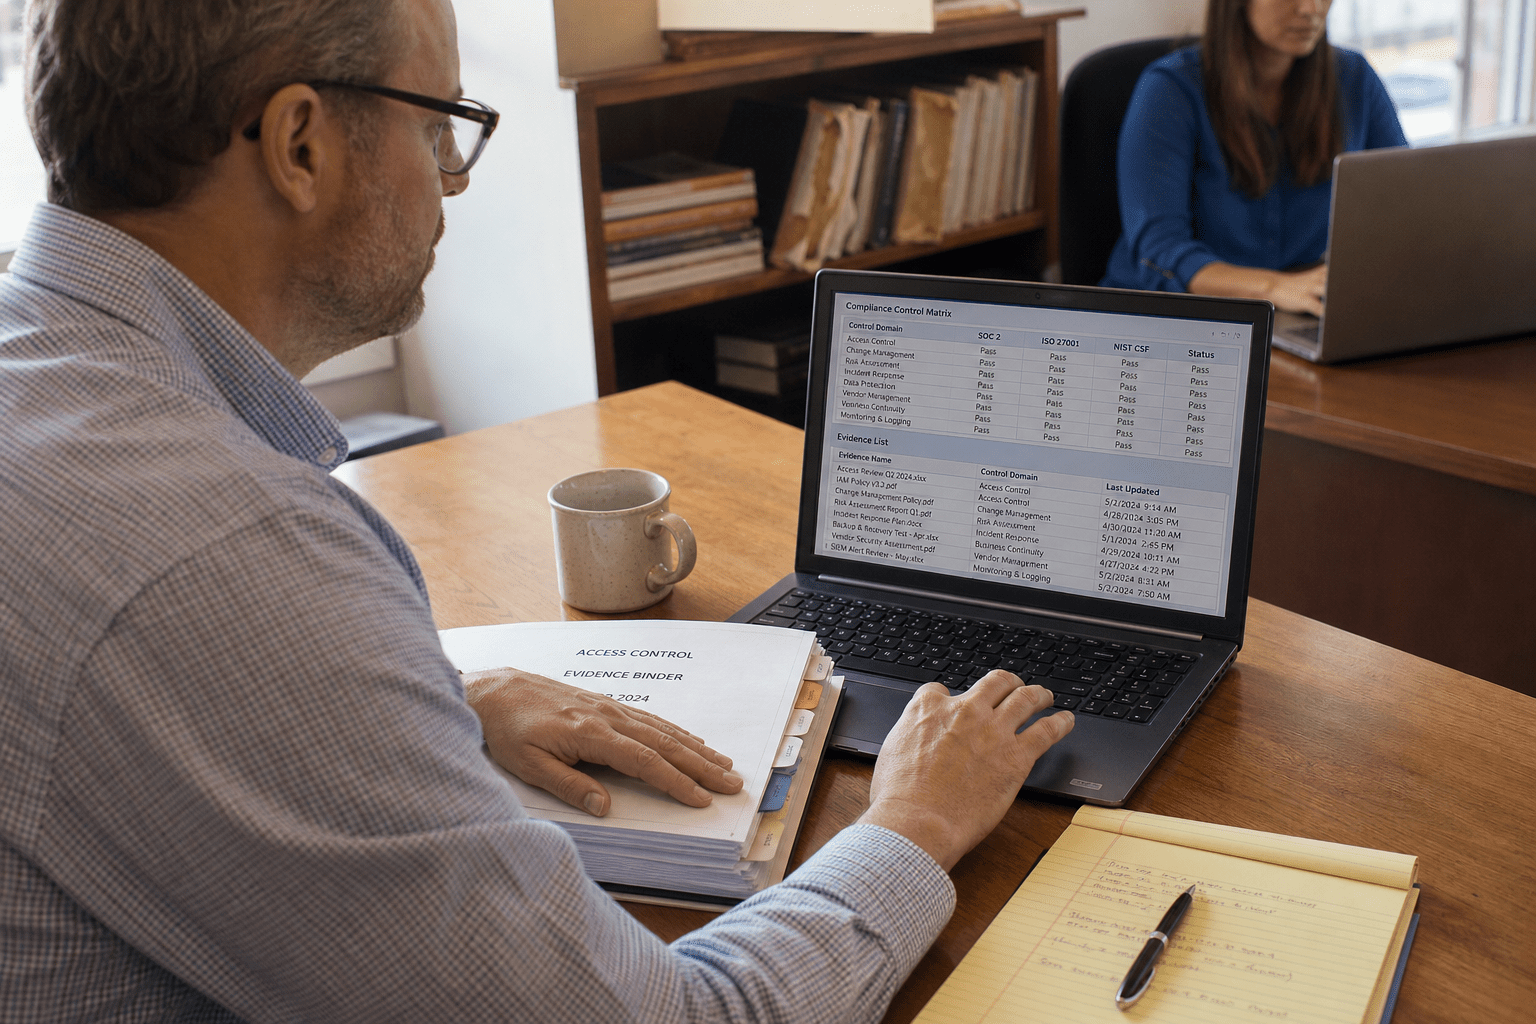
A client carrying both HIPAA and SOC 2 has controls that satisfy requirements in each, and access review is the clearest example. The underlying activity is one quarterly review of who holds elevated rights and why. Tools that model this as a single control with two framework references produce one evidence request, one artifact, and two citations. Tools that model frameworks as independent trees produce two evidence requests for the same review, and your technician either collects it twice or collects it once and pastes it into both, which reintroduces exactly the provenance problem automation was meant to remove. The objection to unified modelling is legitimate: frameworks genuinely differ in scope and evidence expectations, and collapsing two requirements onto one artifact can under-evidence the stricter of the pair. Encryption at rest is the usual example, where one framework accepts a policy attestation and the other expects configuration output. The defensible middle is to unify the control and keep the evidence requirement per framework, so the stricter expectation governs collection and the citation still resolves in both directions. Ask any vendor to show you this with a real overlapping pair rather than describing it.
Four Questions That Separate a Reporting Tool From a Report Generator
Every vendor demo shows a finished report. These four questions establish what produced it.
- Where did this artifact come from, and can the assessor see that? Ask for the provenance metadata on one specific line item, not the report as a whole.
- What happens when a client is under two frameworks with overlapping controls? You want one control evidenced once and referenced twice, not the same evidence duplicated into two reports with different wording.
- How do you collect for a period rather than a date? Continuous collection with retained snapshots is a different architecture from an on demand pull, and only one answers a period question.
- Show me tenant separation with my own test data. Any hesitation here is the answer.
A workable adoption sequence: run one client through the tool in parallel with your existing process for a full reporting cycle, compare the two outputs line by line, and count how many artifacts the tool produced that you would have had to chase by hand. That number is the honest measure of value, and it is available before you commit the portfolio. Firms building compliance into service delivery more broadly may find our cybersecurity compliance services and our note on compliance driven cybersecurity for New Jersey businesses useful reference points, and firms with FTC obligations should look at FTC compliance specifically.
Frequently Asked Questions
Can AI write the control narratives in a client compliance report?
It can draft them, and drafting is where the time goes, so that is worth having. What it should not do unreviewed is interpret whether a control satisfies a requirement, because that judgment is the thing an assessor is testing and a confident wrong answer is worse than a blank field. Our practice is AI drafts, a human confirms the interpretation, and the tool records who confirmed it.
Do these tools replace a compliance assessment?
No, and a vendor implying otherwise is describing a different product. These platforms assemble and organise evidence and produce reporting from it. An assessment is an independent opinion on whether that evidence satisfies the framework, and independence is the entire value of it.
How many clients before automation pays for itself?
The break even is driven by reporting frequency more than client count. A portfolio of ten clients on quarterly cycles generates more collection work than thirty clients reporting annually. Count reporting events per year rather than logos, and compare that against the hours your team currently spends chasing artifacts.
What about clients on frameworks the tool does not support?
Handle them outside the platform rather than forcing a mapping, because a poorly fitted framework template produces a report that reads as compliant while evidencing the wrong things. A partial deployment covering your common frameworks well is more useful than full coverage that misrepresents the edge cases.
Does automated evidence collection create new security exposure?
It does, and it should be treated as such. A collection tool holds standing read access into every client environment, which makes it a high value target and a concentration of risk. Scope its permissions to read only, review them on the same cycle as your privileged accounts, and make sure its own access is covered in the reporting it produces.
Who Is Behind This Guidance
Our team builds and runs compliance programmes for regulated clients rather than only advising on them, and that shapes the emphasis here. We have watched well organised reports get picked apart over a single unsourced artifact, and we have watched thin looking reports pass without a question because every line traced cleanly to a system. That contrast is why this guide weighs provenance above coverage, which is not how most product comparisons are written. Mindcore’s founder, Matt Rosenthal, keeps the firm focused on programmes a client can still stand behind two years in, once the initial project energy is gone and the quarterly cycle is just work. Compliance tooling earns its place on that timescale or not at all.
Talk Through Your Reporting Cycle
The parallel run described above costs you one client and one cycle, needs no vendor commitment, and will tell you more than any comparison table including this one. If you want a faster read, pull your most recent client report and pick three artifacts at random: if you cannot say which system produced each one and on what date, provenance is your gap and tool selection follows from that rather than from framework counts. Where our team helps is the part that is harder from inside a portfolio: deciding which frameworks justify automation, setting retention that does not itself create an obligation, and testing tenant separation properly before it matters. Book a free strategy call and we will walk one client’s reporting cycle with you and say plainly where the effort is going.