

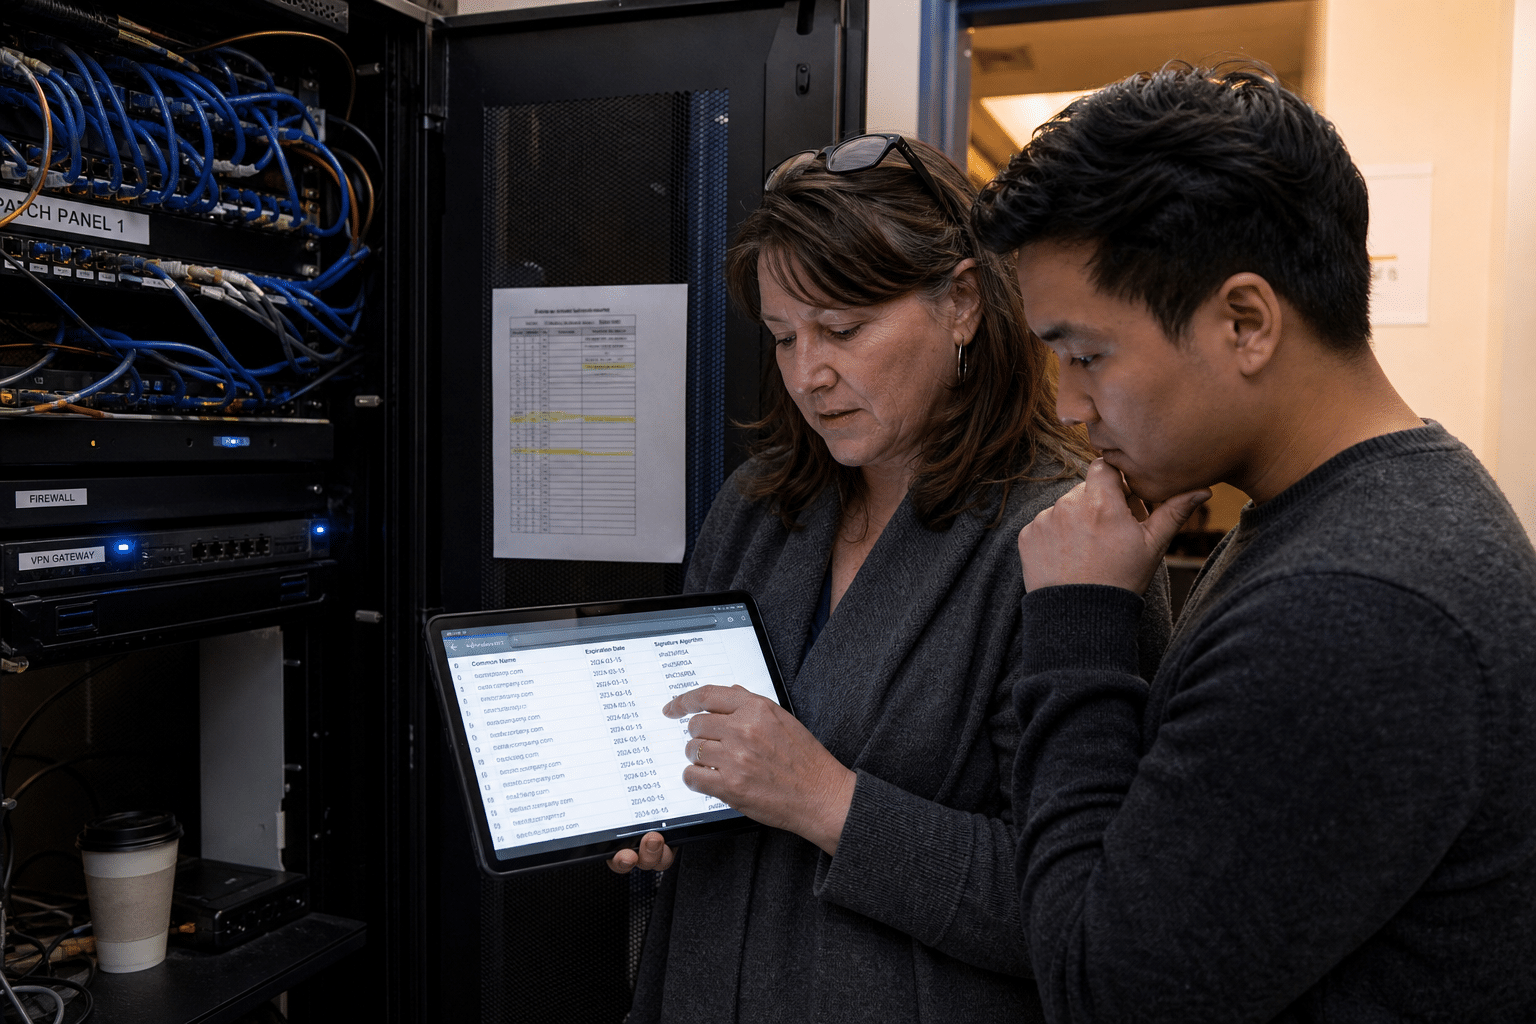
Post-quantum authentication means proving identity, for a website, a server, a device or a signed file, with digital signatures that a future quantum computer cannot forge. For a small or midsize business the work does not start with new algorithms. It starts with a list: every certificate you rely on, who issued it, when it expires, and which systems would break if its signature type changed. Microsoft made this point in October 2026 when it described its PQC TLS Pilot Program and urged organizations to start testing their certificate chains now, years before any deadline forces the change. Our team agrees with the timing and would put it more bluntly for SMBs: the algorithms will arrive through your vendors whether you plan or not, but the inventory, the testing and the contract language are yours to own. This article lays out six concrete steps and a realistic calendar for doing them.
The Five Points to Take Away
Before the detail, here is the short version our consultants give owners and IT managers who ask whether quantum risk is worth a meeting this year.
- Signatures are the slow part. Encryption can be upgraded quietly inside a protocol, but signatures live in certificates, firmware, code signing and smart cards that stay in service for years.
- You cannot replace what you have not found. Most SMBs we assess undercount their certificates by a wide margin, because appliances, printers, VPN concentrators and line-of-business apps each carry their own.
- Testing beats waiting. Larger post-quantum signatures change handshake sizes and break older parsers, and you only learn which of your systems choke by trying.
- Crypto-agility is a contract issue. The vendor who cannot tell you how they will swap signature algorithms is the vendor who will strand you.
- The calendar is real but not frantic. Federal guidance points to deprecating classical public-key algorithms around 2030 to 2035, so 2027 is the year to know your exposure, not the year to rip and replace.
Why Post-Quantum Authentication Is a Certificate Problem First
Post-quantum authentication becomes a certificate problem because nearly every trust decision your network makes rests on an X.509 certificate signed with RSA or elliptic curve cryptography, and those are exactly the signature schemes a large quantum computer would break. When NIST finalized ML-DSA (FIPS 204) and SLH-DSA (FIPS 205) in 2024, it gave the industry replacement signature algorithms. It did not give anyone a map of where the old ones live.
Where certificates hide in a typical SMB network
Certificates sit in far more places than the public website. In our assessments we routinely find them on the firewall management page, the VPN gateway, wireless controllers, the on-premises Exchange or file server that never quite got retired, multifunction printers, building access systems, backup appliances and internal web apps built by a contractor years ago. Each one was issued by someone, sometimes a public certificate authority, often a self-signed or internal one that nobody documented.
The opposing view is fair: many of those devices will be replaced on their normal refresh cycle before quantum attacks are practical, so cataloguing them can feel like busywork. Our answer is that the catalogue serves you now as well. Expired internal certificates cause outages today, and a device that cannot accept a modern certificate is already a security finding. The inventory pays for itself before the quantum question ever comes up.
Why signatures lag behind encryption
Encryption and signatures face different quantum threats on different clocks. Encrypted traffic recorded today could be decrypted later, the “harvest now, decrypt later” scenario, which is why browsers and cloud providers moved first on hybrid key exchange. Signatures are different: a forged signature only matters at the moment it is checked, so the urgency is lower but the migration is harder. Signature algorithms are baked into certificate chains, hardware security modules, smart cards and firmware update mechanisms, and changing them touches every party that has to validate them.
Some argue this means SMBs can ignore signatures until the big vendors finish. That is partly true, because your public website certificate will change when your certificate authority and browsers move together. It is not true for your private trust, the internal certificate authority, the device certificates and the signed scripts your team controls. Nobody upgrades those for you.
What the Microsoft pilot actually signals
Microsoft’s PQC TLS Pilot Program, described on its security blog on October 8, 2026, lets organizations test post-quantum certificates in TLS against real software before standards and public trust programs settle. The signal for an SMB is not that you should join a pilot. It is that the vendors who build your operating systems and browsers expect customers to find compatibility problems now, and they would rather you find them in a lab than in production.
Step 1: Build a Certificate Inventory You Can Trust
A certificate inventory is a living list of every certificate in your environment with its issuer, signature algorithm, key size, expiration date, owner and the system that depends on it. It is the first deliverable of the plan, and most of the effort in the whole program.
Start with what you can scan. Network discovery tools can sweep internal address ranges for TLS endpoints and record what each presents. Your Windows certificate authority, if you run one, holds a database of everything it issued. Your public certificate authority account lists your external certificates.
Then cover what scanners miss. Code-signing certificates live on build machines and in developer laptops. Client certificates used for Wi-Fi authentication or device enrollment live in your mobile device management platform. Hard-coded certificates and pinned public keys sit inside custom apps and integrations, and the only way to find those is to ask the people who wrote them.
We recommend a simple spreadsheet before buying any certificate lifecycle tool. Columns for location, issuer, algorithm, expiry, owner and business impact are enough.
Step 2: Rank What Breaks First
Ranking your certificates by exposure lets you spend effort where a failure would hurt most, rather than treating a printer and the VPN gateway as equal priorities. We score each entry on two questions: how long does the data or trust it protects need to stay safe, and how hard is the system to change?
Long-lived trust ranks highest. A root or intermediate certificate authority that will still be signing in 2033 deserves attention now. Firmware signing on devices you expect to run for ten years ranks next, because a device that cannot accept new signature types in a firmware update can never be fixed in place. Short-lived web certificates that renew every 90 days rank lowest, since they will rotate onto new algorithms naturally once your provider supports them.
The counterargument is that ranking requires judgment SMB teams may not have. That is fair, and it is where an outside view helps. Our team has seen owners rate their public website as most critical while an undocumented internal certificate authority quietly underpins every laptop login. A short ranking workshop with someone who has seen many networks usually corrects that.
Step 3: Test Post-Quantum Certificates in a Lab
Testing post-quantum certificates in a lab shows you which of your systems fail when signatures and handshakes grow larger, which is the most common real-world break. An ML-DSA signature is several kilobytes, compared with a few hundred bytes for an elliptic curve signature, and certificate chains grow to match.
Older load balancers, embedded web servers and middleboxes sometimes assume handshake messages fit within a fixed buffer. When the chain grows, they drop the connection or fail silently.
A practical lab for an SMB does not need special hardware. Several certificate authority vendors now offer private post-quantum test certificates at no extra cost to existing customers, explicitly marked as not production-ready. Open-source toolkits such as the Open Quantum Safe project’s libraries let an engineer generate test chains. Point a test certificate at a copy of your VPN, your internal web app and your reverse proxy, and record what fails.
Some teams worry that lab testing burns hours on standards that may still shift. Certificate profiles are indeed still settling. But the size problem will not go away, and knowing that your firewall model cannot handle large chains is useful whichever profile wins.
Step 4: Ask Your Vendors the Right Questions
Vendor questions turn crypto-agility, the ability to change cryptographic algorithms without redesigning a system, from a hope into a commitment you can hold someone to. For most SMBs, vendors control more of the cryptography than the internal team does.
These are the questions we put in front of every software and hardware vendor during renewals:
- Which signature algorithms does your product use for certificates, firmware and updates today?
- What is your published roadmap for supporting ML-DSA or other NIST-approved post-quantum signatures, and in which release?
- Can your product accept certificates from our internal certificate authority with a different signature algorithm without a code change?
- Will firmware already in the field accept updates signed with a new algorithm, or does hardware need replacing?
- Do you support hybrid certificates or dual signatures during the transition?
Write the answers into your inventory. Then add a crypto-agility clause to new contracts requiring support for NIST-approved post-quantum algorithms within a stated period after standards finalize for that product category.
Small customers have little leverage individually, but the question itself tells you which vendors have a plan, and that shapes your next purchase.
Step 5: Shorten Certificate Lifetimes and Automate Renewal
Shorter certificate lifetimes and automated renewal make the eventual algorithm switch a routine event instead of a project. Public TLS certificate lifetimes are already scheduled to shrink sharply over the next few years under CA/Browser Forum rules, so manual renewal is becoming unworkable regardless of quantum risk.
If your team renews certificates by hand from calendar reminders, the first post-quantum migration will be a scramble. If certificates renew automatically through ACME or your platform’s lifecycle tooling, changing the signature algorithm becomes a configuration change that rolls out on the next cycle.
Automation also strengthens identity controls you already depend on. Certificate-based device authentication pairs well with multi-factor authentication for every user, and both rely on trust that someone has to maintain. Our guide to MFA best practices covers the user side of the same problem, and our piece on why two-factor authentication became the norm explains how quickly expectations shift once the big platforms move.
Critics note that automation adds its own failure modes, a broken renewal job can take down a service. True, which is why automated renewal needs monitoring and an alert on failure. A monitored automated process still fails less often than a reminder in one person’s calendar.
Step 6: Set a Realistic Timeline Through 2030
A realistic post-quantum authentication timeline for an SMB spreads the work over roughly four years, matched to the federal and industry milestones that will force change on your vendors.
| Period | What to finish |
|---|---|
| Late 2026 to mid 2027 | Complete the certificate inventory, rank exposure, assign an owner for each certificate |
| Mid 2027 to 2028 | Lab-test post-quantum certificates on critical systems, collect vendor roadmaps, add crypto-agility clauses at renewal |
| 2028 to 2029 | Automate renewal everywhere possible, plan replacement of hardware that cannot accept new signatures, rebuild the internal certificate authority on a migratable design |
| 2030 onward | Move internal trust to post-quantum or hybrid signatures as vendors support them, retire classical-only systems |
This calendar tracks the direction set by NIST’s transition guidance and the US national security timeline, which both point to deprecating classical public-key algorithms in the early 2030s.
Some leaders will see four years and conclude there is no rush. The inventory alone often takes a quarter of focused effort in a busy SMB, and hardware refresh cycles run five to seven years. A device bought in 2027 without a crypto-agility answer may still be in your rack in 2033.
How This Connects to Your Existing Quantum Planning
Post-quantum authentication sits beside the encryption work many organizations have already started. If you operate in a regulated field, our articles on quantum-resistant encryption preparedness and quantum-ready IT infrastructure for protected data cover the data-at-rest side, while our analysis of encryption against AI and quantum threats and our quantum compliance guide cover how auditors are starting to ask about it. The certificate inventory described here feeds both programs, since the same list tells you where encryption and signatures each need to change.
Frequently Asked Questions
When will quantum computers be able to forge signatures?
Nobody can give a reliable date, and credible estimates range from the early 2030s to much later. The planning assumption used by NIST and US agencies is to finish moving away from classical public-key algorithms by around 2035, which is why inventory and testing belong in the next two years.
Do we need to replace our public website certificate now?
No, your public certificate will move to post-quantum signatures when your certificate authority and the major browsers support it together. What you should do now is confirm your renewal is automated, so the switch happens without manual work.
What is crypto-agility in plain terms?
Crypto-agility is the ability to change the cryptographic algorithm a system uses through configuration or an update, without redesigning or replacing the system. A crypto-agile product lets you adopt post-quantum signatures with a setting change instead of a hardware purchase.
Is an internal certificate authority a bigger risk than public certificates?
Often it is, because nobody upgrades an internal certificate authority for you and many SMB deployments were set up years ago without documentation. If your laptops, Wi-Fi or VPN trust an internal root, that root and its signature algorithm belong at the top of your exposure ranking.
How much does post-quantum readiness cost an SMB?
Most of the early cost is staff or consultant time for inventory and testing rather than new products. Test certificates are often free from existing providers, and the larger spending comes later as part of normal hardware and software refresh, which is why choosing crypto-agile products now keeps that cost down.
Who Is Behind This Guidance
Mindcore Technologies has spent years running certificate audits, rebuilding neglected internal certificate authorities and hardening identity systems for businesses with 10 to 500 employees across healthcare, finance, manufacturing and professional services. The steps above come from that fieldwork, from the devices that failed in testing and the vendor answers that turned out to matter at renewal time. Our role is to help your team see the whole map, so the decisions about pace and budget stay yours. Mindcore is led by CEO Matt Rosenthal, who focuses on making enterprise-grade security practical for growing businesses that do not have a dedicated cryptography team on staff.
Start Your Certificate Inventory This Quarter
The most useful thing an SMB can do about post-quantum authentication in 2027 is know exactly what it owns. Build the certificate inventory, rank it by how long each trust relationship must hold and how hard each system is to change, test the systems that matter most against larger post-quantum chains, and put crypto-agility questions in front of every vendor before you sign the next renewal. Automate certificate renewal so the eventual algorithm switch becomes a configuration change, and lay the work out on a calendar that tracks the early-2030s deprecation milestones rather than a panic date. None of this requires buying quantum products today, and almost all of it improves your security right now by removing expired, undocumented and weak certificates from your network. If you would like a second set of eyes on where your certificates live and which ones should worry you, our team can walk through it with you. Book a free strategy call and we will help you turn the inventory into a plan your team can run.

