

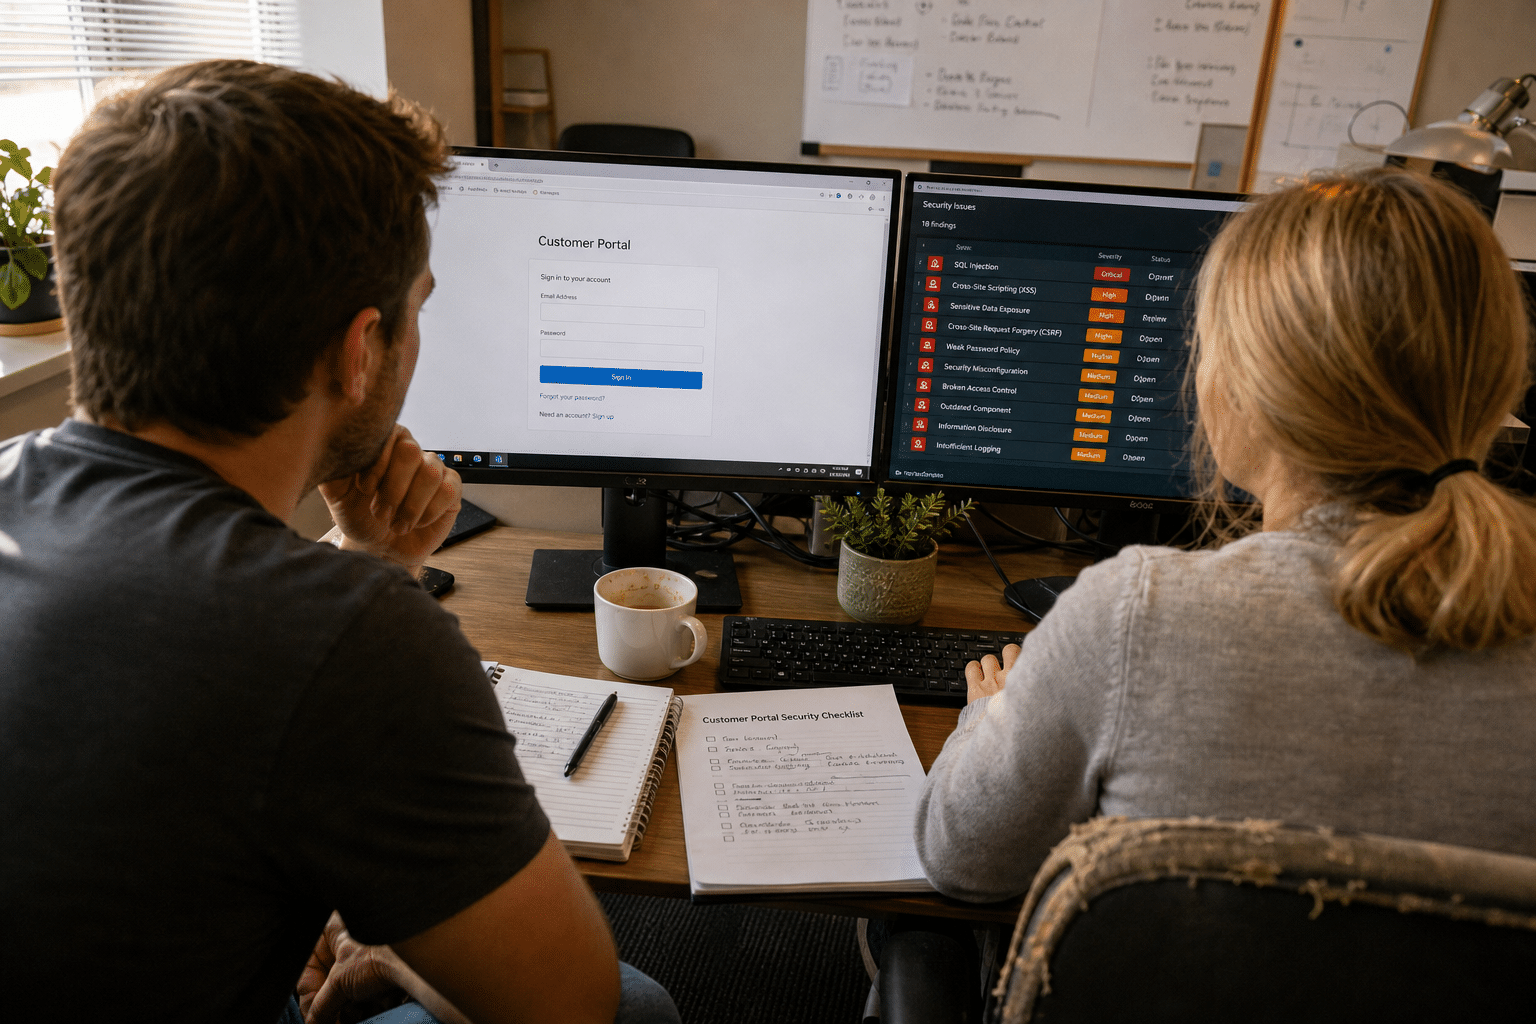
Web application security for SMBs now has to assume that someone is testing your customer portal every week, because AI has made finding flaws cheap. In October 2026, Dark Reading reported that Google’s internal PageBreak agent found roughly 500 flaws across Google’s own web applications by pairing AI discovery with deterministic checks that confirm a flaw is actually exploitable. Google runs one of the most mature security programs anywhere, and an agent still found hundreds of real issues. The same class of tooling is available to attackers, so the question for a 50 to 500 person company is no longer whether its portal has flaws. It is whether you learn about them before someone else does. This article covers the six portal weaknesses automated agents surface fastest, how to inventory what you run, and the questions to put to the developer or agency that built it.
The Five Points Every Portal Owner Should Hold Onto
Before the detail, here is the short version our team gives clients who run a client login, a payment page, an online booking tool or a vendor portal.
- Discovery is now cheap. An AI agent can crawl, probe and confirm a weakness in minutes, so attackers no longer save their effort for large targets.
- You cannot protect what you have not listed. Most SMBs we assess run two or three web apps nobody remembers approving, often a staging copy or an old form builder.
- Logic flaws beat scanners. The most damaging issues are permission mistakes, such as one customer seeing another customer’s invoice, and classic scanners rarely catch them.
- Your contract is a security control. The agency that built your portal decides how fast flaws get fixed, and that is set in writing, not in good intentions.
- Testing has to be continuous. An annual test describes one week of a portal that changes every month.
These points apply whether you sell to consumers, other businesses or patients. They matter most for firms handling payment data, health records or contract documents.
Why Web Application Security for SMBs Changed in 2026
Web application security for SMBs changed because the cost of finding a working exploit fell faster than the cost of fixing one. For years, small firms relied on a quiet assumption: a skilled tester costs money, so attackers aimed that skill at banks and retailers. Automated scanners existed, but they produced noisy lists that took a human hours to verify.
What the PageBreak report shows is the verification step getting automated too. The agent does not stop at “this parameter looks suspicious.” It confirms whether the issue is reachable and exploitable, which is the expensive part of a penetration test. Once that step is cheap, an attacker can point the same approach at thousands of small portals in parallel.
Are SMB portals really a target, or is this a big company problem?
Small portals are a target, and the argument against that view deserves a fair hearing. Large firms hold more data, and many attackers still go after scale. Our view is that both are true: high-profile campaigns chase big names, while automated campaigns chase whatever responds. A booking portal for a 40-person dental group answers a probe the same way a bank does. In the incidents our team has worked this year, the common thread was not the size of the victim. It was an exposed login page, an unpatched plugin, or an API that trusted whatever ID it was given.
Does AI help defenders as much as attackers?
AI helps defenders at least as much, but only if they actually run it. The same discovery techniques can sit inside your own testing program, and our AI-enhanced security services exist for that reason. The imbalance is about attention rather than tools. An attacker runs the agent on purpose. Many SMBs never run anything against their own portal after launch day.
The 6 Web Application Risks AI Agents Surface First
These are the weaknesses we see automated tools confirm fastest on SMB portals. Each one has a clear owner and a clear fix.
1. Broken access control on customer records
Broken access control means a logged-in user can reach data that belongs to someone else, usually by changing a number in a URL or an API request. If /invoice/1043 shows your invoice, an attacker tries /invoice/1044. It is the most common serious finding in web app testing, and it is exactly what an agent can enumerate tirelessly. The fix is a server-side ownership check on every record request, not a hidden button in the interface.
2. Forgotten staging and test copies
A staging site is a copy of your portal used for testing changes, and it is often left online with real data and weaker passwords. Agencies spin these up during a project and rarely take them down. An agent finds them through certificate logs and subdomain guessing within minutes.
3. Outdated plugins and frameworks
Portals built on WordPress, an off-the-shelf booking platform or an older framework inherit every flaw published against those components. Public vulnerability databases tell attackers exactly what to look for. The fix is a named person who applies updates on a schedule you can verify.
4. Weak authentication and session handling
This covers logins without multi-factor authentication, password reset flows that confirm whether an email exists, and sessions that never expire. Each lets an agent test stolen credentials at scale or take over accounts through the reset page.
5. APIs that trust the client
Many modern portals are a thin front end talking to an API, which is the behind-the-scenes interface the app uses to fetch and save data. When that API trusts whatever the browser sends, price fields, role flags and account IDs can all be altered. Agents read the app’s own JavaScript to map these endpoints.
6. File uploads and form inputs
Upload forms for documents, resumes or insurance cards are a common way in. Poor checks let an attacker upload a script instead of a PDF, or inject code into a form that later runs in a staff member’s browser.
How to Inventory Every Web App You Actually Run
An inventory of your web applications is a list of every site, portal, form and API your business exposes to the internet, with an owner, a purpose and a hosting location next to each. It sounds like paperwork. In practice it is the step that finds the most risk for the least money.
Start with what you know: the main website, the client portal, the payment page. Then widen the search. Ask finance which online tools they pay for. Pull your DNS records and list every subdomain. Search certificate transparency logs, which publicly record every HTTPS certificate issued for your domain. Ask each department head which forms collect customer information.
What belongs on the inventory sheet?
Each entry needs the URL, the business owner, the technical owner (internal staff or an outside firm), the platform it runs on, the type of data it holds, whether it requires a login, and the date it was last tested. Some teams also add whether the app is still needed. In almost every inventory we have run, at least one app could simply be switched off, which removes its risk entirely.
Should the inventory live with IT or with the business?
The honest answer is both, and there is a real tension. IT can maintain the technical detail, but only the business knows whether a portal still serves customers. When IT owns it alone, abandoned apps linger because nobody feels entitled to delete them. When the business owns it alone, technical details go stale. We suggest IT keeps the sheet and a business owner signs off on each line twice a year. A structured cyber security audit can produce the first version quickly.
How do cloud-hosted portals change the picture?
Cloud hosting moves some responsibility to the provider, but not the application itself. The provider secures the servers. Your configuration, your code and your access rules remain yours. Misconfigured storage buckets and over-permissive cloud roles show up in our findings regularly, which is why cloud security reviews belong alongside the app inventory.
What to Ask the Developer or Agency That Built Your Portal
The contract with whoever built your portal is one of your most important security controls, because it decides who fixes a flaw, how fast, and who pays. Most SMB portals were built by a small agency or a freelancer, and the original agreement covered delivery, not maintenance.
We recommend putting these questions to your developer in writing:
- Who applies security updates to the platform, plugins and libraries, and how often?
- How quickly will you fix a confirmed critical flaw? Ask for a number of days.
- Do you run automated security testing before each release? Can we see the results?
- Where are staging and test copies hosted, and do they contain real customer data?
- Who holds the admin credentials and hosting access, and is multi-factor authentication on all of them?
- If we end the relationship, how do we receive the code, credentials and documentation?
What if the developer is no longer around?
This happens more often than people admit: the freelancer moved on, or the agency closed. The portal keeps running with nobody watching it. Some owners decide the safest move is a rebuild, while others prefer to take over maintenance of the existing code. Both can be right. The deciding factors are how much sensitive data the portal holds and whether anyone can still read and update the code. Either way, the first step is recovering admin access and running a test against what is live today.
Is it fair to hold a small agency to enterprise standards?
There is a reasonable case that a five-person agency cannot match an enterprise security team. There is an equally reasonable case that your customers’ data deserves the same care regardless of who wrote the code. We land in the middle: you do not need an enterprise contract, but you do need written fix timelines and proof of testing. Our guide on how SMBs pick a managed IT security services provider covers the same vetting logic for outside partners.
How to Test Your Own Portal Before Attackers Do
Testing your own portal means running the same kind of discovery an attacker would, on a schedule, with someone accountable for the results. The goal is to see your findings list first.
A practical program has three layers. Automated scanning runs weekly or after every release and catches outdated components and common misconfigurations. Authenticated testing, done by a person or an AI agent logged in as a real customer, checks whether one account can reach another account’s data. A deeper penetration test, once or twice a year, looks at the business logic that tools still miss, such as discount abuse or approval steps that can be skipped.
How often is often enough?
There is no single right interval, and teams disagree. Quarterly testing is affordable and catches drift. Continuous testing tied to each release catches problems the day they appear. If your portal changes monthly and holds payment or health data, we lean toward release-based testing. If it is a static booking form that rarely changes, quarterly is reasonable. Pair either with network security monitoring so active probing gets noticed while it happens.
Who should read the results?
Findings that sit in an inbox do nothing. Every result needs an owner, a severity, and a fix date that someone checks. Firms without an in-house security lead often handle this through managed security services or a fractional security leader. We wrote about that model in our piece on how virtual IT security leadership helps SMBs compete like enterprises.
Where do compliance rules fit in?
If your portal touches patient data, HIPAA already expects periodic technical evaluation, and a portal flaw can become a reportable breach. Our article on HIPAA Security Rule compliance mistakes that cost SMBs covers the gaps we see most. Remote staff who log into admin panels from home networks add another layer, discussed in our look at hybrid work security cost risks.
Frequently Asked Questions
What is the biggest web application security risk for SMBs?
Broken access control is the most common serious risk we find, where one logged-in user can view or change another user’s records. It is easy for automated agents to test and often invisible in normal use. A server-side ownership check on every request closes it.
Can an AI agent really find flaws in a small business portal?
Yes, and quickly. The techniques reported in Google’s PageBreak work, automated discovery followed by confirmation that a flaw is exploitable, apply to any reachable web app. A small portal is often easier to test because it has fewer protective layers.
How much does web app testing cost an SMB?
Cost depends on the size of the app and how deep the testing goes. Automated scanning is inexpensive, while a manual penetration test of a complex portal costs more. Most firms start with an inventory and an automated baseline, then add deeper testing where the sensitive data lives.
Should we rebuild an old portal or secure the existing one?
It depends on whether anyone can still maintain the code and how sensitive the data is. If the platform is unsupported and the original developer is gone, a rebuild is often cheaper over three years. If the code is current and documented, hardening it is usually faster.
Who is responsible when a portal built by an agency gets breached?
Legally and reputationally, your business is responsible to your customers, even if the agency wrote the flawed code. That is why written fix timelines, access handover terms and testing evidence belong in the agency contract.
Who Is Behind This Advice
Mindcore Technologies has supported small and midsize businesses on managed IT and cybersecurity since the company was founded, and web application exposure has become one of the most frequent findings in the assessments our team runs. We help clients list what they run, test it the way an attacker would, and turn the results into a fix plan their developers can actually follow. Our CEO, Matt Rosenthal, focuses on making enterprise-grade security practical for firms without a large internal security staff, which is the gap automated attack tools now exploit most.
Get Your Portal Tested Before Someone Else Does
The lesson from 500 flaws in one of the best-defended companies anywhere is not that your portal is doomed. It is that discovery has become cheap, so someone is already looking, and the advantage goes to the owner who looks first. Build the inventory, put fix timelines into your developer contract, close broken access control and forgotten staging sites, and test on a schedule tied to how often the portal changes. If you want a second set of eyes on where your exposure sits today, book a free strategy call and our team will walk through your portals with you and outline what to fix first.

