A zero-click AI data leak requires nothing from your staff at all. In the EchoLeak research, an attacker sent a single crafted email, the recipient never opened it, and the assistant processed it during routine mailbox summarization. From there the technique caused Copilot to reach into files the user could access and send their contents outward. Microsoft scored it 9.3 and shipped a server-side fix in May 2026, with no confirmed exploitation in the wild. The reason it still matters is not the specific flaw, which is patched, but what it demonstrated: an AI assistant with broad access to your data will act on text that arrives from outside, and the blast radius is set by your own permissions rather than by anything the vendor controls.
The Five Things This Changes About Your Assistant
These are the points worth acting on regardless of which vendor’s assistant you run.
- User awareness training does nothing here. Nobody clicked. Nobody opened anything. The assistant read an email as part of its normal work.
- The assistant inherits the user’s reach. It can see what they can see, which means exfiltration stops exactly where their permissions stop.
- Untrusted text is an input, not a message. Any content the assistant processes from outside your organization is potentially instruction-shaped.
- Your oversharing sets the severity. Two firms on the same patched product carry completely different exposure depending on how their files are shared.
- The patch is the vendor’s job. The scope is yours. One of those is done and the other is not.
Our note on the hidden data exfiltration risks SMBs miss covers the wider pattern this sits inside.
Why a Zero-Click AI Data Leak Defeats Your Awareness Training
The entire security model most businesses rely on for email assumes a human in the loop deciding whether to trust something, and an assistant that reads the mailbox on the user’s behalf removes that human. Years of investment have gone into teaching people to hesitate over unexpected attachments and check sender addresses, and that investment remains worthwhile for conventional phishing. It contributes nothing to this. The assistant does not hesitate, does not check the sender, and was designed specifically to read everything and be helpful about it. Any control that depends on somebody deciding not to engage is bypassed by a system whose purpose is to engage automatically with all of it.
The Assistant Is a New Kind of Account
Treat an AI assistant as an identity with standing access rather than as a feature of your email client, because that is how it behaves and how it will be abused. It reads, it retrieves, and it acts, continuously, across everything the user can reach. When you ask what a compromise of that assistant would expose, the answer is the union of every file, mailbox, and site available to the person it works for. Most firms have never asked that question about any individual user, let alone as a class. Our note on insider threats hidden in access permissions covers the same arithmetic without the AI, and the numbers are usually uncomfortable before an assistant is involved at all. The counterargument that this proves assistants are unsafe is stronger than we would accept: the exposure was always there, and the assistant made it reachable by a new path rather than creating it.
Untrusted Content Is Now an Attack Surface
Any text your assistant processes from outside the organization should be treated as potentially instruction-shaped, which is a genuinely new category of input for most security teams. An email body, a document attached by a customer, a shared file from a partner, a web page the assistant fetches, and a calendar invite from a stranger are all content the system reads and may act on. Vendors are building classifiers to detect these attempts, and the EchoLeak research showed a determined technique chaining several bypasses to get past one. That arms race will continue and you are not a participant in it. What you control is how much the assistant can reach if an attempt succeeds, which is why scope work beats detection work for a business of ordinary size. Our piece on secure AI data access patterns covers the architectural side of keeping that boundary narrow.
Your Oversharing Decides the Severity
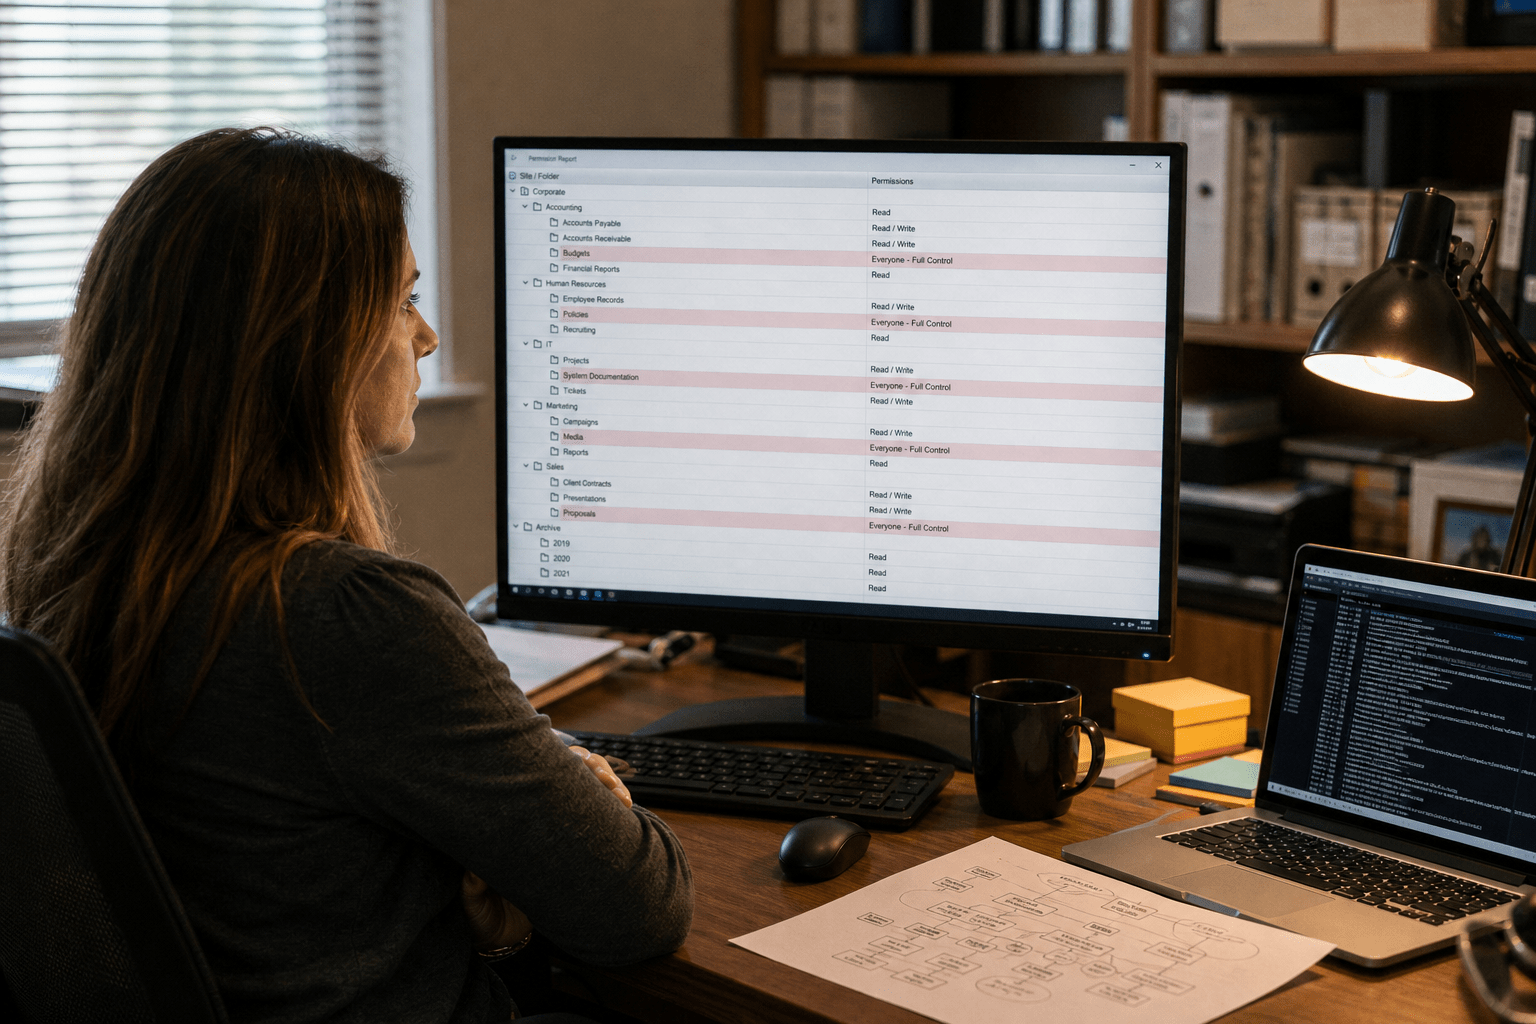
The same flaw in the same product produces a minor incident at one firm and a serious one at another, and the difference is entirely how their files were shared before anyone deployed an assistant. This is the most actionable finding, because it is work you can do today without waiting for a vendor. Most tenants we assess carry a long tail of sites shared with everyone in the organization, files shared by link to anyone with the link, and permissions inherited from a project that ended three years ago. None of that was a pressing problem while access required somebody to go looking. An assistant goes looking as its default behavior. Our guidance on secure document sharing in SharePoint and OneDrive is the practical starting point.
Run the Oversharing Report Before You Widen the Rollout
Find out what your most-connected user can actually reach before you extend an assistant to more people, because that number is your exposure and it is usually a surprise. Pick someone with long tenure and broad project history, run a report on everything they have access to, and read it. The common finding is access to sites they have not opened in years, retained because removal was nobody’s task. Fix that population before extending the assistant, not afterward. There is a reasonable objection that permission cleanup is a large, thankless project that stalls in every organization that starts it, and that gating an AI rollout behind it means never rolling out. That is a real risk. The proportionate version is to fix the worst tier only: anything shared organization-wide that contains payroll, contracts, customer data, or credentials. That is a bounded list and it removes most of the severity.
Decide What the Assistant May Never Touch
Some content should be outside the assistant’s reach entirely, and deciding that deliberately is easier than inspecting every access path individually. Board material, legal advice, personnel files, and anything under a contractual confidentiality obligation are the usual candidates. Putting those in locations excluded from assistant indexing gives you a boundary that holds regardless of what any future prompt injection technique achieves, because the content is simply not available to be retrieved. The argument against is that exclusions reduce the value of the tool and invite staff to work around them by copying material into places that are indexed, which genuinely happens. Keep the exclusion list short enough to be respected, and pair it with an explanation rather than a rule, since people route around controls they think are arbitrary. Our note on AI data privacy risks to fix before 2027 covers where regulators are heading on this.
What Monitoring Actually Helps
Conventional security tooling watches for a user behaving oddly, and in this attack the user did nothing at all, so the signal has to come from the assistant’s own activity rather than from the person. That is a gap in most deployments. Ask your vendor what audit data the assistant produces: which files it retrieved, on whose behalf, and where any outbound request went. Then ask whether anybody reads it. The honest answer in most businesses is that the logging exists and nobody has looked at it, which is understandable and worth changing at least to the extent of knowing what a normal week looks like. Our note on keeping cloud data secure covers the general posture this sits within.
Baseline Retrieval Volume, Not Individual Queries
Reading every assistant interaction is impossible and unnecessary, while knowing how many files it typically retrieves in a day is achievable and would have shown this attack. Exfiltration through an assistant looks like retrieval at a volume or breadth that does not match how the person works. Somebody in finance whose assistant suddenly reads across engineering sites, or a normal daily retrieval count that jumps by an order of magnitude, is the shape worth alerting on. Set the baseline from a quiet fortnight rather than from intuition. The counterargument is that legitimate work is bursty, a member of staff preparing for an audit will genuinely read across the whole estate, and a volume alert will fire on them first. That is true and it is survivable, because the number of such bursts in a month is small and each takes a minute to dismiss once you know who is doing what.
Know Your Response Before You Need It
If an assistant is implicated in a data exposure, the questions arrive faster than for a conventional breach, because the affected parties are named in the files it read. Work out in advance who can disable the assistant tenant-wide, how you would enumerate what it retrieved during a given window, and who makes the notification decision. That third one is a legal question in most jurisdictions and it is not a good moment to be finding your first answer. Our note on what to do after a data breach exposure covers the general process, and the AI-specific addition is the enumeration step, which depends entirely on logging you either turned on beforehand or did not. There is a fair argument that planning for a scenario with no confirmed real-world exploitation is premature. We would agree if the plan took a week. It takes an hour, and the same hour covers any future assistant incident regardless of technique.
Ask Your Vendor the Three Questions That Matter
Vendor security documentation is written to reassure rather than to answer, so go in with three specific questions and judge the responses on whether they are answerable rather than on whether they sound good. First, what boundary exists between content the assistant retrieves and instructions it will follow, and is that boundary a classifier or an architectural separation. A classifier is a probabilistic filter in an arms race; a separation is a property. Second, what retrieval audit data is available to us as the customer, at what granularity, and for how long is it retained. Third, what controls do we have to exclude specific locations from indexing, and are those enforced server-side or by configuration a user could undo.
You are not trying to catch anybody out. You are establishing which parts of your risk you control and which you are trusting somebody else with, and that distinction should be written down rather than assumed. A vendor who answers the third question clearly has given you something you can act on this month, regardless of how the first two land. The objection is that a small business has no leverage in this conversation and will get a link to a trust center rather than an engineer. That is usually true on the first attempt, and it is still worth the email, because the questions also work as an internal checklist. Anything the vendor will not answer becomes a scope decision you make yourself, which is the same conclusion the rest of this article reaches by a different route.
Frequently Asked Questions
Was EchoLeak exploited against real businesses?
There are no confirmed cases of exploitation in the wild, and Microsoft patched it server-side in May 2026. It matters as a demonstration of a technique rather than as an incident you need to investigate.
Does this mean we should not use AI assistants?
No. The exposure it revealed was mostly pre-existing oversharing that the assistant made reachable. Fixing the sharing is worthwhile whether or not you deploy an assistant.
Can security awareness training reduce this risk?
Not meaningfully for this attack class. Nobody clicked anything. Controls that depend on a person choosing not to engage are bypassed by a system built to engage automatically.
What is the single most useful thing to do?
Run an oversharing report on your most broadly permissioned user and fix anything shared organization-wide that holds payroll, contracts, customer data, or credentials. That bounded list removes most of the severity.
How would we know if it happened to us?
Through assistant activity logging rather than user behavior monitoring, since the user did nothing. Ask your vendor what retrieval audit data exists and establish what a normal week looks like.
Who You Are Taking This Advice From
Mindcore deploys and secures AI assistants inside Microsoft tenants for businesses that never ran a permissions cleanup because nothing forced one, which is where this risk actually lives. We run the oversharing report before the rollout rather than after, agree the short exclusion list with the people whose material is on it, and turn on the retrieval logging while somebody still has the admin console open, and the guidance above comes from tenants we have worked in rather than from the research paper. Matt Rosenthal, who leads Mindcore, keeps the firm focused on controls that survive the next technique rather than the last one, which here means narrowing what an assistant can reach instead of trying to out-detect an attacker. You decide what your assistant is for. Our job is to make sure it cannot reach what it was never meant to.
Your Next Move Before You Widen the Rollout
Pick your longest-tenured, most project-connected member of staff and find out what their account can actually reach. That single report is the honest measure of your exposure, and it takes an administrator an afternoon. Read it properly rather than skimming the total, because the interesting entries are the sites nobody has opened in years that were never removed. Fix the worst tier first: anything shared organization-wide holding payroll, contracts, customer records, or credentials. Then agree a short list of material the assistant may never index, and explain the reasoning to the people whose work is on it rather than announcing a rule. Turn on retrieval logging and spend ten minutes learning what a normal week looks like, so an abnormal one is visible. None of this waits on a vendor, and none of it is wasted if you never deploy another assistant, because every item on that list is a permission problem you had already. If you want somebody to run the oversharing report and set the boundary with you, book a free strategy call and we will start with your most connected account.