A VPN appliance compromise does not end when you install the update, because the attacker’s objective was never the flaw itself. Remote access appliances are exploited to harvest what is stored on and passing through them: local account credentials, cached directory passwords, active session tokens, and the configuration that tells an attacker exactly how your network is laid out. All of that is taken during the weeks before a patch exists. Then you patch, the vulnerability scanner turns green, and the attacker logs in through the front door with valid credentials against a fully updated device. We have worked incidents that began exactly this way, and in every one the patch had been applied promptly and correctly.
The Five Steps a Patch Does Not Cover
Applying the update is step one of six. These are the five that get skipped.
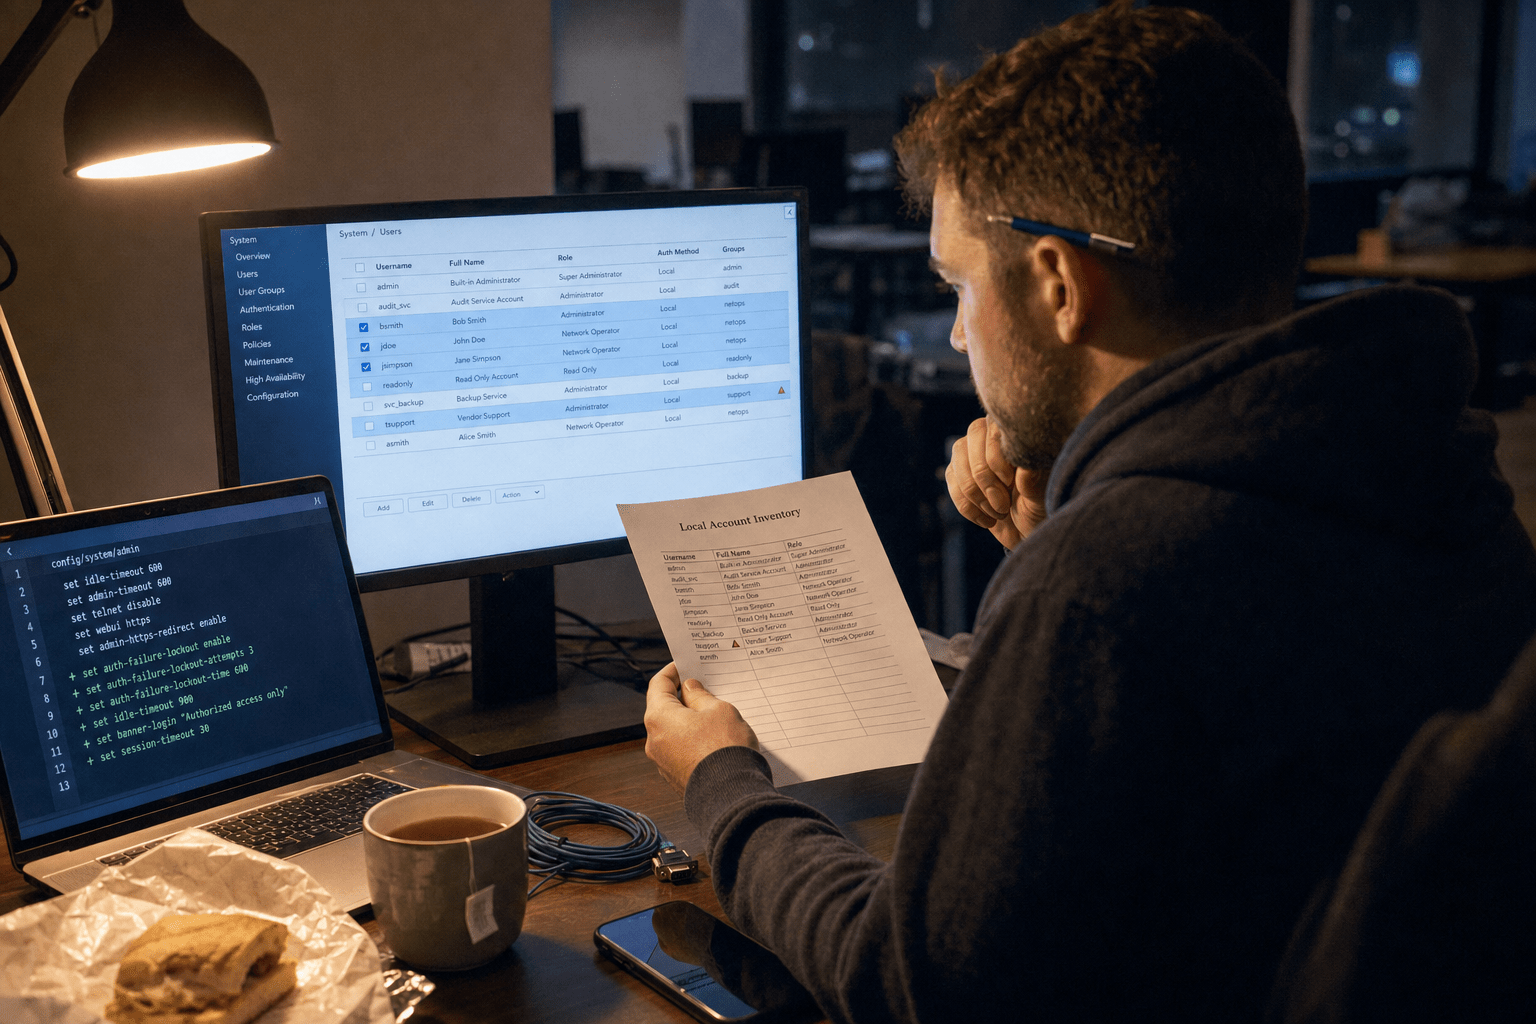
- Reset every local account on the appliance. Administrative and service accounts stored on the device should be treated as known to an attacker.
- Invalidate all active sessions. A live session token continues working after a patch unless somebody explicitly terminates it.
- Reset directory passwords for anyone who authenticated through it. Credentials passing through a compromised device were available to whoever controlled it.
- Review the configuration for additions. New local users, altered access rules, and changed logging settings are the persistence an attacker leaves behind.
- Check what the appliance could reach. The device sits inside your network, so its own access is a second path worth examining.
Our note on how identity-based attacks cost real money covers what happens after credentials leave.
Why a VPN Appliance Compromise Survives Patching
The patch removes the vulnerability and does nothing about the material taken through it, which is why a promptly patched device can still be the source of an incident weeks later. Think about the timeline these flaws follow. A vulnerability is discovered and exploited quietly, sometimes for weeks, by an attacker with no interest in being noticed. During that window they take what is useful, which on a remote access device is credentials and session state. The flaw becomes public, a fix ships, and defenders apply it in days if they are diligent. By then the credentials are already elsewhere. The remaining access requires no vulnerability at all, which is why it also evades a vulnerability scanner, and why the incident looks like a legitimate remote login when it eventually surfaces.
Credentials Are the Target, Not Access
An attacker with a foothold on a remote access appliance is collecting authentication material rather than looking around, because credentials are durable and a foothold is not. Local administrative accounts on the device, service accounts used for directory integration, and the credentials of every user who authenticates through it while the attacker is present are all available from that position. Some appliances cache directory credentials. Some log authentication attempts in ways that expose more than intended. All of them handle the material in memory. The practical consequence is that the blast radius of an appliance compromise is your user population rather than the device, and our work on monitoring network security treats a compromised edge device as an identity incident from the first hour rather than a device incident.
Sessions Outlive the Fix Unless You End Them
An active session established before patching continues to work afterward, because a session token is not re-validated against the vulnerability that allowed it. This is the step most commonly forgotten, and it is a single administrative action on most platforms. Terminate all sessions, force re-authentication, and accept the brief disruption of everybody reconnecting. Doing it during business hours is inconvenient and doing it not at all leaves a live path open. The objection is that forcing a reconnection for the whole remote workforce over an unconfirmed compromise is disproportionate, and for a vulnerability with no evidence of exploitation that argument holds. For anything confirmed as exploited in the wild before the patch, which describes most of the appliance flaws that reach the headlines, the assumption should run the other way.
The Configuration Is Where Persistence Hides
An attacker who expects to lose their exploit will leave something behind that survives it, and on an appliance that something is usually a configuration change rather than malware. A new local account with an unremarkable name. An additional authentication rule permitting a specific source. A modified logging configuration that quietly stops recording the thing they want unrecorded. None of that is detected by patching, none of it triggers an antivirus product, and all of it survives a reboot. Reviewing the configuration against a known-good copy is the only reliable way to find it, which is an argument for keeping a known-good copy.
Compare Against a Baseline, Not Against Memory
Reading a configuration and deciding whether it looks right is far less reliable than comparing it against an export from before the incident, especially on a device nobody reviews routinely. Export your appliance configuration on a schedule and store it somewhere separate. Then a post-incident review becomes a difference rather than an interpretation, and the difference takes ten minutes to read. Without a baseline you are asking somebody to notice an extra rule among dozens that all look plausible, which is an unfair test. The counterpoint is that configurations change legitimately and often, so a difference is not automatically a finding. True, and a difference you can explain is a much better position than a configuration you can only read.
Check the Accounts You Do Not Recognize
Any local account on the appliance that nobody can account for should be treated as an attacker’s rather than as an artifact of an old project, and the burden of proof sits on the account rather than on you. Appliances accumulate accounts: the one the installer created, the one for a monitoring integration nobody uses any more, the one somebody made for a contractor in 2022. That noise is exactly what a new account hides in. Work through the list with whoever administers the device and require an explanation for each, then remove what cannot be explained rather than leaving it pending. Our security audit work finds these on most engagements, and they are almost always benign, which is precisely the problem: a population of unexplained accounts is what makes one more invisible.
Tell People Why They Are Resetting
A forced password reset explained as routine maintenance trains staff to expect unexplained resets, which is the exact conditioning an attacker relies on when they phone somebody claiming to be IT. Say what happened in one or two plain sentences: a device that handles our remote connections had a security flaw, we have fixed it, and we are resetting passwords as a precaution because they may have been exposed. That sentence costs nothing and it buys two things. Staff comply faster when they understand the reason, and they become harder to social-engineer afterward because they now have a reference point for what a legitimate reset request looks like.
The instinct to say nothing is understandable, particularly while the investigation is open and nobody wants to commit to a characterization that might change. Our experience is that vagueness costs more than it saves here, because the reset is visible regardless and an unexplained one generates its own speculation, usually less accurate than the truth. Keep it short, avoid speculating about who or why, and say plainly that you will update people if the picture changes. That is a different act from a public disclosure, which has its own timing and its own advisers.
Reducing What the Next One Costs
Every appliance in this category will have another vulnerability, so the durable question is how much a compromise of it can reach rather than how quickly you patch. That reframing leads somewhere more useful than a faster patch cycle, because patch speed has a floor set by the attacker’s head start and no amount of diligence closes a window that opened before disclosure. What you can change is what the device holds and what it grants. Our comparison of VPN against zero trust approaches covers the architectural direction, and this is the operational version for firms staying put.
Stop the Appliance Holding Credentials It Does Not Need
Configuring remote access to delegate authentication rather than to store or cache it removes the most valuable thing an attacker finds on the device. Where the appliance can authenticate users against your identity provider without retaining credentials locally, configure it that way, and remove any local accounts beyond a single break-glass administrator with a long, stored, unused password. Multifactor authentication on the portal is table stakes and, importantly, it should be enforced at the identity provider rather than by the appliance, so a compromise of the appliance does not compromise the second factor. The objection is that delegating authentication introduces a dependency, and if your identity provider is unreachable nobody can connect. That is a genuine trade, and it is what the break-glass account exists for.
Put the Appliance’s Own Access on a Diet
The device sits inside your network with its own reach, and narrowing that reach is what limits an incident that starts there. Ask what the appliance can talk to, which for most installations turns out to be everything, because it was configured once to make connectivity work. Restrict it to the services remote users actually need, segment it away from administrative infrastructure, and make sure its management interface is reachable only from a small internal range. For firms handling regulated data the same reasoning applies with more force, as our note on secure remote access in healthcare covers, and the wider approach is the one set out in our five steps to zero trust for small business and in how ShieldHQ aligns those architectures.
Work Out Your Exposure Window Before You Scope the Reset
The reset list depends entirely on how long the device was exposed, and that date is knowable rather than a matter of guesswork. Take the earliest credible date of exploitation from the advisory, not the disclosure date, since those are usually weeks apart and the gap is exactly the period that matters. Then check when your device was reachable and running the affected version, which your change records or firmware history will tell you. The overlap is your exposure window. Everyone who authenticated through the appliance during that window goes on the reset list, and everything the appliance held throughout it should be treated as taken.
That calculation is what turns an unbounded, alarming task into a defined one. A firm with two hundred staff but only forty remote users has forty password resets rather than two hundred, and knowing which forty makes the difference between a job somebody schedules and a job everybody avoids. It also gives you the log range to examine, which otherwise becomes a search with no edges. The objection is that advisories are often vague about first exploitation and you may be working from an estimate. You usually are, and the right response is to take the earliest plausible date rather than the most convenient one, then note the assumption in your incident record so a later revision is a small adjustment instead of a fresh investigation.
Frequently Asked Questions
If we patched quickly, are we safe?
Not necessarily. These flaws are usually exploited before a fix exists, so credentials and sessions taken during that window keep working against a patched device. Patching is the first of several steps.
What should we reset after an appliance vulnerability?
Local accounts on the device, any service account it uses for directory integration, and the directory passwords of users who authenticated through it during the exposure window. Then terminate all active sessions.
How do we know if something was changed on the device?
Compare the configuration against an export taken before the incident. Without a baseline you are relying on somebody noticing an unfamiliar rule among many plausible ones, which is not a reliable check.
Does multifactor authentication protect the appliance?
It helps substantially, provided it is enforced at your identity provider rather than by the appliance itself. A second factor validated by the compromised device offers much less.
Should we replace VPN with something else?
That is a separate architectural decision worth making on its own timeline. The steps here apply either way, because you will be running the appliance during whatever transition you choose.
Who You Are Taking This Advice From
Mindcore works remote access incidents for businesses where the appliance was installed years ago by somebody who has since left, which means our first job is usually finding out what it can reach. We run the eviction steps in order, compare the configuration against a baseline where one exists and create one where it does not, and treat a compromised edge device as an identity incident rather than a hardware one, and the guidance above comes from incidents we have handled rather than from an advisory. Matt Rosenthal, who leads Mindcore, keeps the firm focused on limiting what a failure reaches rather than on preventing every failure, which at the network edge means an appliance that holds nothing worth stealing. You decide how people connect. Our job is to make sure one bad month does not become your whole user directory.
Your Next Move on Remote Access
Assume the next advisory is already written and prepare for it now. Export your appliance configuration this week and store the copy somewhere the appliance cannot reach, because that single file turns a future investigation from interpretation into comparison. Work through the local account list with whoever administers the device and remove anything nobody can explain, leaving one break-glass administrator. Confirm your multifactor enforcement sits at your identity provider rather than on the appliance. Then find out what the device can actually talk to inside your network, which in most installations is considerably more than anyone intended, and narrow it to what remote users genuinely need. When the advisory does arrive, patch first and then run the other five steps rather than stopping at the scanner turning green. The firms that get hurt by these flaws are rarely the ones that patched slowly. They are the ones that patched and stopped. If you want help building the baseline and narrowing the appliance’s reach, book a free strategy call and we will start with its configuration.