

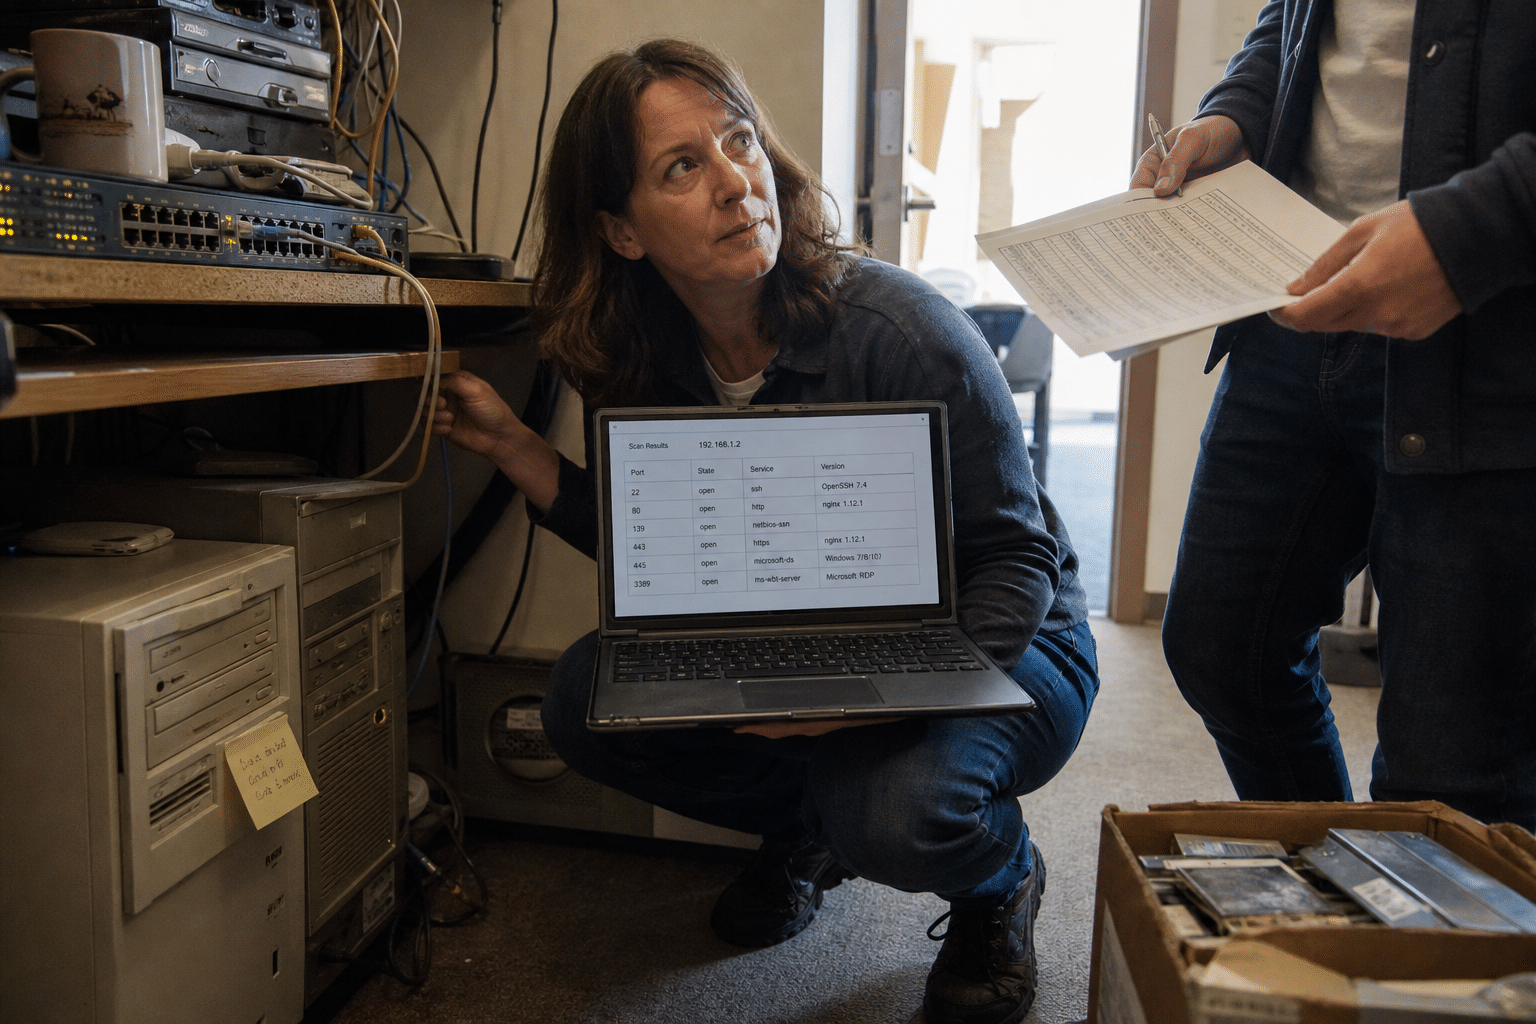
Old vulnerabilities are still exploited because the servers carrying them are still online, still reachable from the internet, and still owned by nobody. In October 2026 the Cybersecurity and Infrastructure Security Agency (CISA) added five flaws to its Known Exploited Vulnerabilities catalog after a China-linked group tracked as Flax Typhoon used them to break into organizations. Two of those flaws date to 2015 and one to 2016. Federal agencies were told to patch or stop using the affected products by October 11. Private businesses got no deadline at all, which is exactly why the same flaws will keep working against them. If you cannot name an owner for every internet-facing service you run, you are carrying this risk today.
The Five Points This Article Makes
Here is the short version for an IT manager or owner who needs the answer before the detail.
- Age is not protection. A flaw from 2015 with a public exploit is more dangerous to a small business than a brand new flaw with none, because attackers automate what already works.
- The exposure lives in forgotten services. FTP servers, Java web apps, document editors and headless content systems get stood up for one project and never retired.
- State groups use the same doors as criminals. Flax Typhoon did not need anything exotic. It used catalogued, patchable flaws, then password spraying and VPN persistence.
- Inventory comes before patching. You cannot patch what you do not know you run. An owner-per-service list is the first control, not the last.
- Retire beats patch for dead apps. When a service has no business owner, turning it off removes the risk permanently. Patching it only buys time.
Why Old Vulnerabilities Still Exploited Today Hit SMBs Hardest
Old vulnerabilities still exploited in 2026 hit small and midsize businesses hardest because those businesses rarely have a person whose job is to find every exposed service. Large enterprises run attack surface management programs. A 60-person accounting firm usually has one IT generalist or an outside provider focused on laptops and Microsoft 365.
Our team sees the result on almost every new client assessment. We find an FTP box set up in 2017 to swap files with a printer vendor. We find a Tomcat server still running a Struts app from a website rebuild that was abandoned. We find a test instance of a document editor somebody spun up to try an alternative to SharePoint. None of these show up on the asset list because none of them were ever on it.
Attackers do not need to know your company exists. Internet-wide scanners check every reachable address for known banners and version strings, then hand the matches to exploit scripts. Industry telemetry has shown for years that the most common network attacks against small businesses use flaws that are several years old, some close to a decade.
Does a Ten-Year-Old CVE Really Matter?
Yes, a ten-year-old CVE matters as much as a new one if the vulnerable software is still reachable, because the exploit has had a decade to become reliable and automated. The ProFTPD flaw in this month’s catalog carries a CVSS score of 10.0, the highest possible rating.
The opposing view has some merit. Many old flaws only affect configurations that modern installs no longer ship, and a patched or rebuilt server is not at risk at all. If your FTP server runs a current release, the 2015 issue does not apply.
Both statements are true, and that is the point. The age of the flaw tells you nothing. The age and ownership of the server tells you everything. We recommend you stop sorting vulnerabilities by publication date and start sorting them by whether a public exploit exists and whether the service faces the internet.
Why Do Patch Cycles Miss These Servers?
Patch cycles miss these servers because monthly patching tools cover the operating systems and applications they were told about, and forgotten services were never enrolled. Windows Update and a remote monitoring agent will not touch a Linux FTP daemon on a box nobody registered.
A fair counterpoint is that good patch tooling does discover unmanaged hosts on the internal network. That is true for machines on the domain. It is much less true for a cloud VM in a personal subscription, a rented VPS or a device with its own public address. Our vulnerability assessment service exists largely to close that gap from the outside in.
What Does This Have to Do With Nation-State Attackers?
Nation-state attackers matter to small businesses because they scan the same internet everyone else does and use small networks as stepping stones. CISA leadership said publicly that China-affiliated actors are positioning inside critical infrastructure, including operational technology, to cause disruption at a time of their choosing.
Some owners reasonably argue that a dental practice or a regional distributor is not a strategic target. Often it is not the final target. It is infrastructure: a server to proxy through, a mailbox to phish partners from, or a supplier with access to a larger customer. Being boring does not take you off the scan list.
The 5 Apps SMBs Forget to Patch, From This Month’s Catalog
The five apps in this month’s Flax Typhoon catalog entries map neatly onto the services small businesses forget. Each one below names the flaw, the year it was disclosed, and the plain question you should ask about your own environment.
ProFTPD File Transfer Servers (CVE-2015-3306)
ProFTPD servers vulnerable to CVE-2015-3306 let a remote attacker copy files around the server without logging in, using the mod_copy commands, which can lead straight to code execution. It is rated 10.0.
FTP survives in small businesses because a vendor, a scanner workflow or a legacy line-of-business app still expects it. Some of those are genuine dependencies, and ripping them out without a replacement breaks a real process.
Ask your team one question: is any FTP service reachable from the internet, and who asked for it? If the answer is a vendor that left three years ago, turn it off. If it is a live workflow, move it to SFTP on a current release and restrict it to the partner’s IP addresses.
Apache Struts Java Web Apps (CVE-2016-3081)
Apache Struts apps vulnerable to CVE-2016-3081 allow remote command execution when Dynamic Method Invocation is enabled. Struts sits inside many custom Java portals built in the early 2010s, often by a contractor who is long gone.
The other side is that plenty of Struts apps were rebuilt or patched years ago, and Dynamic Method Invocation is off in most hardened builds. You may be fine. The trouble is that nobody can say so without checking.
If you have a customer portal, quoting tool or intranet app written in Java, ask who maintains it and what framework version it runs. A portal with no maintainer should sit behind a VPN or zero-trust gateway at minimum, and preferably be retired.
ONLYOFFICE Document Servers (CVE-2021-3199)
ONLYOFFICE Docs servers vulnerable to CVE-2021-3199 suffer a path traversal flaw when JSON Web Tokens are used, which can allow remote code execution through an image upload parameter. Self-hosted office suites get deployed as a cost saving or a privacy experiment.
There is a reasonable case for self-hosting documents, especially for firms with data-residency concerns. That case only holds if someone patches the server on the same cadence as the vendor releases.
Check whether anyone in your company stood up a self-hosted document editor, wiki or file-sharing tool.
Strapi Headless CMS Instances (CVE-2023-22894)
Strapi installs vulnerable to CVE-2023-22894 store sensitive user details in a way an attacker with admin panel access can pull out through query filters. It is the youngest flaw on this list and needs a foothold first, so it rated 7.2.
That foothold requirement is a fair reason to rank it lower than the FTP flaw. It is also exactly the kind of chain Flax Typhoon favors: password spray the admin panel, then use the flaw to harvest more credentials.
If a marketing agency built your site on a headless CMS, find out whether the admin panel is exposed to the internet and whether it enforces multi-factor authentication.
ISC BIND DNS Servers (CVE-2015-5477)
ISC BIND servers vulnerable to CVE-2015-5477 can be crashed remotely with a crafted TKEY query, taking down name resolution for everything that depends on them. It is a denial-of-service flaw rather than a break-in, rated 7.5.
Most small businesses now use their registrar or cloud provider for public DNS, so many readers will not run BIND at all. Those who do usually inherited it with an old Linux server or firewall appliance. Our guide to common network security vulnerabilities and how to fix them covers the wider set of network-layer weaknesses that travel with these boxes.
How Flax Typhoon Turned Old Flaws Into Persistent Access
Flax Typhoon turned these old flaws into persistent access by combining them with ordinary techniques: scanning, cross-site scripting, password spraying against Microsoft Exchange, persistence through VPN software, and scripts that pulled out email and credentials. Nothing in that chain is new.
Why Persistence Matters More Than the Initial Flaw
Persistence matters more than the initial flaw because patching the entry point does not remove an attacker who has already installed a VPN client or created accounts. A server patched in November can still have a backdoor from September.
Some teams treat a patch as the end of the incident, and for a flaw nobody exploited that is reasonable. For a flaw on the known-exploited list that sat exposed for months, assume compromise until a review says otherwise. Look for new local accounts, unfamiliar remote access tools and outbound connections to unknown hosts. Our network security monitoring watches for exactly that outbound pattern.
Why Password Spraying Still Works on Exchange
Password spraying still works on Exchange because on-premises servers often accept legacy authentication that skips multi-factor prompts. The attacker tries a few common passwords across every mailbox and waits for one to land.
The counterargument is that most SMBs moved to Exchange Online years ago. Many did, but hybrid setups kept an on-premises server for management or relay, and that server is frequently left exposed. The CIS Controls v8 gaps small firms still miss include exactly this kind of unmanaged legacy authentication.
What Remote Access Persistence Looks Like
Remote access persistence looks like a legitimate VPN or remote support client installed on a server that never needed one, configured to reach out to a host the attacker controls. Because the software is legitimate, antivirus rarely flags it.
Admittedly, legitimate tools are installed for good reasons every day, and alerting on all of them creates noise. The workable middle ground is an allow list of approved remote access tools, with anything else raising an alert. We cover the VPN side of this in our piece on eliminating VPN vulnerabilities in healthcare organizations, and the lessons carry to every sector.
What to Check, Change and Ask Your Provider This Quarter
The practical response to old vulnerabilities still exploited is a short, repeatable program: find every internet-facing service, assign it an owner, then patch it, restrict it or retire it. Here is the sequence our team runs with new clients.
Build an Owner-Per-Service Inventory
An owner-per-service inventory lists every public IP address, subdomain and cloud service your company runs, with a named person who can say why it exists. Without the owner column the list goes stale within a quarter.
- Pull every DNS record for your domains and resolve each one.
- Export public IPs from your firewall, ISP account and every cloud subscription, including personal ones staff used for work.
- Run an external port scan against that list and record the software and version on each open port.
- Match each service to a business owner. Anything with no owner after two weeks goes on the retire list.
Decide Patch, Restrict or Retire
Every service on the list gets one of three decisions, and the decision is recorded so it does not get relitigated each quarter.
- Patch when the service is needed, publicly reachable by design and supported by its vendor.
- Restrict when the service is needed but only by known parties. Put it behind a VPN, a zero-trust gateway or an IP allow list.
- Retire when the service has no owner, no vendor support or no current purpose. This is the only option that permanently removes the risk.
Questions to Ask Your IT Provider
If an outside provider manages your environment, these questions tell you quickly whether forgotten services are covered.
- Do you scan our public IP ranges and domains from the outside, and how often?
- Do you subscribe to the CISA Known Exploited Vulnerabilities catalog and compare it against our inventory?
- Who gets alerted when a new internet-facing service appears?
- What is your process for a server nobody claims?
If the answers are vague, our managed security services team can run this program alongside your current provider, or our cyber security audits can give you a one-time baseline.
Frequently Asked Questions
Why are old vulnerabilities still exploited if patches exist?
Old vulnerabilities are still exploited because many vulnerable servers were never patched, usually because nobody knows they exist. Public exploits for these flaws are free and automated, so attackers keep scanning for the laggards.
Is the CISA KEV catalog relevant to private businesses?
Yes, the CISA Known Exploited Vulnerabilities catalog is the most useful free prioritization list a private business can use. The deadlines apply only to federal agencies, but every entry is a flaw attackers are actively using right now.
How often should a small business scan its internet-facing services?
A small business should scan its internet-facing services at least monthly and after any change to DNS, firewall rules or cloud subscriptions. Continuous external monitoring is better for firms that handle regulated data.
Should we patch or retire an old application nobody uses?
Retire it. An application with no owner will not be patched consistently, and turning it off removes the risk permanently. Keep a backup of its data in case someone later finds a need for it.
Who Is Behind This Advice
Mindcore Technologies has spent years helping small and midsize businesses in New Jersey, Florida and beyond find the services they forgot they had, then decide what to keep. The work in this article comes from those assessments: the FTP boxes, abandoned portals and test servers we turn up on real client networks, and the cleanup that follows. We approach it as your guide. You know your business and which services matter; we bring the scanning, the threat intelligence and the experience of having done this many times. Matt Rosenthal, Mindcore’s CEO, focuses on making enterprise-grade security practices workable for companies without an enterprise security budget, and this inventory-first approach reflects that priority.
Close the Doors Attackers Already Know About
Closing old vulnerabilities still exploited by attackers starts with knowing every door your business has left open to the internet, and it rarely needs new technology. The Flax Typhoon entries this month are a clean example: a decade-old FTP flaw, an old Java framework, a self-hosted document editor, a content system admin panel and a legacy DNS server. Federal agencies had a deadline to act. Your business does not, which means nothing forces the work except a decision to do it. Build the owner-per-service inventory, sort every service into patch, restrict or retire, and make your provider show you the external scan. The cybersecurity mistakes CEOs still make almost always include assuming somebody else owns this list. If you want a second set of eyes on what your business exposes today, book a free strategy call and our team will walk through your external footprint with you.

