

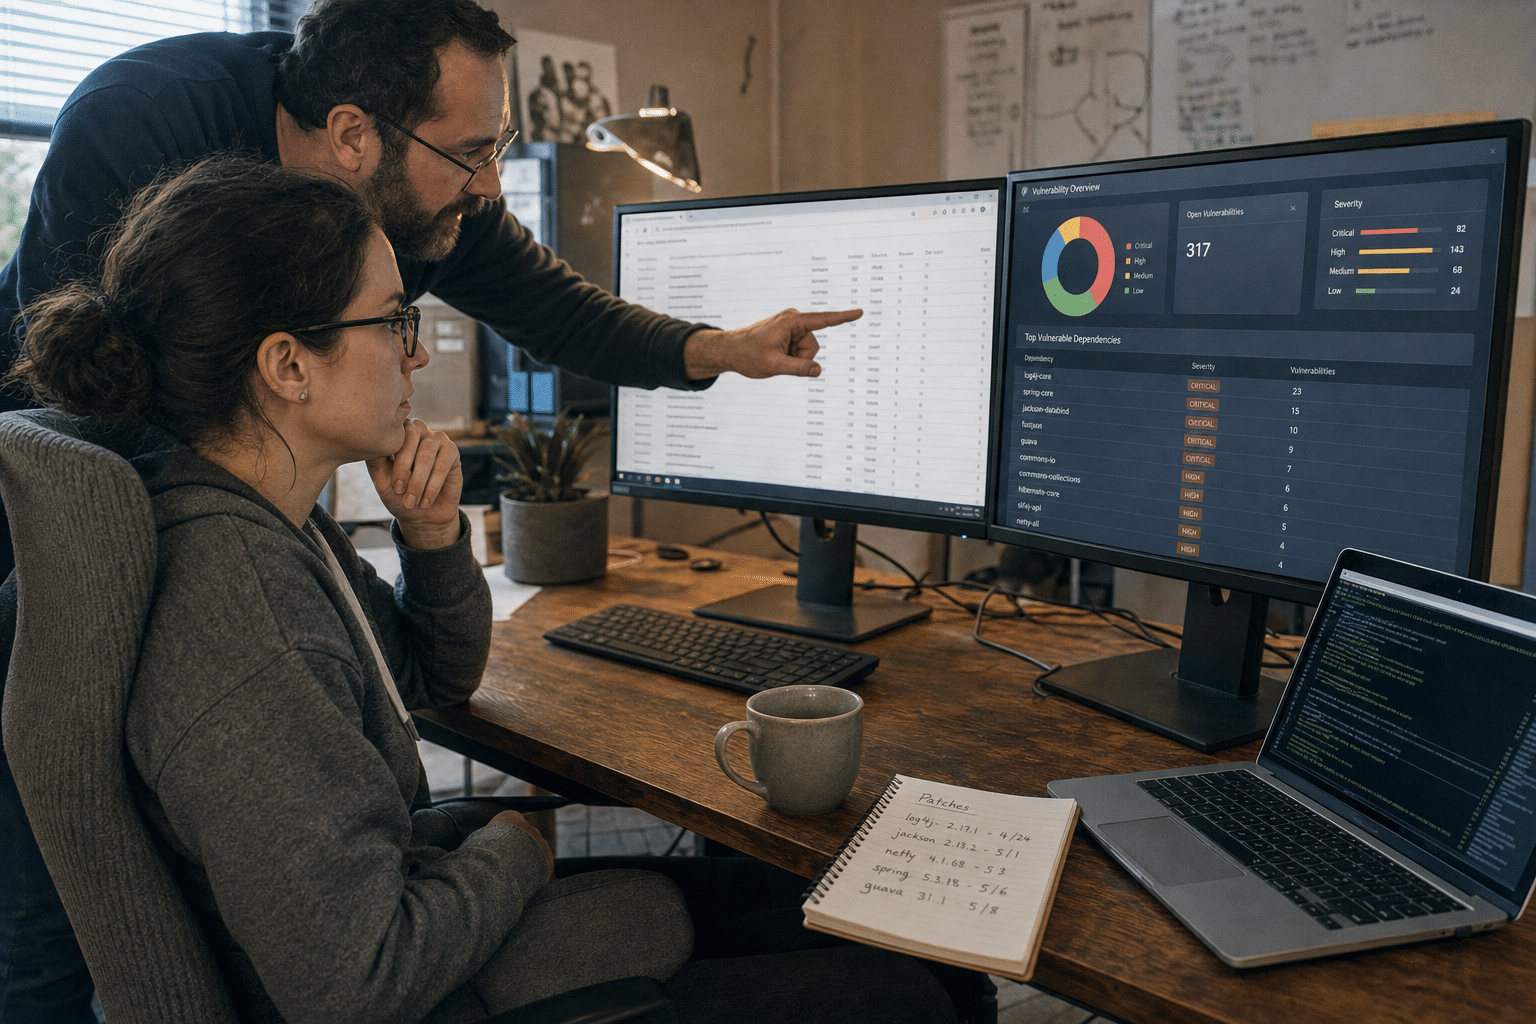
AI vulnerability scanning of open source software means large language models read the source code of public projects, reason about how data flows through it, and report flaws that older pattern-matching tools missed. For a small or midsize business, the important part is what happens next: every confirmed flaw becomes a patch, and those patches land inside the accounting platform, the firewall appliance, the line-of-business app and the website plugins you already run. You probably did not write any of that code, and your vendors may not tell you it was affected. When Anthropic announced its free, opt-in OSS Scanner in October 2026, as reported by The Hacker News, it signaled that machine-speed bug hunting is now available to every maintainer at no cost. That is good news for software quality. It also means a heavier, faster stream of fixes your business has to absorb, and the firms that prepare now will patch calmly while others scramble.
The Five Points to Take Away
- More flaws are about to be found. Free AI scanning lowers the cost of finding a bug in an open source library to almost nothing, so disclosure volume will climb for years.
- Finding is not fixing. Help Net Security reported that roughly 29,000 candidate issues over six months produced about 6,000 confirmed vulnerabilities, which shows how much validation work sits between a scan and a patch.
- Your exposure is indirect. Most SMBs consume open source through commercial products, so your risk depends on how fast each vendor ships the upstream fix.
- Inventory decides speed. A business that knows which products contain which libraries can act on a disclosure in hours rather than weeks.
- Attackers read the same reports. Once a fix is public, the vulnerable code path is documented, and unpatched systems become the easiest target on the internet.
These points apply whether you run five servers or five hundred. They matter most for firms in regulated fields such as healthcare, finance and legal, where a known unpatched flaw can turn a breach into a compliance finding.
Why AI Vulnerability Scanning Changes the Patch Math for SMBs
AI vulnerability scanning changes the patch math because it raises the rate of new disclosures faster than most small IT teams can raise their rate of patching. For two decades, the number of open source flaws found each year was bounded by how many skilled human researchers had time to read code. That ceiling is gone.
Our team has watched the early effect already. Over the past year we have seen clients receive vendor advisories for libraries they had never heard of, buried three layers down in a product they bought for an unrelated reason. A PDF rendering library inside a document management system. A compression library inside a backup agent. A logging framework inside a building access controller. Each advisory arrived with a severity score, a vague timeline and no clear instruction for the customer.
Here is the arithmetic that concerns us. If a typical SMB runs forty commercial applications, and each one bundles dozens of open source components, the business depends on well over a thousand pieces of code it has never reviewed. When AI scanning multiplies the discovery rate, even a modest increase in confirmed flaws produces a steady drip of advisories touching that estate. The old rhythm of a monthly patch window and an annual audit was built for a slower stream.
The upside is real. Anthropic said projects that join OSS Scanner receive periodic scans by its strongest models at no cost, and that the service draws on its experience finding vulnerabilities during Project Glasswing. Better upstream code helps everyone. Your job is to make sure the fixes reach your systems before an attacker reaches the flaw.
How AI Vulnerability Scanning Differs From Traditional Dependency Scanning
AI vulnerability scanning differs from traditional dependency scanning because it reasons about how code behaves, while dependency scanners match version numbers against a list of already published flaws. Both have a place in a mature program, and confusing them leads to false confidence.
What reasoning-based scanning catches that version matching misses
Reasoning-based scanning catches flaws that have never been published, because the model reads logic rather than looking up a database entry. A classic software composition analysis tool opens a manifest file, sees that a product uses version 2.3 of a library, and checks a feed of known CVEs, the public identifiers assigned to disclosed vulnerabilities. If nobody has reported a flaw yet, the tool reports nothing. An AI model can trace how untrusted input moves through a parser and notice that a length check happens after a copy instead of before it. Supporters argue this is the first practical way to audit the long tail of small, underfunded libraries that no human team will ever review. Skeptics point out that models also produce confident reports about flaws that cannot be triggered in practice. Both positions hold some truth, which is why the confirmation rate matters more than the raw count.
Why validation is now the bottleneck
Validation is now the bottleneck because a candidate finding only becomes a fix after a person reproduces it, judges its impact and writes a patch. The reported gap between 29,000 candidates and roughly 6,000 confirmed issues tells the story. Maintainers of popular projects have already complained about a flood of low-quality automated reports, and many of those maintainers are volunteers. One view holds that services with stronger internal triage, such as Anthropic reporting that 88 percent of an early batch of high and critical findings met its disclosure standard, will reduce that noise. Another view holds that any increase in volume strains people who maintain code on nights and weekends. For a business owner, the practical lesson is simple: expect uneven patch timing across the products you depend on.
Where a software bill of materials fits
A software bill of materials, or SBOM, is a machine-readable list of every component inside a product, and it is the bridge between an upstream disclosure and your own systems. Without one, you learn you are affected only when a vendor chooses to tell you. With one, you can search your own records the morning a flaw is announced. Some vendors now ship SBOMs routinely. Others treat them as confidential. Advocates see SBOMs as the single most useful transparency step in software supply chain security. Critics note that a list of components says nothing about whether the vulnerable function is actually reachable. Pairing an SBOM with a VEX statement, a vendor note saying whether a product is exploitable, answers that second question.
5 SMB Risks When AI Finds Flaws in Open Source Software
The five risks below are the ones we see most often when a new wave of open source disclosures meets a small business that was not set up to absorb it. None of them requires exotic attackers, which is what makes them dangerous.
Risk 1: You cannot see the open source inside your commercial software
The first risk is invisibility: most SMBs have no record of which open source libraries live inside the products they license. Your accounting package, your phone system and your VPN appliance each carry their own bundle, and none of it appears on an invoice. When a disclosure lands, the honest answer to “are we affected” is often “we do not know.” We recommend starting with a list of every application and appliance that touches the internet or holds sensitive data, then asking each vendor for an SBOM. A formal vulnerability assessment can fill gaps by fingerprinting what is actually running.
Risk 2: Vendor patch lag leaves a public flaw open on your network
The second risk is the gap between an upstream fix and your vendor shipping it. When a library maintainer releases a patch, every commercial product that bundles that library must rebuild, test and release its own update. Some vendors do this in days. Others take months, and a few never do it for older product lines. During that window, the flaw is public and your system is not fixed. Our team tracks this lag per vendor for clients, because it is the best predictor of where a breach will start. Our guide to testing, patching and vulnerability scanning covers how to fold vendor updates into a regular cycle.
Risk 3: Exploit development speeds up after disclosure
The third risk is that the same AI tools that find flaws can help attackers turn a published fix into a working exploit. A patch shows exactly which lines changed, and comparing the old and new code points straight at the weakness. Historically, this “patch diffing” took a skilled researcher days. With model assistance, the time shrinks. That compresses the safe window between a fix appearing upstream and attackers scanning the internet for systems that lack it. Businesses that still patch on a fixed monthly calendar should add an emergency lane for internet-facing systems, with a target measured in days.
Risk 4: Alert volume buries the flaws that matter
The fourth risk is alert fatigue: when every scanner and vendor feed reports more findings, a small team stops reading them. We have walked into environments with thousands of open findings in a dashboard nobody had opened for months. The problem was never a lack of data. It was the absence of a rule for what gets fixed first. A workable rule ranks issues by three facts: whether the system is reachable from the internet, whether a public exploit exists, and whether the system holds regulated or financial data. Our vulnerability management guide for SMBs walks through that triage model in more detail.
Risk 5: Your own code and scripts go unreviewed
The fifth risk sits closer to home: the custom scripts, website themes, plugins and small internal apps your team or a contractor built. Free AI scanning programs target public open source projects, not the private code that runs your intake form or customer portal. Yet that code usually imports the same libraries and receives far less review. If a contractor built your client portal three years ago and nobody has touched it since, its dependencies are frozen at whatever versions were current then. Commissioning penetration testing on custom applications closes the gap that public scanning programs leave open.
Questions to Ask Your Software Vendors and IT Provider About Open Source Risk
The fastest way to reduce open source exposure is to ask your vendors and your IT provider a short set of direct questions and record the answers. You do not need to read code to hold suppliers accountable.
Ask for an SBOM and a VEX statement
Ask every vendor whose product touches sensitive data whether it can provide an SBOM and, when a major disclosure hits, a VEX statement saying whether its product is affected. Vendors that answer quickly usually have mature build processes. Vendors that refuse are telling you something about how they will behave during an incident. Some smaller suppliers will say they lack the tooling, and that answer is honest. In those cases, ask for a written commitment to notify you within a set number of days of any upstream disclosure affecting their product.
Ask for a patch commitment in writing
Ask each vendor how many days, after an upstream fix, it commits to shipping a patched release for critical and high severity flaws. Put the answer in your contract or renewal notes. Our team has seen vendors promise “as soon as possible” and deliver in four months. A number creates accountability. Pair that commitment with your own internal target, so you know how long a patched release sits before your team installs it. Our post on how to implement a vulnerability management process includes a template for tracking both clocks.
Ask your IT provider how it handles out-of-cycle patches
Ask your managed IT or security provider what happens when a critical open source flaw drops on a Tuesday afternoon. Who reads the advisory, who checks your inventory, and who approves an emergency change? A provider running managed security services should answer with names, timelines and a change process, not a general reassurance. Ask also how the provider separates scanning from testing, since the two answer different questions, as covered in our comparison of vulnerability scanning vs penetration testing. Healthcare practices should review the added expectations in our article on healthcare vulnerability scanning risks.
Frequently Asked Questions
Does AI vulnerability scanning of open source software make my business less safe?
AI vulnerability scanning makes open source code safer over time, but it raises short-term risk for businesses that patch slowly. More flaws get found and fixed upstream. The danger is the window between a public fix and the moment your systems receive it.
Can my business enroll in Anthropic’s OSS Scanner?
OSS Scanner is aimed at maintainers of open source projects, not at companies that consume software. Most SMBs benefit indirectly when the libraries inside their products get scanned. Your own custom code needs its own review through testing or a code audit.
What is the difference between an SBOM and a vulnerability scan?
An SBOM lists the components inside a product, while a vulnerability scan checks systems for known weaknesses. The SBOM tells you what you have. The scan tells you which of those things is currently exposed, and the two work best together.
How fast should an SMB patch a critical open source flaw?
We recommend a target of a few days for internet-facing systems once a vendor releases a fix, and your regular cycle for internal systems. Systems holding regulated data deserve the faster lane. The right target depends on your exposure, but a written number beats an informal intention.
Do I need a security team to manage open source risk?
You do not need an in-house security team, but you do need someone accountable for inventory, vendor follow-up and emergency patching. Many SMBs assign that role to a managed security provider. What matters is that a named person owns the process.
Who Is Behind This Advice
Mindcore Technologies has spent years running vulnerability management for small and midsize businesses in healthcare, finance, legal and professional services, which means our team handles real advisories against real client environments every week. We build inventories, chase vendors for patch timelines and run emergency change windows when a critical flaw goes public. The guidance in this article comes from that daily work, not from theory. Mindcore is led by CEO Matt Rosenthal, who focuses on helping growing companies build security programs that hold up under regulatory scrutiny without slowing the business down.
Get Ready for the Next Wave of Open Source Disclosures
AI vulnerability scanning of open source software is going to find more flaws, faster, for years to come, and the businesses that come out ahead will be the ones that can turn a disclosure into a deployed patch without panic. That readiness rests on a few habits you can build now: an inventory of the software you run and the components inside it, written patch commitments from your vendors, a triage rule that ranks findings by exposure and exploitability, an emergency lane for internet-facing systems, and regular testing of the custom code that public scanning programs never see. None of these steps requires a large budget. Each one shortens the time between a public fix and a protected system, which is the only window an attacker can use. If you want help mapping your open source exposure, setting vendor expectations or building a patch process your team can sustain, book a free strategy call with our team, and we will walk through where your environment stands today and what to fix first.

