Device code phishing is an account takeover that never touches the victim’s password. The attacker starts a sign-in on their own machine, receives a short user code from Microsoft, and talks the victim into typing that code into Microsoft’s real sign-in page. The victim authenticates, completes multi-factor authentication, and hands the resulting access token to the attacker without ever seeing a fake login screen. We have watched this land in tenants that had conditional access, mandatory MFA, and a well-drilled reporting culture. The controls did not fail; they were answering a question the attack does not ask. This article walks the six risks our team sees Microsoft 365 administrators miss, and what closes each one.
Overview: What Microsoft 365 Administrators Need to Know First
Five points carry most of the weight here, and they matter most to IT managers and security leads running tenants between 50 and 500 seats, where there is no dedicated identity team.
- The OAuth device authorization flow exists for televisions, conference-room displays, and command-line tools that cannot render a browser. It is legitimate, it ships enabled, and attackers use it exactly as designed.
- No password is stolen at any point, so password rotation, breach-corpus monitoring, and a password manager rollout all sit outside the attack path.
- MFA is completed by the real user on the real page, which means an MFA mandate on its own stops nothing.
- The prize is the token, not the credential. Once it is issued, the attacker can register devices and enroll management agents before anyone reads a sign-in alert.
- The control that actually closes this is conditional access scoped to the device code grant, and most tenants have never written that policy.
Why Device Code Phishing Walks Past Controls That Stop Ordinary Phishing
Device code phishing defeats mainstream anti-phishing controls because every one of those controls is looking for a forged sign-in page or a stolen password, and this attack produces neither. Our team runs into the same conversation each time: the tenant has done the work, the user did what training taught, and the account still went. The gap is architectural, not behavioral. If you want the baseline that these controls do cover, our overview of phishing attacks is the right starting point, and this article is what sits beyond it.
Risk 1: The Sign-In Page Is Genuinely Microsoft’s
The first risk is that there is no fraudulent page to spot, so awareness training built on URL inspection never fires. Everything a cautious user is taught to check will pass. The certificate is valid, the domain is Microsoft’s, and the branding is correct because it is real. The counter-argument deserves a hearing: training is not wasted, and a user who questions an unexpected request will still stop this attack on the pretext rather than the page. Both readings hold. Where we land is that URL inspection is a control with a defined scope, and this attack sits outside it. Our guidance on how to detect a phishing email still applies to the lure; it simply cannot apply to the sign-in step, because that step is authentic.
Risk 2: Completing MFA Is the Attack, Not the Defense
The second risk is that multi-factor authentication runs to completion and works correctly, which converts a security control into the final step of the compromise. The user approves a push or enters a code from their authenticator app, and that approval is genuine. Some security leads argue this proves MFA is worthless against modern tradecraft. We disagree, and the numbers on credential stuffing back us up: MFA still blocks the overwhelming majority of commodity attacks. The accurate statement is narrower. MFA proves the human is present; it does not prove the human understands which session they are approving. That distinction is the whole attack.
Risk 3: The Lure Does Not Arrive by Email
The third risk is that the initial contact often bypasses mail security entirely by coming through a public web form. In the campaign eSentire documented in late August 2026, the operators submitted routine procurement inquiries through business contact forms, built a short correspondence, then sent a file-transfer link holding a password-protected HTML file. Nothing in that sequence passes through an inbound mail gateway in a form it can judge. There is a reasonable objection that this makes the attack expensive and therefore rare. It is more labor than a mass campaign, which is why targets are chosen rather than sprayed, and that selectivity is closer to spear phishing attacks than to bulk mail. Rare and targeted is not the same as unlikely for you.
The Device Code Phishing Risks That Surface After the Token Is Issued
The second set of risks begins the moment the access token exists, and they are the ones that turn a single approval into weeks of access. Administrators tend to model this as a sign-in event to be reviewed in the morning. Our team models it as a race that has already been lost by the time a human reads anything, which changes what you build. The same pattern of treating a security surface as a place attackers arrive rather than a place they persist shows up in our breakdown of a phishing attack that impersonated security alerts.
Risk 4: Token Replay Starts in Seconds, Not Hours
The fourth risk is that the window between approval and abuse is far shorter than any human-speed response. In the documented case, the stolen token was in use five seconds after the victim authenticated, and within 78 seconds the operators had registered three devices in Entra ID and completed an Intune enrollment. A user who realizes the mistake immediately and calls the help desk is still minutes behind. Against that, an argument for fast human reporting is worth keeping: reporting shortens the total dwell time even when it cannot prevent the initial foothold, and it is often how anyone finds out at all. Both are true. Plan for automated revocation as the primary response and treat the phone call as the thing that tells you where to look.
Risk 5: Access Survives the Response Most Teams Run
The fifth risk is that registering a device converts a stolen session into standing access that a password reset does not touch. This is where our team sees incidents reopen a week later. The response runs correctly on paper: reset the password, revoke sessions, close the ticket. Meanwhile the attacker-registered device holds its own relationship with the tenant and can request fresh tokens. There is a defensible position that a full identity reset should be standard for any suspected token theft, and we agree it should be. The practical problem is that most runbooks were written when a password reset was the boundary of the problem, and nobody has revised them. If you manage enrollment through our mobile device management practice, the registration inventory is where this becomes visible.
Risk 6: Nobody Is Watching the Device Code Grant
The sixth risk is that the device code flow is enabled by default in most tenants and almost never audited, so there is no baseline to compare an anomaly against. Ask your team how many device code sign-ins your tenant issued last month and who they belonged to. In the tenants we assess, that question usually cannot be answered from existing reporting. The counter-position is that disabling the flow outright can break legitimate hardware, and that is a real constraint in organizations running conference-room systems or developer tooling. The resolution is not a blanket switch. It is a scoped policy plus a report someone actually reads, which is how the phishing trends we track get caught early rather than during an incident.
What a Device Code Sign-In Looks Like in Your Entra ID Logs
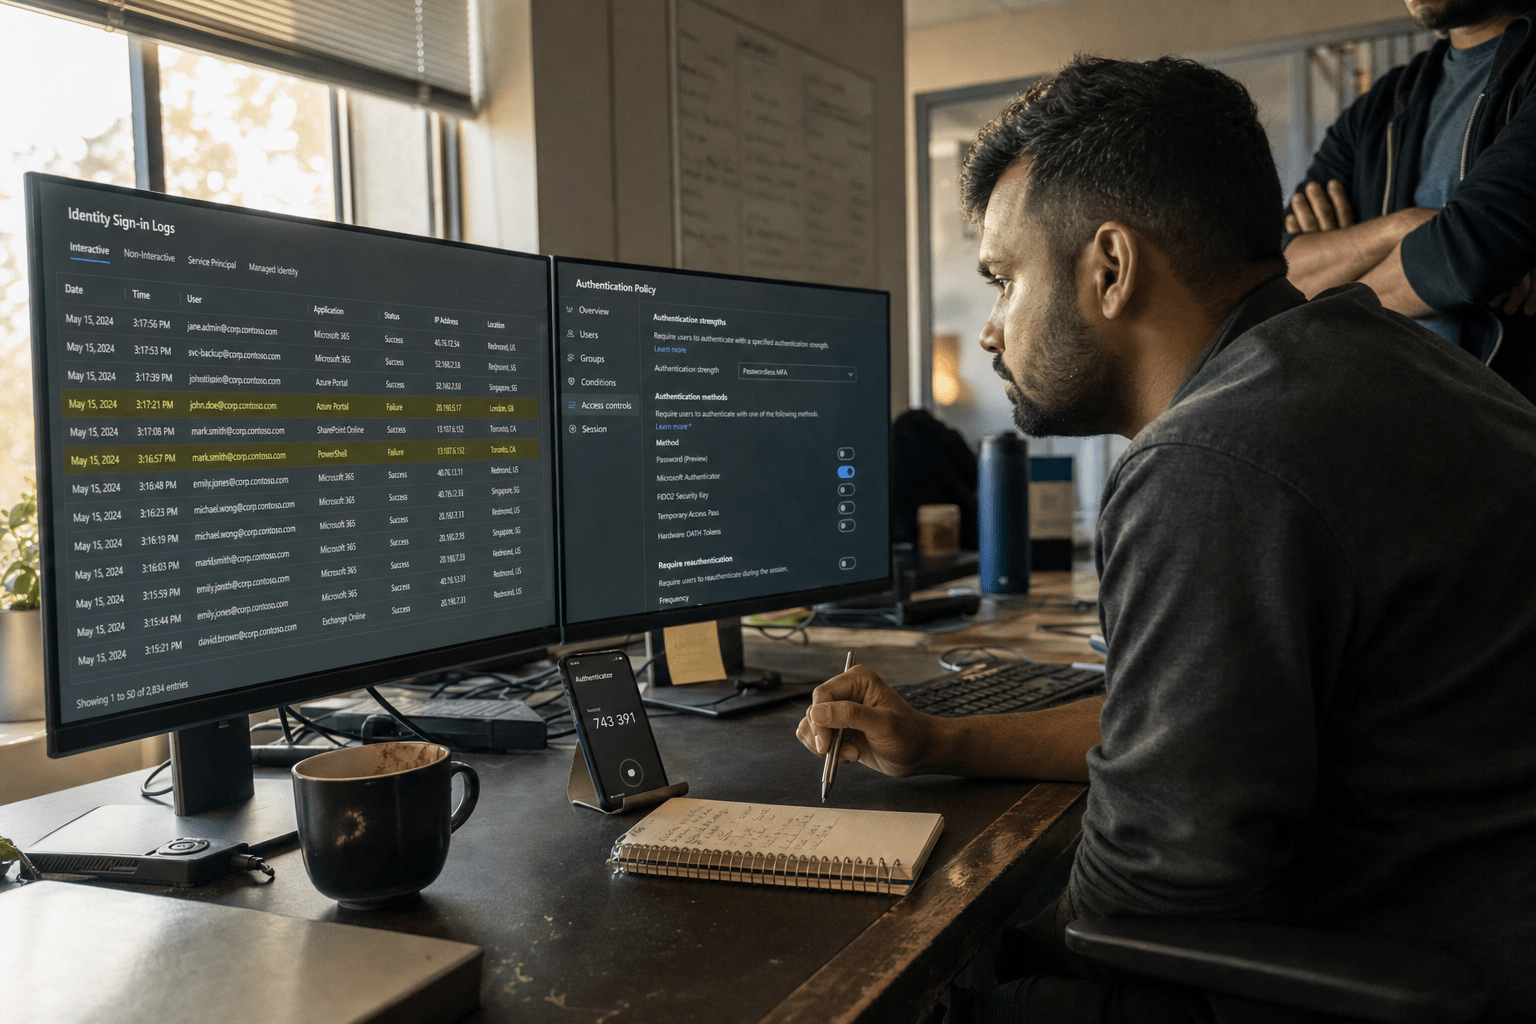
A device code sign-in is identifiable in Entra ID sign-in logs by an authentication protocol value of “Device Code” on an interactive sign-in, and that single field is the whole detection story. Most administrators have never filtered on it, which is why the first time anyone looks is during an incident. Pulling the last 90 days takes a few minutes and gives you something more useful than a policy: a list of the accounts and applications in your tenant that genuinely use this flow, which is exactly the exclusion group you will need later.
Separating Legitimate Hardware From an Attack in the Same Log
Legitimate device code sign-ins cluster, and attacker ones do not, which is what makes the two separable without any extra tooling. A conference-room display authenticates from the same office address on a predictable rhythm, under a shared account, against the same application. A developer signing in to a command-line tool shows up from a handful of addresses with a recognizable client identifier. The attacker sign-in is a one-off from an address nobody at your organization has used, under a real employee’s account, followed within minutes by a registration event. Reasonable people push back here that a hybrid workforce makes location a weak signal, and that is fair on its own. The combination is what carries the weight: a first-ever device code sign-in for that user, from a new address, followed by a device registration, is not an ambiguous pattern.
Why the Application Name in the Log Is Worth Reading
The application recorded against a device code sign-in tells you what the token was minted for, and attackers favor first-party Microsoft client identifiers because those attract no scrutiny. Seeing a familiar Microsoft application name is therefore not reassurance. What matters is whether that application has any business being used through this flow by that person. Our team keeps the answer in writing per tenant, because an on-call engineer at two in the morning should not be deciding from memory whether a given client identifier is normal for your organization.
How Our Team Closes Device Code Phishing in an Entra ID Tenant
Closing device code phishing takes one conditional access policy, one inventory pass, and one change to the incident runbook, and most tenants can complete all three inside a working week. These are the steps we run, in order:
- Write a conditional access policy that blocks the device code grant for all users, then add an exclusion group holding only the accounts that genuinely drive headless hardware. Start in report-only mode for a week and read what it catches before you turn it on.
- Pull the device registration and Intune enrollment inventory and reconcile every entry against a person and a purchase. Anything you cannot name, disable rather than delete, so the forensic record survives.
- Add token revocation to the runbook as the first action for any suspected session compromise, ahead of the password reset, and confirm the help desk can execute it without waiting for an escalation.
- Alert on device registration events rather than on sign-ins alone. A registration from an unfamiliar location within minutes of an interactive sign-in is the signal that matters here.
- Brief users on the one sentence that actually protects them: nobody legitimate will ever read you a code to type into a Microsoft page. That single rule covers this attack and the ones our team expects next, including the Microsoft Teams phishing attacks now hitting the same tenants.
Frequently Asked Questions
Does device code phishing work if we have MFA turned on for everyone?
Yes, and that is the point of the technique. The victim completes real multi-factor authentication on Microsoft’s real sign-in page, so the attacker inherits a token that already satisfies the MFA requirement. Conditional access scoped to the device code grant is the control that stops it.
Can we just disable the device code flow entirely?
Most organizations can, and for many it is the right call. Check first for conference-room displays, shared-device sign-ins, and command-line tooling your developers rely on, because those break without an exclusion. Running the policy in report-only mode for a week surfaces every legitimate user before you enforce it.
How do we tell whether this has already happened in our tenant?
Review device registration and Intune enrollment events going back at least 90 days and match each one to a known person and device. Then look for interactive sign-ins followed by a registration within a few minutes from a different location. Our team runs this reconciliation as part of an identity assessment.
Is a password reset enough after a device code compromise?
No. The attacker never had the password, so resetting it changes nothing about their access. You need to revoke refresh tokens, remove any attacker-registered devices, and review what was enrolled before the account is safe to return to service.
How is this different from an AI-generated phishing campaign?
The lure may well be written by a model, and the pretexts we see are noticeably better than they were a year ago, which we cover in our piece on AI-generated phishing. The difference is the mechanism: AI improves the persuasion, while device code phishing changes what the attacker walks away with.
Who Is Behind This Guidance
Our team has spent the past two years running identity assessments across Microsoft 365 tenants in professional services, healthcare, and manufacturing, most of them between 50 and 500 seats. That work is where the pattern in this article came from: the same conditional access gap, tenant after tenant, in organizations that had done everything their previous provider asked of them. We are not describing a theoretical weakness. We are describing the finding we write up most often.
Mindcore is led by Matt Rosenthal, who has built the practice around one principle that shapes work like this: the point of a security program is that your people can do their jobs without becoming the last line of defense. That is why our recommendations here end in policy and automated revocation rather than in more training.
Talk Through Your Tenant With Someone Who Has Seen This
Device code phishing is a narrow gap with a short fix, and it stays open in most tenants only because nobody has been told to look at the device code grant. If the six risks above are not currently on anyone’s list at your organization, that is the finding, and it is a good one to have before an incident rather than during a response. Reconciling your device registrations and writing one conditional access policy is a week of work that removes an entire class of account takeover from your exposure.
Our team can walk your tenant with you, show you what your device code sign-ins look like today, and hand you the policy we would deploy. If that would be useful, book a free strategy call and bring whoever owns your Microsoft 365 tenant. You will leave the call knowing whether this is already a problem for you, which is the question worth answering first.