AI screening rules covering automated decisionmaking technology reach full compliance on January 1, 2027, and they apply to employers rather than only to the vendors who build the tools. The obligations are concrete: a documented risk assessment before use, a notice to candidates and employees before the technology runs, working access and opt-out rights, and oversight of the vendor whose product is doing the scoring. Our team has watched several clients conclude this does not apply to them because they never bought anything labeled artificial intelligence. That is the wrong test. The rules follow what the technology decides, not what the invoice calls it, and the most common in-scope system is a feature that came bundled with an applicant tracking platform.
Overview: What Employers Should Take From This
Five points carry the practical weight, and they matter most to HR leaders, operations directors, and general counsel at firms that hire in volume or use scoring features in an HR platform.
- Coverage turns on the decision, not the product name. A resume-ranking filter counts.
- The test that matters is whether a person exercised meaningful human involvement in the decision.
- A documented risk assessment must exist before the technology is used, not after a complaint.
- Candidates and employees get a pre-use notice and rights to access information and opt out.
- Your vendor’s compliance posture does not transfer to you. The obligation sits with the employer.
Which Employers the AI Screening Rules Actually Reach
The rules reach employers who meet the state privacy statute’s coverage thresholds and use automated decisionmaking technology in employment decisions, which is a broader group than most HR leaders assume. Coverage does not require a dedicated AI initiative, a data science team, or a large budget. It requires two things: crossing the privacy law’s applicability thresholds, and letting a technology participate in a decision about hiring, promotion, discipline, or similar. Our cybersecurity compliance team runs this scoping in a single session, because the wrong answer costs a year of unbuilt process.
What Counts as Automated Decisionmaking Technology
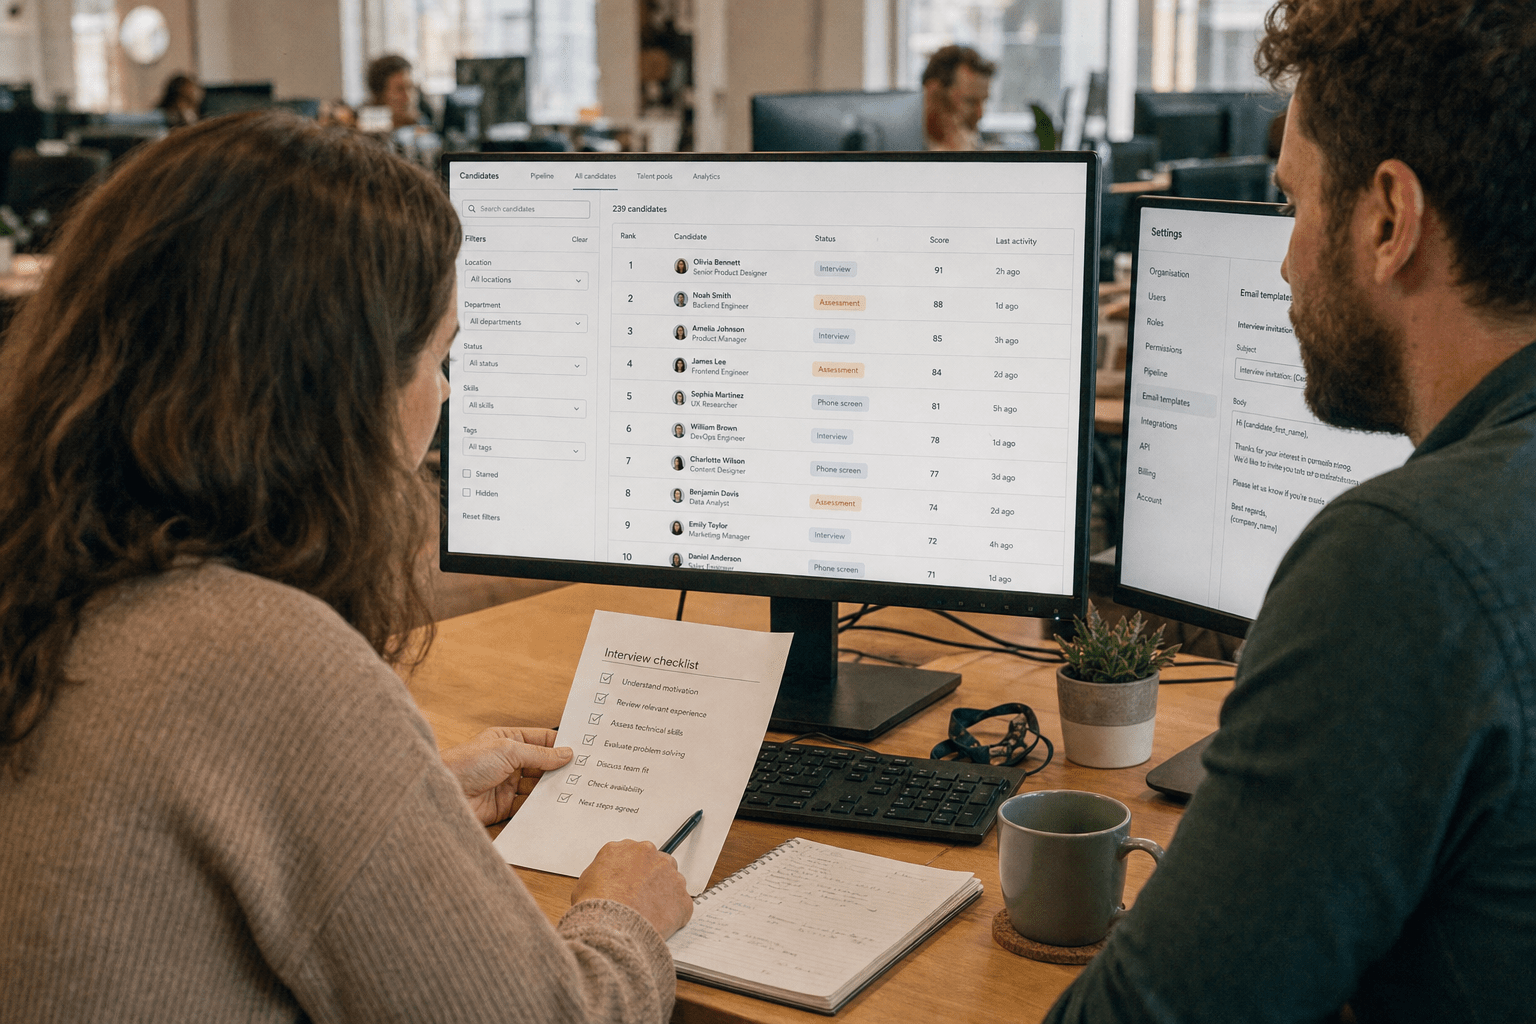
Automated decisionmaking technology means a system that processes personal information to execute or substantially facilitate a decision about a person, and the phrase substantially facilitate is where most organizations get caught. A tool that flatly rejects candidates is obviously in scope. So is a tool that ranks 400 applicants and presents the top 20, because the ranking shaped which people a human ever saw. There is a genuine counter-argument that a ranking is only a convenience and the human still chooses, and in some workflows that is true. What separates the two is whether anyone meaningfully reviewed the people who were filtered out. If nobody looked below the cut line, the system decided.
The Meaningful Human Involvement Test
Meaningful human involvement means a person with authority actually reviewed the output and could have reached a different conclusion, and it is judged by how the process works rather than by what the policy says. Our team asks three questions during an assessment: does the reviewer see the information the system used, do they have time to reach an independent view, and has anyone ever overridden the system. A process where a recruiter approves 98 percent of recommendations in under a minute each is not meaningful involvement, whatever the workflow diagram claims. The counter-position from HR leaders is fair: speed is the entire reason the tool was bought, and a slow review negates it. That tension is real, and the resolution is usually to narrow where the tool is allowed to decide rather than to pretend the review is deeper than it is.
The Systems Nobody Thinks to Inventory
The in-scope systems at most organizations are features inside platforms already in use rather than standalone AI products, which is why an inventory built by asking about AI tools comes back empty. Look instead for ranking, scoring, matching, or recommendation features inside your applicant tracking system, your background screening provider, your scheduling platform, and any assessment or skills-testing service. Add anything that flags employees for attention, including productivity monitoring and attrition prediction. Our piece on AI data privacy risks to fix before 2027 covers the overlapping privacy obligations these same systems trigger.
The Four Obligations That Take Real Lead Time
Four obligations carry actual work, and each has a dependency that makes a January start impossible. Policy language can be written quickly; these cannot. Our managed IT and compliance work sequences readiness around them for exactly that reason.
Risk Assessments Have to Exist Before Use, Not After
A documented risk assessment must be completed before the technology is used for a covered decision, weighing the benefits against the risks to the people affected. This is a written artifact a regulator can request, and its absence is the failure, not its quality. The work is heavier than it sounds because a serious assessment requires knowing what data the system consumes, and most employers cannot answer that about a vendor feature without asking the vendor. That request has a lead time of weeks. There is a reasonable view that these assessments become paperwork rituals, and some do. We have also seen one stop a deployment cold when the room learned the scoring model used a proxy nobody was comfortable defending.
Pre-Use Notices Change Your Application Flow
Candidates and employees must be told before the technology is used on them, which means the notice belongs in the application flow rather than in a policy nobody opens. This is an engineering change to your careers page, your application confirmation, and often your offer and review workflows. It also forces a decision most organizations have avoided: describing in plain terms what the system does. Writing that sentence honestly is harder than building the notice, and it frequently sends teams back to the vendor for a clearer answer about how the scoring works.
Access and Opt-Out Rights Need a Working Path
Affected individuals get rights to access information about the automated decision and, in defined circumstances, to opt out, and each right needs a route that functions end to end within the response window. The hard part is the same one that breaks every rights-request program: locating the relevant records across an applicant tracking system, a vendor’s platform, and whatever exports live in a shared drive. Building this in December means testing it in January with a real request from a real person, which is the worst possible time to discover the vendor cannot produce the information. The general pattern for handling regulated requests is covered in our overview of compliance regulations for SMBs.
Vendor Management Is Now Your Obligation, Not Theirs
The employer carries the compliance obligation even when the technology belongs to a vendor, so contracts and documentation need to reflect that before the deadline. Ask each vendor for four things in writing: what personal information the feature processes, how the output is generated in terms you can repeat to a candidate, what they will provide toward your risk assessment, and how they will support an access request. A vendor who cannot answer within a few weeks is telling you something useful about January. The counter-argument that a large vendor’s compliance program should be sufficient does not survive the text of the rules, which place the duty on the entity making the employment decision. That is also the pattern under FTC compliance, where outsourcing the work never outsources the responsibility.
What Happens to the Records You Are Now Required to Keep
The obligations above all produce documents, and those documents become the evidence in any later inquiry, which changes how you should store them from day one. Most organizations build the assessment, save it to whoever wrote it, and move on. That is enough to satisfy the requirement on paper and not enough to answer a question eighteen months later, when the person who ran the assessment has changed roles and the vendor has shipped three versions of the feature.
Version the Assessment Against the System It Describes
A risk assessment describes a system at a point in time, so it stops being accurate the moment the vendor changes the model behind the feature. Our team records the vendor, the feature, the version or release date, and the date of the assessment together in one place, and we set a review trigger tied to vendor release notes rather than to a calendar. The objection that this is heavier than the rules require is correct in the narrow sense. It is also what makes the document defensible, because an assessment that describes a system you no longer run is worse than an obviously old one: it reads as current and is not.
Keep the Decision Trail, Not Just the Policy
The question an inquiry asks is what happened to a specific person, which a policy cannot answer. Keep a record of which system touched which decision and who reviewed it, at the level of the individual decision rather than the workflow. In most applicant tracking platforms this is a reporting configuration rather than new software, and turning it on costs nothing today while reconstructing it later may be impossible. This is the same principle that governs every regulated record we help clients manage: the artifact that proves compliance is created at the time of the act, not at the time of the question.
What to Do Between Now and January
This is the order our team runs when a client has roughly a quarter before an AI governance deadline. It front-loads the items with external dependencies:
- Week 1: inventory every system that ranks, scores, matches, filters, or flags a person, including features inside platforms you already own. Ask each department rather than relying on a software list.
- Weeks 1 to 3: send the four-question request to every vendor on that list, because their response time is the longest pole in the project.
- Weeks 2 to 5: document the decision workflow for each in-scope system and record honestly whether a human meaningfully reviews the output. Where they do not, decide whether to add review or to narrow the system’s role.
- Weeks 4 to 8: complete the risk assessments using what the vendors returned. Record the date and who approved each one.
- Weeks 6 to 9: implement the pre-use notices in the application and employment workflows, then test them as a candidate would see them.
- Weeks 8 to 11: build and test the access and opt-out path end to end with a real record.
- Week 12: update policies last, so they describe the process you built.
Train the people who will receive these requests, because a recruiter who does not recognize an access request will not route it, and the clock runs anyway. That gap is the same one we cover in our work on security awareness training and compliance mandates, applied to a different kind of incoming message.
Frequently Asked Questions
Do these rules apply if we only use a resume-ranking feature?
Very likely yes. A tool that ranks candidates and determines which ones a human sees substantially facilitates the decision, which is the standard the rules use. Whether it is marketed as AI does not affect the analysis.
What if a recruiter reviews every recommendation?
That depends on whether the review is meaningful in practice. A reviewer who sees the underlying information, has time to form an independent view, and sometimes disagrees is meaningfully involved. Rubber-stamping at speed is not, regardless of what the written process claims.
Is our vendor responsible for compliance?
No. The obligation sits with the employer making the decision. Vendors can support your risk assessment and your access requests, and a good one will, but a regulator’s inquiry comes to you. Our approach to ongoing AI evaluation and risk control is built around that division.
We are a small employer. Are we in scope?
It depends on whether you meet the underlying privacy law’s coverage thresholds, which turn on data volume and revenue rather than headcount. A small company processing a large volume of applicant data can be covered while a larger one is not.
What is the realistic risk if we do nothing by January?
Enforcement in this area tends to begin with an inquiry rather than a penalty, and the first request is usually for documentation. The organizations that struggle are the ones with no risk assessment to produce. Our emergency compliance support exists for that call, and it is a worse position than starting now.
Who Is Behind This Guidance
Our team has spent this year building system inventories for clients who were confident they had no AI in their hiring process and who each found between two and six in-scope features once we looked inside the platforms they already owned. That inventory is the part of this work that cannot be skipped or bought, and it is where we spend most of our time. The legal summaries are available everywhere; the list of what is actually running in your organization is not.
Mindcore is led by Matt Rosenthal, whose position on this kind of deadline has been consistent: a compliance project should leave you understanding your own systems better than before it started. That is the standard we hold this one to, because the inventory keeps paying off long after the filing date passes.
Find Out What Is Actually Screening Your Candidates
If nobody at your organization can name every system that ranks or scores a person, that is the first finding, and it usually takes an afternoon to fix. January is close enough that vendor response times now sit on the critical path, which is the practical reason to start this month rather than after the holidays. Everything else in the project depends on that list existing.
Our team will build the inventory with you, send the vendor questions, and tell you plainly which systems put you in scope. Book a free strategy call and bring whoever administers your applicant tracking system. You will leave with a list, which is the thing every other obligation is built on.