

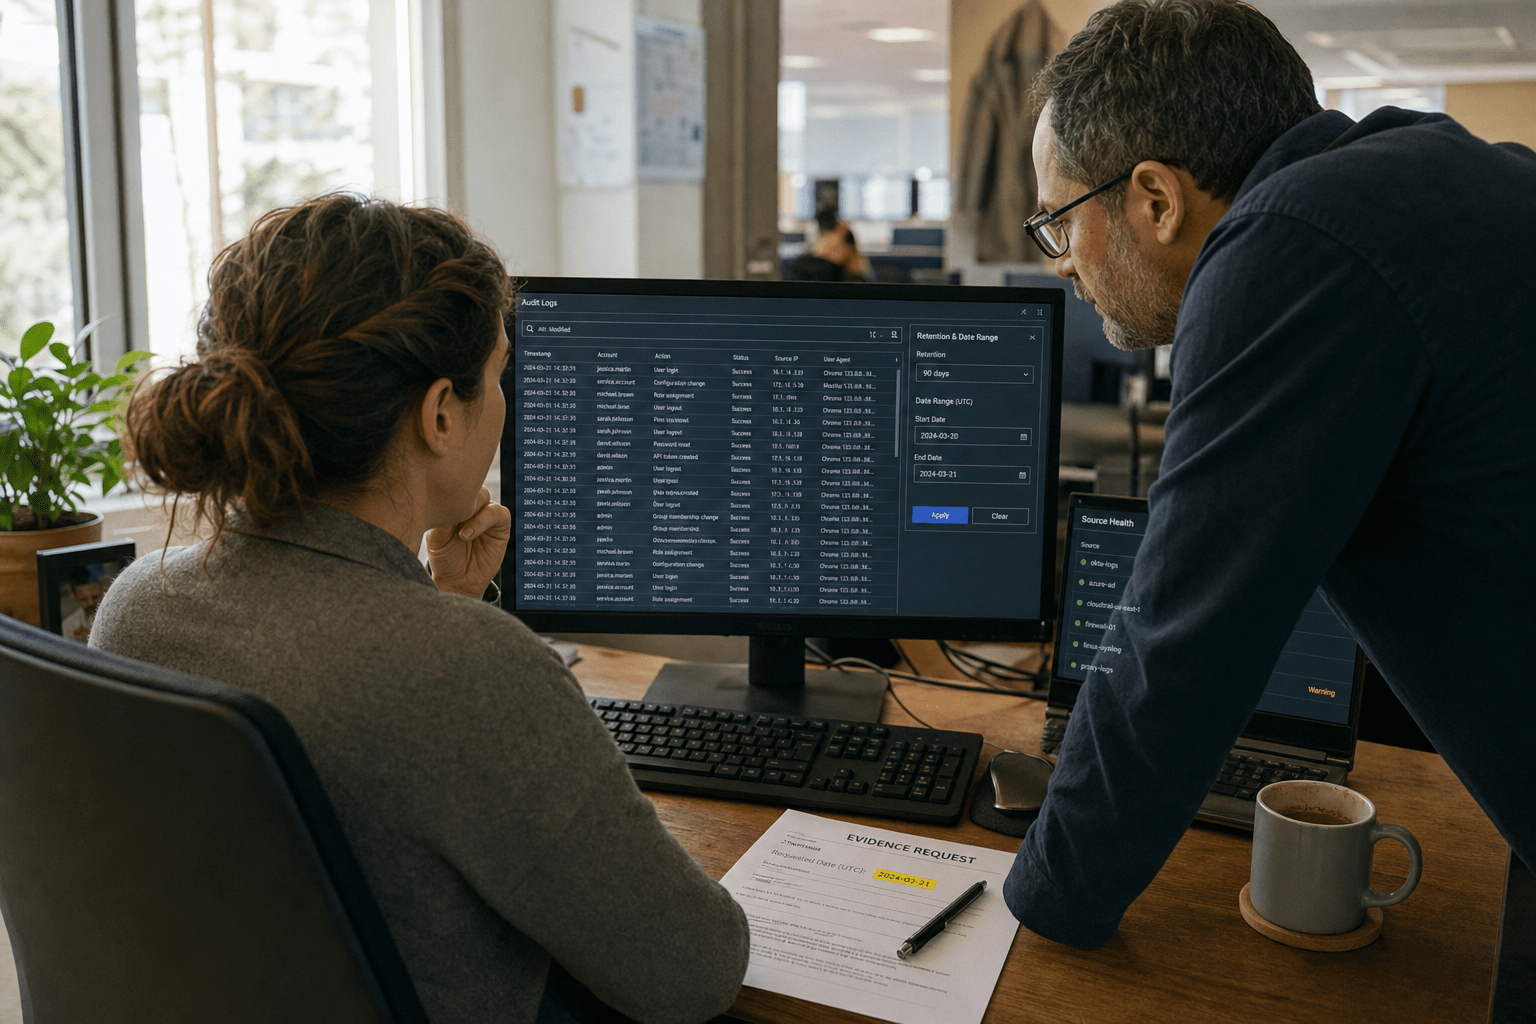
The best AI tools for audit trail documentation are the ones that make an old record retrievable and provable, not the ones that write the tidiest summary. An audit trail is the machine-generated sequence of who did what, to which object, at what time, across every system you are accountable for. When a regulator, an insurer, or opposing counsel asks what one account did on one day fourteen months ago, three things decide whether you can answer: whether the event was written at all, whether it arrived in storage, and whether you can show it has not been edited since. AI helps most at the query and narrative layer. It cannot recover a record that was never emitted.
Overview: What a Usable Audit Trail Has to Survive
- A dated question, not a general one. Evidence requests name an account, an object, and a window. Tooling that only shows the last thirty days answers a different question than the one you were asked.
- Silent loss. Agents stop shipping, ingest quotas fill, and sources get dropped during cost tuning. Almost none of that raises an alarm, so the gap is found during the request.
- Proof of no tampering. A record is worth less if the administrator being investigated could have edited it. Write-once storage and hash chaining are what turn a log into evidence.
- Identity that still resolves. People change names, mailboxes get converted, and service accounts get recycled. A trail keyed to a display name goes ambiguous within a year.
- A retrieval rehearsal. We treat an unrehearsed export the way we treat an untested backup. The first real attempt is the wrong time to learn the format.
This is written for IT managers and compliance leads at firms of roughly 50 to 500 people, where one person owns logging alongside six other duties, and where the budget conversation is real.
Why the Fourteen Month Question Breaks Most Log Estates
Most audit trail failures we see are retrieval failures rather than writing failures, and they surface at the worst moment because nothing tests retrieval until someone external asks. Before comparing platforms, sit down and try to answer one dated question from your own systems. What happens in the next twenty minutes tells you more than any vendor demo.
Searchable time is shorter than retention time
Retention and searchability are two separate numbers, and vendors quote the friendlier one. A platform may hold thirteen months of data while indexing only thirty or ninety days for interactive search. Older data sits in cold storage and has to be rehydrated, sometimes at per-gigabyte cost, sometimes on a multi-hour job. There is a fair argument for that design, because indexing everything hot is expensive and most queries are recent. The counterargument matters more at audit time: if your obligation covers a year and your hot window covers a month, you hold eleven months of records you cannot practically read. Get both numbers in writing, then price a rehydration of one older month so the cost is known before it is urgent. Write the hot window and the retention window into the same row of your control matrix, side by side, because the gap between them is the part an assessor will ask about and the part nobody documents.
The account in the log is not the person in the question
Audit trails key on identifiers, and identifiers move. A user who married and changed surnames, a contractor whose account was disabled and reissued, a shared mailbox converted to a distribution list: each one breaks a name-based search across a long window. Identity governance data resolves this when the trail stores immutable object identifiers, such as an Entra ID object GUID, rather than a display name. Plenty of application logs store only the friendly name, and those cannot be reconciled after the fact without a separate directory history. Before you buy a query layer, check which identifier your noisiest applications actually write, because no amount of natural language search fixes an ambiguous subject.
A deleted record and an event that never happened look identical
This property separates a log from evidence. If a record is absent, you cannot tell from the log itself whether the action never occurred or whether someone removed the entry. Sequence numbering, hash chaining, and write-once retention locks close that gap by making a removal detectable rather than invisible. The honest objection is cost and rigidity, since immutable storage cannot be cleaned up, so a mistake in scope is expensive and a privacy deletion request gets complicated. Our position is that the integrity requirement wins for the narrow set of sources answering accountability questions, and normal lifecycle rules are fine for everything else. Deciding that scope is the work, and it is where a cyber security audit earns its fee.
Stage by Stage: Where Audit Trail Records Actually Go Missing
Audit trail records are lost at three points, and each one needs a different fix, so diagnosing the stage before shopping saves a wasted purchase. Emission, transport, and storage fail differently and are owned by different teams. AI tooling sits downstream of all three.
Emission: the systems that write nothing until told
Default logging is thinner than most teams assume. Mailbox auditing, file-level read events, database object access, and administrative actions inside line-of-business applications are commonly off, sampled, or held for a short native window until somebody turns them up. The tradeoff is genuine, since verbose logging costs storage and can slow a busy database. Still, the asymmetry is stark: turning on an event class costs money going forward, while not having it costs you the answer permanently. Walk your accountable systems, list the event classes each one can emit, and record which are enabled today. That inventory is the denominator every later coverage claim depends on. Two event classes are worth turning on this week almost regardless of budget: administrative privilege changes, because they precede most of the activity anyone later asks about, and object deletions, because a deletion is the one action whose own evidence disappears with it.
Transport: agents that stop shipping and never mention it
A forwarder that dies quietly is the most common failure in the estate. The server keeps running, the application keeps working, and the log pipeline simply stops, so the absence of records reads as an absence of activity. The fix is a heartbeat rather than an alert on volume, because an alert tuned to a drop in events will miss a source that was always quiet. We look for platforms that track expected sources and flag any source silent for longer than its own normal interval. This is ground that continuous network security monitoring already covers, and folding audit-source health into that same watch list is cheaper than a second tool.
Storage: who holds the delete key
Ask who can shorten a retention policy, and how you would know they did. In most estates the answer is a small group of administrators with no separate approval and no second copy, which means the people most likely to be the subject of an investigation also control the record of it. Cloud object storage with an object lock in compliance mode, a separate account or tenant boundary, and retention changes that require a second identity all raise that bar without a large project. The counterweight is operational friction and the risk of locking data you regret keeping, so set the window deliberately against the longest obligation you actually carry rather than the longest one imaginable.
What the AI Layer Adds Once the Records Exist
The best AI tools for audit trail documentation earn their cost at retrieval and narration, converting a correct but unreadable record set into something a person can review and hand over. Four groups are worth separating, because they solve different halves of the problem and are often sold as though they were interchangeable.
Query layers over log platforms
Splunk, Microsoft Sentinel, Elastic, and Datadog now ship assistants that turn a plain sentence into their own query language, and this is the largest time saving on offer. It removes the bottleneck where one person who knows the query syntax becomes the constraint on every request. Treat generated queries as drafts: confirm the time zone, the index scope, and the field names before you trust a result, since a query that silently searched the wrong index returns a confident and empty answer.
Cloud native audit services
Microsoft Purview Audit, AWS CloudTrail with Lake, and Google Cloud Audit Logs give the cleanest trail for their own platforms and are already paid for in many tenants. Read the licensing line carefully, because longer retention and higher-value event classes usually sit in a premium tier, and the default window is often shorter than a compliance review period. These belong in your architecture as a source of truth for their own estate, not as the answer for the whole estate.
Integrity and archive tooling
This group is the least discussed and the most decisive. Object lock, write-once archive targets, and hash-chained ledgers make deletion detectable rather than plausible. Governance platforms such as Vanta, Drata, and AuditBoard sit alongside them, mapping stored evidence to control requirements and generating the request packages, which is real work removed from a small team.
Identity and AI agent trails
Two growing sources deserve their own line. Identity providers record consent grants, token issuance, and privilege elevation, which is where quiet persistence shows up. Separately, any AI agent acting inside your systems needs its own trail of prompts, tool calls, and approvals, and platforms including Monitaur, Fiddler AI, and IBM watsonx.governance exist for that record. Our view on both matches our view on AI tools across a security program: the model output is not the evidence, the linked source record is.
Two Numbers to Get Before You Sign
Pricing on log platforms turns on daily ingest volume and retention tier, so a shortlist built without those two figures produces quotes nobody can compare. Measure your current volume per day per source over a fortnight, including the sources you plan to turn on, because enabling mailbox and file auditing can double an estate’s volume. Then ask each vendor for the cost of holding one older month in searchable form, not archived form. Those two numbers convert a feature comparison into a budget decision, and they usually reorder the shortlist. In our experience the platform that wins on features rarely wins once a year of searchable retention is priced at real volume, and a two-tier design, hot for ninety days with a cheaper searchable archive behind it, tends to land closer to what a mid-sized firm can defend to a finance director. Firms working through this alongside a framework deadline often find the sequencing easier inside an existing cybersecurity compliance engagement, where the retention obligation is already written down, and our guide on preparing for a cybersecurity compliance audit covers the evidence side in more detail.
Frequently Asked Questions
What are the best AI tools for audit trail documentation to adopt first?
Start with a query assistant on the log platform you already run, because it removes the retrieval bottleneck without changing your architecture. Add integrity storage next, then governance mapping. Buying narrative tooling before you have complete and tamper-evident records improves the writing and not the evidence.
How long do we have to keep audit logs?
It depends on the obligation, and most firms carry several at once, commonly one year of accessible records with longer holds for certain sectors and contracts. Write down the longest window that applies to each source, then compare it against your searchable window rather than your storage window. Those two numbers are usually different.
Can AI reconstruct an audit trail we did not log?
No, and any tool implying otherwise is generating plausible narrative rather than evidence. AI can correlate records that exist, resolve identifiers, and explain a sequence in readable form. A record that was never emitted is gone, which is why the emission inventory comes before tool selection.
Does an immutable audit log satisfy an auditor by itself?
Rarely on its own. Assessors generally want the record plus the control description, the scope it covers, and evidence that someone reviews it on a stated cadence. Immutability answers the tampering question, and our work on audit-ready infrastructure covers the review cadence that has to sit around it.
How do we test whether our audit trail actually works?
Pick a real account, a real object, and a date more than a year back, then produce the full sequence of actions with timestamps and export it. Time the attempt and note every source that could not answer. Running that drill twice a year finds the silent gaps, much as scheduled penetration testing finds the gaps a configuration review misses.
Who Stands Behind This Guidance
Our team has spent years building and repairing log estates for regulated firms in healthcare, defense supply chain, legal, and finance, which means we have been on the wrong side of the fourteen month question and know what it costs. That experience shapes how we scope managed security services: source coverage and retrieval rehearsal come before dashboards. Matt Rosenthal, who leads Mindcore, keeps the focus on whether a control produces defensible proof for the business rather than on the size of the toolset, and that standard is why we push clients to rehearse a retrieval before renewing a platform.
Book a Free Strategy Call Before Your Next Evidence Request
An audit trail is only as good as the oldest question it can answer, and the question always arrives with a date attached. If your searchable window is shorter than your obligation, if a forwarder could be down right now without anyone knowing, or if the same administrators who run your systems can quietly shorten a retention policy, those are fixable conditions and they cost far less to fix on a normal Tuesday than during a regulator’s deadline. Bring us one dated question you would struggle to answer today. We will map the sources that should have written the record, show you where it stops, and tell you which of the best AI tools for audit trail documentation would change the outcome for your estate. Book a free strategy call and start with the reconstruction test rather than a product list.

