

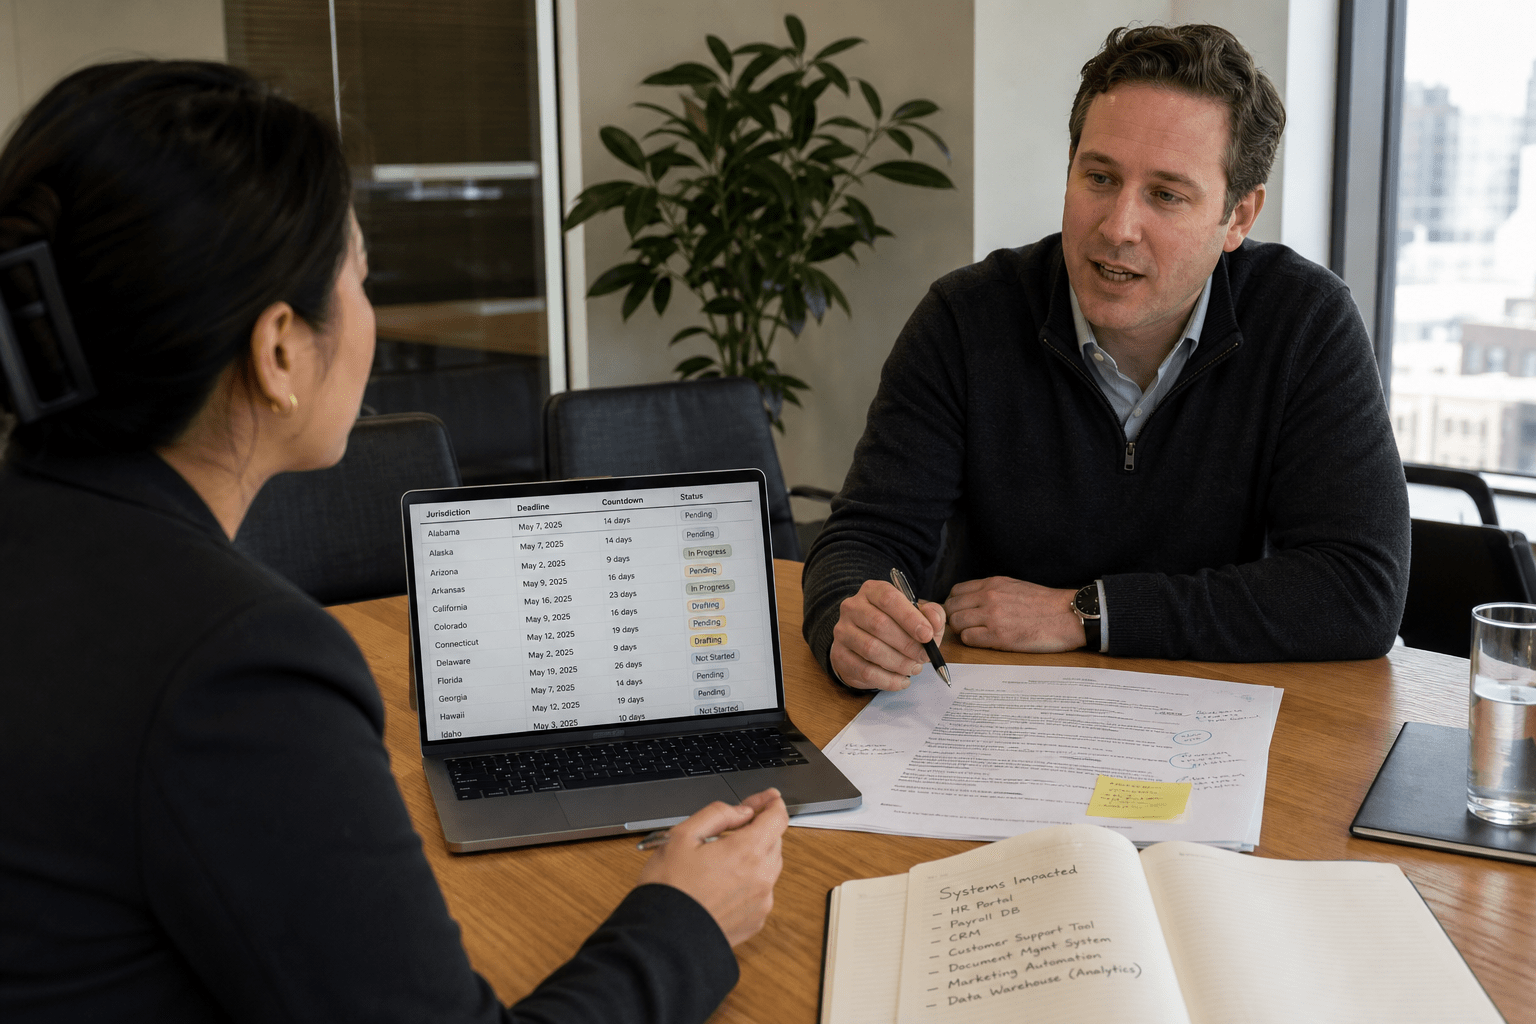
The best AI tools for data breach notification drafting handle the parts that are mechanical and leave the letter itself to counsel. What they do well is assemble the affected-person list from incident data, map each recipient to the state or regulator whose rules govern them, surface the content each of those regimes requires, and hold the clock on every deadline running in parallel. What they do badly is write persuasive legal prose under privilege. Our team treats these platforms as a deadline and jurisdiction engine feeding a lawyer, never as a drafting shortcut. The firms that get burned are the ones that let a model produce the letter and treated counsel review as a formality at the end.
Overview: Five Things That Decide a Notification Goes Out Correctly
- The clock started before you knew. Most regimes run from discovery, and some run from occurrence, so the calendar is set by facts you are still assembling.
- One incident is many notifications. Affected people in different states trigger different rules, and the regulator notice is a separate obligation from the individual notice.
- Content requirements are itemized, not stylistic. Several regimes name the elements a letter must contain, and a missing element makes an on-time notice defective.
- The recipient list is the hardest artifact. Deduplicating people across systems, resolving addresses, and identifying minors takes longer than writing.
- Privilege shapes the workflow. Anything drafted outside counsel’s direction may not be protected, which changes where the tooling can sit.
Why Notification Drafting Goes Wrong Under Time Pressure
Notification drafting fails when the team treats it as a writing task that starts after the investigation ends, because the deadline was running the whole time. We have watched firms spend eleven days on forensics and then discover they had a shorter clock than they thought and a recipient list nobody had begun assembling. The immediate response steps matter, and we cover those in what to do immediately after a data breach, but the notification workstream has to run in parallel rather than after.
The Deadline Is Not One Deadline
Breach notification deadlines run concurrently across every regime that touches your affected population, and deadline-tracking tooling exists because the matrix is genuinely hard to hold in a head. A single incident affecting customers in a dozen states, plus health data, plus a contractual obligation to an enterprise client, can carry six different clocks with different start events. Software that ingests the affected-population breakdown and produces a dated obligation list removes a class of error that has nothing to do with legal skill.
The objection worth taking seriously is that these tools encode a reading of the law that changes. Statutes get amended, regulators publish interpretive guidance, and a platform that has not tracked an amendment produces a confident date that is wrong. A wrong date delivered with a countdown timer is more dangerous than an unanswered question, because nobody re-checks it.
Our position is that the tool owns the arithmetic and a human owns the rule. We use the generated matrix as a worklist and have counsel confirm the governing regime and trigger event for anything unusual, particularly health data, which carries its own layered timing that we walk through in the HITECH breach notification deadlines small firms miss.
Assembling the Recipient List Is the Real Work
Recipient list assembly consumes more of the notification window than drafting does, and it is where automation genuinely earns its cost. The affected records live across a CRM, a billing platform, an email system, and often a backup nobody has queried in years. Tooling that reconciles identities across those sources, flags records with no deliverable address, and separates minors and deceased individuals turns a week of manual work into a reviewable output.
Set against that, an automated reconciliation makes judgment calls about identity matching that carry real consequence. Two records merged wrongly means one person never hears about the exposure of their data. Records split wrongly means duplicate letters, which looks careless to a regulator already reading your response for signs of disorganization.
We handle this by treating the match confidence score as the deliverable rather than the merged list. High-confidence matches proceed, anything ambiguous goes to a human reviewer, and the review decisions are logged. That log has been useful more than once when a regulator asked how the population was determined. One detail worth building in early: record the query that produced each source extract alongside the results. Six months later, when someone asks why a particular customer segment was excluded, the answer needs to be a query rather than a recollection, and reconstructing it after the fact is close to impossible.
Substitute Notice and the Records You Cannot Reach
Substitute notice rules apply when direct contact is not possible, and they impose their own thresholds and formats that vary by regime. Tooling helps by counting the unreachable population and telling you whether you have crossed a threshold that triggers website posting, statewide media notice, or an email alternative. That count is arithmetic against a rule, which is what these platforms do well.
The contrary reading is that leaning on substitute notice too early is a decision with reputational weight, not just a compliance one. A firm that posts a notice on its website rather than working harder on address resolution has technically complied and has also told a regulator something about its effort. Some counsel push clients to exhaust direct contact well past the point automation recommends.
The line we draw is that the tool reports the threshold and a human decides whether to invoke it. Substitute notice is a fallback, not an efficiency, and treating it as the default because software surfaced it as available is how an adequate response becomes a criticized one.
Best AI Tools for Data Breach Notification Drafting: Where the Writing Actually Happens
Drafting assistance is useful in a narrow band: producing a first pass that already contains every element the governing regime itemizes, in the structure regulators expect. Several compliance platforms now maintain per-jurisdiction content checklists and generate a skeleton letter carrying each required element as a labelled section. That skeleton saves counsel from assembling the requirements list themselves, which is the mechanical half of their work.
Required Elements Versus Persuasive Language
Content-requirement automation reliably catches omissions, and omissions are the defect that makes an on-time notice fail. A letter missing the description of the information involved, the date range, or the steps individuals can take is defective in several regimes regardless of how well it reads. A checklist generator that maps each required element to a section is doing verification, not writing.
The limitation shows up immediately past that point. The tone of a notification letter is a legal and commercial judgment about how much to say, how to characterize the incident without conceding facts still under investigation, and how to phrase remediation offers. Generated prose defaults to a register that reads either evasive or over-committal, and both create problems that outlast the incident.
We use the generated skeleton and have counsel write the actual language into it. That split keeps the completeness benefit and keeps the wording where privilege and judgment live. Firms that need help standing up this whole workstream usually start with our data breach incident response service rather than assembling it under pressure.
Regulator Notices Are a Different Document
Regulator notification is a separate obligation with its own format, and treating it as a copy of the individual letter is a common error. Many regimes require a submission through a portal with structured fields covering the incident timeline, the population count by jurisdiction, and the remediation offered. The reporting obligations vary enough that we wrote them up separately in ransomware and data breach notification laws and what to report.
Automation is a mixed proposition here. Structured-field submission is exactly the kind of task software should do, and a platform that pre-fills population counts from the reconciled recipient list removes transcription errors. Yet regulator portals change without notice, and an integration that silently fails or submits into a superseded form creates a compliance gap that looks like a filing.
Our practice is to automate the assembly and confirm the submission by hand. Somebody watches the portal accept it and keeps the confirmation. That step takes minutes and is the only evidence you filed, which matters more than the time it saves to skip it. Healthcare organizations carry extra obligations on top of this, which is why we scope healthcare data management with the notification path already mapped.
Version Control on a Letter Twelve People Are Editing
Notification letters go through more hands than almost any document a firm produces under time pressure, and the tooling that helps least is the tooling that adds another place to edit. Counsel, the security lead, communications, and often an insurer’s panel firm all touch the text inside a few days. Platforms that keep the letter in a versioned workspace with per-section comments beat an email chain of attachments, which is what most firms fall back on and which reliably produces two competing final versions.
The argument against a dedicated workspace is that it puts the most sensitive document of the incident into another vendor system, with its own access model and its own retention. Some counsel refuse for exactly that reason and keep the letter inside the firm’s own environment, accepting a clumsier process in exchange for a smaller footprint.
Both are defensible and the deciding factor is usually the insurer. If a panel firm is involved, the workspace is often theirs and the decision is made for you. Where it is ours to make, we keep the drafting inside counsel’s environment and use the compliance platform for the matrix and the recipient list rather than the prose.
What the Timeline Reconstruction Has to Support
Every notification rests on a timeline that says when the incident occurred, when it was discovered, and what was known at each point, and that reconstruction feeds both the letter and the regulator filing. Tooling that pulls timestamps from forensic output and builds a defensible sequence saves genuine hours, and more importantly it produces something consistent across the individual notice, the regulator submission, and whatever the firm tells its enterprise clients.
The risk is that an automated timeline hardens too early. Forensics revises findings, a discovery date moves once someone finds an earlier alert nobody actioned, and a timeline already embedded in three documents is expensive to correct. Teams have sent notices carrying a date the investigation later contradicted, which is worse than having sent nothing yet.
We keep the timeline in one place and reference it everywhere rather than copying it. When it changes, every document that draws from it changes with it, and somebody signs off that the change propagated before anything goes out.
Frequently Asked Questions
What are the best AI tools for data breach notification drafting in 2026?
The useful category is compliance platforms that combine multi-jurisdiction deadline tracking, per-regime content checklists, and recipient list reconciliation, feeding a skeleton letter that counsel completes. Judge them on how current their jurisdiction rules are and whether they show you their reasoning, not on the quality of the prose they generate.
Can AI write our breach notification letter?
It can produce a structurally complete first pass and should not produce the final wording. The letter involves judgment about characterizing an incident still under investigation, and that judgment carries legal consequence. Use generated output as a completeness check under counsel’s direction.
How do these tools handle different state deadlines?
The better platforms map your affected population by jurisdiction and produce a dated obligation list showing every clock running in parallel. Confirm the trigger event with counsel, because regimes differ on whether the clock starts at discovery, at confirmation, or at occurrence, and that difference can move a deadline by weeks.
Does using an AI tool affect attorney-client privilege?
It can, which is why the workflow matters as much as the tooling. Work performed at counsel’s direction and within their engagement stands a better chance of protection than analysis a vendor platform generated independently. Have your lawyer specify where the tooling sits before an incident, not during one.
What should we set up before we ever need this?
Build the data map first. The reason notification takes weeks is that nobody knows which systems hold personal information, so map that now, and understand how breaches actually happen so the map covers the paths that matter.
Who Is Behind This Advice
Mindcore supports firms in regulated industries through incidents where the notification window is measured in days and the affected population spans several states. The patterns here come from that work: the clock that started earlier than the team assumed, the recipient list nobody began until forensics finished, the regulator portal submission that was never confirmed. Our engineers build the data map and the obligation matrix before an incident, because both are far cheaper to assemble on a normal Tuesday. The broader response sequence is laid out in what a company should do after a data breach.
Matt Rosenthal, Mindcore’s CEO, focuses the firm on preparation that holds up under real conditions rather than documentation that satisfies a checklist, which is why our incident work starts with knowing where the data lives. That emphasis shapes how our team scopes every engagement.
Get Your Notification Path Mapped Before You Need It
Breach notification is a deadline problem, a data problem, and a legal problem, and only the third one is about writing. The tooling in this article handles the first two capably: it holds every clock, itemizes what each regime requires, and turns a scattered population into a reviewable list. It does not decide how to characterize an incident, whether to invoke substitute notice, or what your regulator will read into your response. Those calls belong to counsel and to the people who know your business. Firms that prepare well map their data, agree the workflow with their lawyer, and rehearse the sequence once. Firms that do not tend to discover all three problems in the same week.
If you have not mapped where personal information lives across your systems, that is the work worth doing now, and it is the work that shortens every future notification window. Our engineers walk the estate with your team, document the systems holding regulated data, and build the obligation matrix your counsel will need. Book a free strategy call and we will start with your data map.

