The best AI tools for zero trust architecture planning are the ones that build your inventory, not the ones that enforce your policy. Enforcement products are mature and largely interchangeable for a 50 to 500 person firm. What stops these projects is that almost nobody can answer three questions on day one: which identities exist, which of them are service accounts carrying standing privilege, and which systems actually talk to each other. We have watched well funded rollouts stall for months on that gap. AI helps most in discovery, traffic baselining, and turning observed behavior into a first draft of policy. Choose tools for that phase and the enforcement decision gets easier later.
Why Zero Trust Planning Stalls Before Enforcement Starts
Zero trust planning stalls because teams buy a policy decision point before they have an accurate map of the identities and data flows that policy will govern. Five patterns cause most of the delay we see in the field:
- Nobody owns the service accounts. A ten year old file server runs as a domain account created by a contractor who left in 2019. It holds standing access to three shares and has no MFA path.
- The identity list and the payroll list disagree. Offboarding closed the mailbox and left the VPN profile, the SaaS seat, and the local account on the finance workstation.
- East-west traffic is unmeasured. Teams document what should talk to what, segment on that document, then break a scheduled billing job at month end.
- Legacy protocols hide in the middle tier. NTLM and SMBv1 still carry real workloads at firms that believe they retired both years ago.
- Policy is written from a template. A downloaded ruleset describes a reference architecture nobody here operates, so exceptions pile up until the ruleset means nothing.
Each of these is an inventory problem wearing a policy costume. If you want the model itself first, our primer on what zero trust actually means is the right starting point.
Where AI Tools for Zero Trust Architecture Planning Earn Their Place
AI tools for zero trust architecture planning earn their place in the three weeks of discovery work that precede any enforcement purchase, because that work is pattern matching across large, messy log volumes and humans are slow and inconsistent at it. Our team treats the planning phase as three jobs: find every identity, watch what actually moves, and write policy from what you observed rather than from a reference diagram. The tools worth paying for are the ones that shorten one of those three and produce an artifact a human can argue with.
Identity Inventory and the Service Accounts Nobody Owns
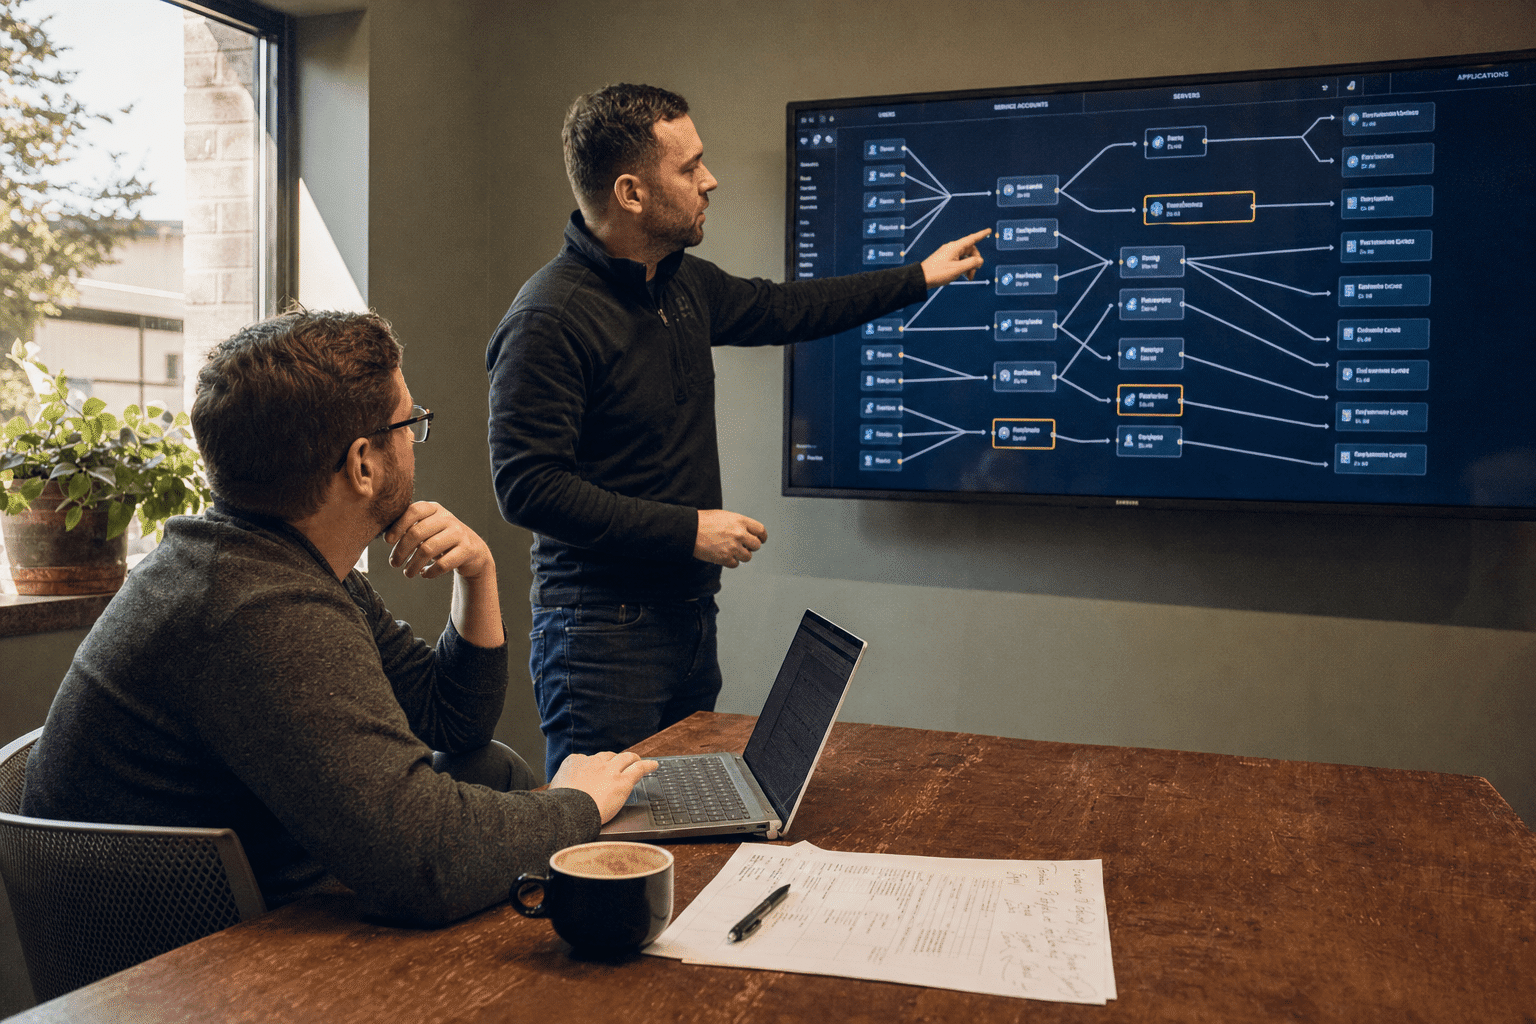
Identity inventory is where zero trust planning either gets real or quietly fails, because a policy engine can only govern principals it knows about. In favor of automated inventory: correlation engines that read Entra ID sign-in logs, on-premises domain controller events, and SaaS admin APIs together will surface non-human principals far faster than a spreadsheet exercise. They cluster by authentication pattern, so an account that signs in every night at 2:14 from one host gets flagged as machine-driven regardless of how it was named.
Against it: these tools infer ownership, and inference is not proof. We have seen a shared account used by four people classified as a service account and nearly stripped of interactive rights. The honest position is that automated inventory is excellent at finding candidates and poor at assigning accountability. Run the discovery, then walk the list with the people who own the systems. Budget an afternoon per department. The output you want is a signed list where every non-human principal has a named human owner and a stated reason to exist, because that document is what your later access reviews compare against.
Data Flow Mapping Across East-West Traffic
Data flow mapping decides whether your first segmentation attempt breaks production, and it is the part teams most often skip. Arguing for behavioral mapping tools: agents or flow collectors that baseline traffic for two to four weeks will find the connections nobody documented, including the month-end batch job, the reporting server that reads the ERP database directly, and the workstation the accounting lead uses as an informal file share.
Arguing against: a baseline captures only the period it observed. A quarter-end process, an annual audit export, or a disaster recovery test that runs twice a year will not appear, and segmenting on an incomplete baseline produces an outage at the worst possible moment. We ask clients to overlay the flow map with their own calendar of periodic processes before anything moves to enforcement, and to hold the first policies in monitor mode across at least one full month-end close. Firms with heavy project cycles, including the architecture and engineering practices we support, often carry seasonal traffic that a four week window simply cannot see.
Drafting Policy From Observed Behavior, Not Guesswork
Policy drafting is the third place AI genuinely reduces effort, because turning a flow map into a candidate ruleset is mechanical translation. Tools that generate draft policy from observed traffic will produce a starting ruleset in hours rather than the weeks a manual pass takes, and the better ones annotate each rule with the observations that justified it.
The counterargument matters here. Generated policy encodes current behavior, including the behavior you intend to eliminate. If the finance workstation reaches the domain controller over SMB today, a behavior-derived rule will permit exactly that tomorrow. Our team reads every generated rule with one question: is this traffic something we want to keep, or something we merely found. That review is human work and it does not compress well. The useful framing is the one we set out in why zero trust is a model and not a product, where the tool drafts and your team decides.
The Legacy Protocol Problem Discovery Surfaces First
Legacy protocol dependency is the most common reason a zero trust pilot gets rolled back, and discovery tooling finds it early enough to plan around. Almost every mid-sized environment we assess still carries NTLM authentication somewhere, usually behind a line-of-business application whose vendor never shipped a Kerberos path. The planning question is not whether to remove it, but which systems will fail the day you do.
NTLM, SMBv1, and the Applications That Break Under Segmentation
Legacy authentication protocols break under segmentation in ways that look like network faults, which is why teams misdiagnose them for days. In support of protocol-aware discovery tools: they parse authentication events by type and report which hosts still negotiate NTLM and which shares still answer SMBv1, with the calling application named. That report is the difference between a planned remediation and a Monday morning outage.
The limitation is scope. These tools see what crosses the sensor. An isolated manufacturing subnet or a vendor-managed appliance often sits outside instrumented paths, so the report reads clean while the dependency is real. We treat a clean legacy protocol report as evidence only for the segments actually instrumented, and we say so in writing. For regulated firms this distinction carries weight, and our notes on mapping CMMC controls to zero trust infrastructure cover how to document instrumented scope so an assessor sees the same boundary you do.
Modeling Blast Radius Before You Enforce
Blast radius modeling answers the question your leadership will ask, which is what actually improves if this project finishes. Simulation features in modern planning tools take the identity graph and the flow map and compute reachability: if this workstation is compromised, which systems can that session reach today, and which could it reach after the proposed policy. That produces a number your board understands.
The case against relying on it: reachability models assume the policy gets enforced as written, and real deployments accumulate exceptions. A model showing an eighty percent reduction describes the design, not the deployment six months later after twelve exceptions. We recommend re-running the model against enforced policy each quarter rather than trusting the design-time figure. Healthcare clients tend to feel this first, and the practical containment patterns sit in our write-up on protecting PHI with zero trust secure workspaces.
How We Score AI Tools for Zero Trust Architecture Planning
We score AI tools for zero trust architecture planning on four things, and feature count is not one of them. First, does it export its findings in a format a human can review outside the vendor console, because an inventory locked in a dashboard cannot be signed off. Second, does it show its evidence, so every claim about an identity or a flow points back to the observations behind it. Third, does it state its own coverage, naming what it did not see rather than reporting silence as safety. Fourth, does the output survive an audit, meaning dated artifacts you can hand an assessor a year later without regenerating anything.
That fourth test rules out more products than the first three combined. A tool that regenerates its view every time you open it gives you a current picture and no record, and for firms working toward a certification the record is the deliverable. Teams pursuing CMMC should read our notes on how zero trust architecture supports CMMC compliance before choosing, since the evidence format shapes what the assessment costs. Planning also has to account for failure modes, which is why we run this work alongside business continuity planning rather than after it. Our broader reference material sits in the zero trust resource library.
Evidence Export That Survives an Audit
Evidence export separates a planning tool from a monitoring dashboard, because zero trust work gets assessed long after the discovery window closes. In favor of demanding export: an assessor reviewing your access control implementation wants to see the inventory you worked from, the date you built it, and the reasoning behind each policy decision. A tool that writes dated CSV or JSON alongside its console view lets you hand over that package without a scramble, and it lets a new engineer eighteen months later understand why a rule exists.
The argument on the other side is real. Export formats age badly, and a CSV of identities from 2026 tells an assessor nothing about the environment in 2027 unless somebody refreshed it. Export by itself is not a record, it is only the raw material for one. Our team pairs it with a short written scope statement each quarter that names what was instrumented and what was not, because the gap between those two is what an assessor probes hardest. We have watched firms hand over a beautiful identity export and then fail a control because nothing in the package said which subnets the sensors never touched. Write the coverage down in the same folder as the data, and date both.
The practical test we apply during a vendor demo is simple. Ask the vendor to produce last month’s view rather than today’s. A planning tool answers in seconds. A monitoring dashboard changes the subject.
One more thing worth settling before you sign anything: who keeps the data if you leave. Several planning products hold the identity graph and the flow history inside the vendor tenant, and the export you get on termination is a snapshot rather than the working record. For a firm on a multi-year certification path that matters, because the evidence trail has to outlive the contract that produced it. We ask for the retention and export terms in writing during procurement, not at renewal. It is a dull question that saves an expensive year later, and the vendors worth working with answer it without hedging.
Frequently Asked Questions
Do AI tools replace a zero trust assessment?
No, AI tools shorten the discovery portion of an assessment but do not replace the judgement it requires. They produce candidate inventories and draft policy quickly. Deciding which findings matter, who owns each account, and which traffic to keep remains human work.
How long should traffic baselining run before segmentation?
Plan for two to four weeks of continuous observation, then extend across at least one full month-end close before enforcing anything. Periodic processes are the most common source of segmentation outages, and a short baseline will miss quarterly and annual jobs entirely.
Can these tools find shadow SaaS accounts?
Most identity correlation tools find SaaS accounts that authenticate through your identity provider, and miss those that do not. Departments that pay by credit card and sign up with a personal address stay invisible. Pair the tool output with an expense review to close that gap.
Is a behavior-derived policy safe to enforce directly?
Enforcing generated policy without review is the fastest way to lock in the access problems you set out to fix. Generated rules describe what happens today, including standing privilege nobody intended. Read each rule, mark what should not continue, then enforce.
What size firm benefits most from AI-assisted planning?
Firms between roughly 50 and 500 staff see the largest gain, because their environments are complex enough to defeat a manual inventory and small enough that a dedicated security team does not exist. Below that size a careful manual pass is often faster.
Who Is Behind This Advice
Our team has run zero trust planning engagements for regulated mid-market firms across healthcare, professional services, and defense supply chain work, and the pattern holds across all of them: the discovery phase decides the outcome. We have sat through the outage that follows a segmentation push built on an incomplete flow map, and we have written the remediation plans afterward. That experience is why we push clients to spend money on inventory quality before enforcement licensing, even though the licensing conversation is the one vendors want to have first.
Matt Rosenthal leads Mindcore and focuses on making security work sit inside a business plan rather than beside it, so that the controls a firm adopts are ones it can still operate in three years.
Start With Your Inventory, Not Your Vendor Shortlist
The takeaway is simple enough to act on this quarter. Zero trust succeeds or fails on the quality of the identity and data inventory you build before any enforcement product is chosen, and that is the work AI tooling genuinely accelerates. Run identity correlation across your directory and your SaaS estate, baseline east-west traffic through a full month-end close, generate draft policy from what you observed, then read every rule and decide what stays. Keep the artifacts dated and exportable so the work counts as evidence later. The enforcement decision that felt urgent at the start of the project becomes straightforward once you can describe what you are protecting and who reaches it today. If you would rather not run that discovery alone, our team does this work with mid-market firms every week and can tell you inside a short conversation whether your environment needs four weeks of baselining or twelve. Book a free strategy call and we will walk your current inventory with you.