

Information security challenges in business organizations usually start with how the company is run rather than with a missing tool. In the small and midsize organizations our team works with, the recurring problems are unclear ownership of security decisions, software and AI tools adopted without review, a growing list of vendors with access to data, budgets set without a risk picture, and leadership that receives no regular measure of how secure the company is. Each of these creates gaps that attackers exploit through ordinary means: a phished login, an unpatched system nobody was assigned to update, or a vendor account left active after a contract ended. Technical controls matter, but they fail when nobody is accountable for running them. This article walks through the organizational challenges in turn and the practical fixes that work for a company without a full security department.
Overview: Five Organizational Gaps Behind Most Incidents
Security incidents at small and midsize businesses tend to trace back to a short list of organizational gaps. These five frame the article.
- No clear owner. Security tasks are spread across an office manager, an outside IT provider and a busy executive, so decisions stall.
- Tools arrive unreviewed. Staff sign up for cloud apps and AI assistants on their own, creating data flows nobody tracks.
- Vendors multiply. Every software subscription and contractor adds an account, an integration or remote access that must be managed.
- Budgets follow habit. Spending repeats last year’s line items instead of following current risk.
- Leadership sees nothing. Without a few simple measures, executives cannot tell whether risk is rising or falling.
Why Security Ownership Is the First Challenge to Solve
Security ownership is the first challenge to solve because every other control depends on someone being responsible for keeping it running. In many growing companies, security sits in the gap between the outside IT provider, who assumes the client decides policy, and the client, who assumes the provider handles everything.
Name one accountable person
Assign security accountability to one named leader, even if most of the work is done by others. In a small business this is often the operations director or a partner rather than a technical specialist. Their job is to make decisions, approve exceptions and report to leadership. Our article on what a chief information security officer does explains the role many companies fill on a fractional basis.
Write down who does what
A one-page responsibility chart listing tasks such as patching, user access reviews, backup testing and incident response, with an owner for each, prevents assumptions. Share it with your IT provider and review it when staff or vendors change.
Give the owner time and authority
Ownership without time is a title. Set aside a few hours a month for the accountable person, and give them authority to pause risky projects or require fixes.
How Shadow IT and Shadow AI Create Hidden Exposure
Shadow IT and shadow AI create hidden exposure because staff adopt cloud apps and AI tools to get work done faster, often connecting them to company email, files or customer data without anyone reviewing the terms or the security settings. The intent is usually good. The result is data in places the company cannot see or control.
Find what is already in use
Review sign-in logs and connected app consents in your identity platform, check expense reports for software subscriptions, and ask teams what tools they rely on. Most companies find more tools than expected. Our article on shadow AI oversight and unapproved tools lists common examples.
Offer an approved path
Banning tools outright drives them further out of sight. Publish a short list of approved apps and a quick request process for new ones, with a response promised within days. People follow a process that is faster than working around it.
Set rules for sensitive data
Make clear which types of data, such as client records, financial information and health data, may never be pasted into unapproved tools. Reinforce this with brief security awareness training and technical controls where your licenses allow.
Why Vendor Sprawl Weakens Security Over Time
Vendor sprawl weakens security over time because each new supplier adds accounts, integrations and sometimes remote access that rarely get removed when the relationship ends. A company with dozens of software subscriptions can easily have former vendors still holding valid credentials.
Keep a vendor register
Maintain a list of vendors with access to your systems or data, what they can reach, who owns the relationship and when the contract ends. Review it twice a year and remove access for anyone no longer under contract.
Limit and monitor vendor access
Give vendors only the access they need, require multi-factor authentication, and log their activity. Our guide to zero trust security steps a small business can afford shows how to apply least privilege without slowing work.
Align contracts with security expectations
New contracts should require prompt breach notification, reasonable security controls and the return or deletion of your data at the end of the engagement.
How to Give Leadership Security Metrics They Can Use
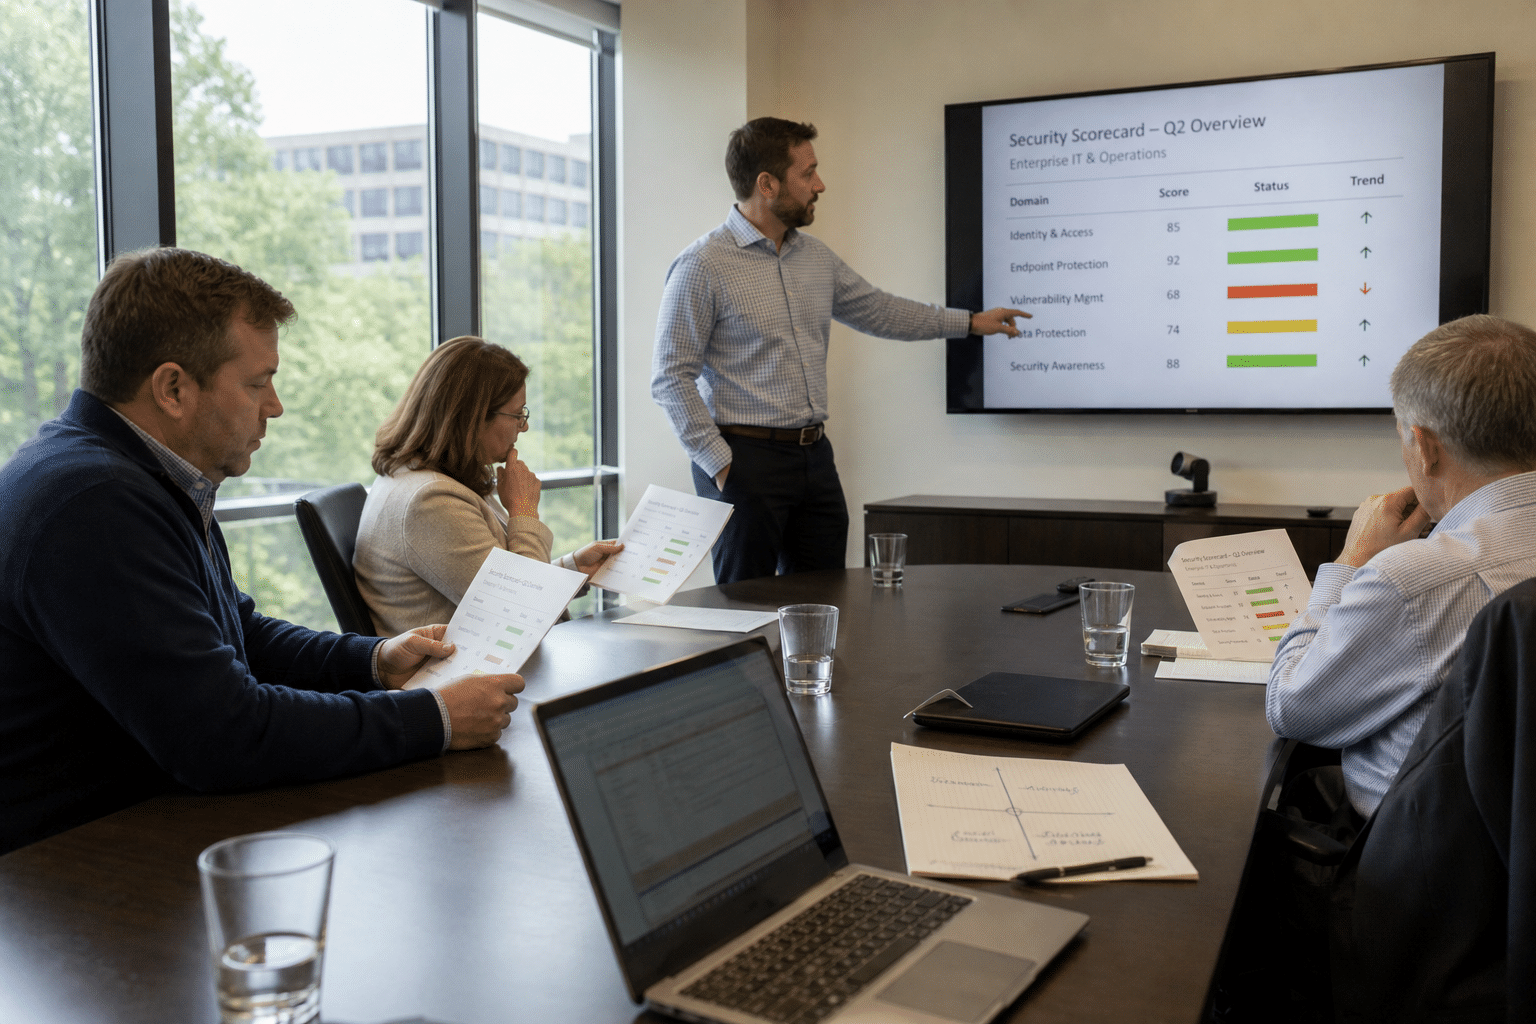
Security metrics for leadership should be few, plain and tracked over time, so executives can see trends and make decisions. Long technical reports go unread; a one-page scorecard reviewed quarterly gets attention.
Pick five measures
Useful starting measures include the percentage of accounts with multi-factor authentication, the share of devices fully patched, the date of the last successful backup restore test, the number of open high-risk findings, and phishing simulation click rates. Each is easy to explain and points to a clear action.
Tie budget to risk
Use the scorecard and an annual cyber security audit to rank spending by risk reduction. This replaces repeating last year’s budget with spending that addresses current gaps. Planning should also cover recovery, which our business continuity planning service helps define.
Separate governance from tooling
Understanding the difference between deciding how data should be handled and protecting it technically helps leaders assign the right work to the right people, as our article on data governance vs data security explains.
How a Tabletop Exercise Reveals Organizational Weak Spots
A tabletop exercise reveals organizational weak spots by walking leaders through a realistic incident on paper and watching where decisions stall. It costs a couple of hours and no software, and it tests the ownership, vendor and communication questions above all at once.
Choose a scenario that fits your business
Pick an incident your company could plausibly face: a finance employee’s mailbox taken over and used to request a wire transfer, ransomware on the file server the week before payroll, or a vendor announcing that your client data was exposed. A scenario tied to your own operations produces far better discussion than a generic one, because people recognize the systems and contacts involved.
Watch for the questions nobody can answer
During the exercise, note every moment where the room goes quiet. Who calls the cyber insurer, and is the policy number at hand? Who can authorize taking the email system offline? Which vendor holds the backups, and how long would a restore take? Who speaks to clients and staff, and what can they say? Each unanswered question is a gap in ownership or documentation, and it is far cheaper to find it in a conference room than during a live incident.
Turn findings into owned actions
End the session by listing each gap with a named owner and a due date, then review progress at the next quarterly scorecard meeting. Repeat the exercise once a year with a new scenario. Over time, the exercise becomes a measure in its own right: fewer unanswered questions means a more prepared organization. Many companies run the first session with outside facilitation so leaders can focus on decisions rather than on running the exercise, and an annual review keeps the plan aligned with staff and vendor changes.
Frequently Asked Questions
What are the biggest information security challenges in business today?
The biggest challenges are unclear ownership, unreviewed cloud and AI tools, unmanaged vendor access, budgets that ignore risk, and a lack of metrics for leadership. Technical threats such as phishing and ransomware exploit these gaps.
Does a small business need a dedicated security leader?
A small business needs a named accountable person, but that person does not have to be a full-time specialist. Many firms combine an internal owner with a fractional security officer or a managed security provider.
How do we find shadow IT in our company?
Review sign-in logs and connected app approvals, check software expenses, and ask teams what they use. Then offer an approved request path so new tools come through review.
How often should vendor access be reviewed?
Review vendor access at least twice a year and whenever a contract ends, removing accounts and integrations that are no longer needed.
What security metrics should executives see?
Executives should see a short scorecard covering multi-factor coverage, patch status, backup restore testing, open high-risk findings and phishing results, reviewed every quarter.
Who Is Behind This Guidance
Mindcore Technologies helps small and midsize organizations build security programs that fit their size, from assigning ownership and writing policies to monitoring and incident response through our managed security services. Our team sees the organizational gaps described here in nearly every first assessment, and the fixes in this article come from that work. Mindcore is led by CEO Matt Rosenthal, who focuses on helping organizations reduce cyber risk with practical controls that leadership can measure and trust.
Solve the Organizational Side of Security First
Information security challenges in business organizations are often framed as a technology problem, but the gaps that cause the most harm are organizational. Name one accountable owner and write down who does what. Bring shadow IT and shadow AI into the open with an approved path. Keep a vendor register and remove access that is no longer needed. Give leadership a short scorecard and use it to direct the budget. These steps cost little, and they make every security tool you already own work better. If you are not sure who owns security decisions in your company today, or what your leadership would see on a one-page scorecard, our team can help you build both. Book a free strategy call and we will help you identify the organizational gaps that matter most and set up a simple program to close them.

