

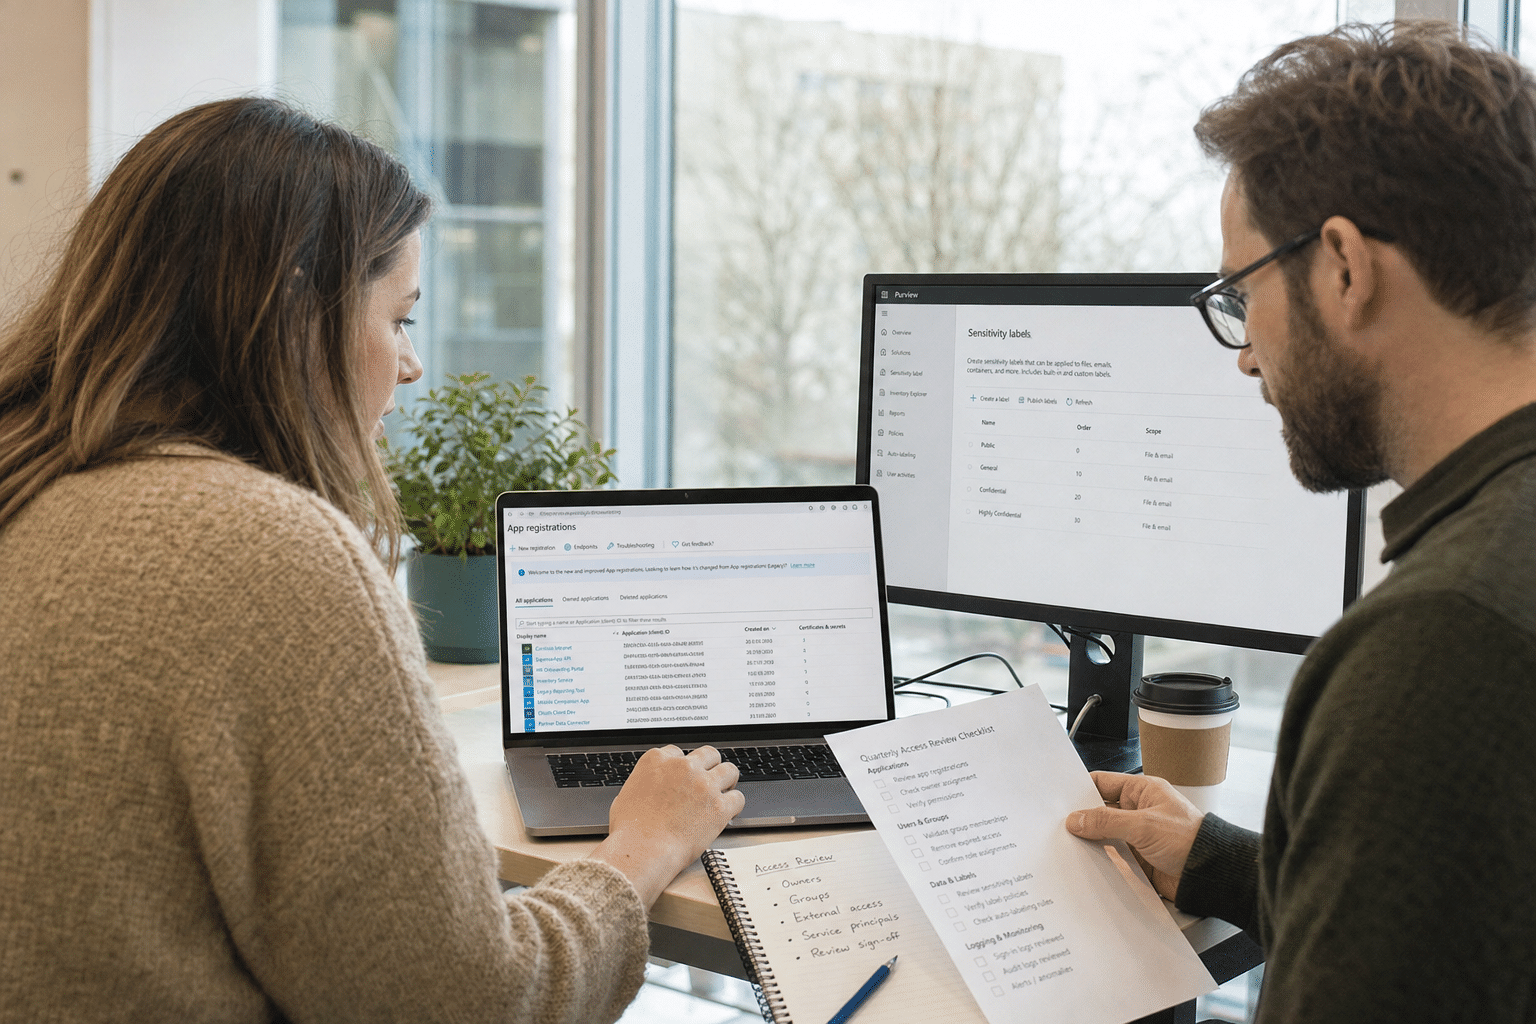
Microsoft Ignite 2026 security news is built around one idea: AI agents now act inside your business with real access to identities, data and cloud resources, and they need the same controls as people. Microsoft’s own Ignite guide, published on its Security Blog on September 30, 2026, describes an AI-first, end-to-end security platform covering identities, devices, data, applications, clouds, infrastructure and the AI agents working alongside your teams. The event runs November 17 to 20 in San Francisco and online, with a Security Pre-Day on November 16. The security track groups its sessions into four themes: defending with AI, securing AI, getting ready for AI with identity and Zero Trust basics, and securing data for Copilot. For a small or midsize business, the announcements will sound large and expensive. This article turns them into six practical questions an SMB IT team can answer before buying anything new.
Overview: What Ignite’s Security Track Means for Smaller Teams
Ignite sessions are written for enterprises with security operations centers. Five points translate the message for an organization with a small IT team or an outsourced provider.
- Agents are now identities. Microsoft is treating AI agents as non-human users that need sign-in controls, permissions and monitoring through Microsoft Entra.
- Agent 365 is the new management layer. Microsoft describes its own security team as customer zero for Agent 365, its control plane for discovering and governing agents.
- Data exposure comes before AI risk. The hands-on lab on deploying Copilot with confidence focuses on finding and protecting overshared sensitive data, which is a problem most SMBs already have.
- The SOC is being rebuilt around automation. Sessions on the agentic SOC and autonomous protection describe Defender and Sentinel handling more triage on their own.
- Fundamentals still decide outcomes. Identity hygiene, device trust through Intune and Zero Trust policies remain the base every new feature depends on.
How Microsoft Ignite 2026 Security Changes the Identity Conversation
Microsoft Ignite 2026 security sessions put identity at the center because an AI agent acting on your behalf is only as safe as the permissions it holds. A session titled “Local agents are here. Can you find and secure them?” makes the point directly. Agents built in Copilot Studio, connected to Microsoft 365 data, or installed by employees on their own devices can read mail, files and records with whatever access they were granted.
Question one: do you know which agents exist today?
Before evaluating new tools, list the agents and automations already running. Check Copilot Studio, Power Automate flows, connected apps with Microsoft 365 permissions, and any third-party AI tools employees have approved through consent screens. In our assessments, most SMBs find several connected apps nobody remembers approving. Our article on what Microsoft 365 Copilot can do is a useful starting point for understanding where Copilot reaches.
Question two: are agents held to the same sign-in rules as people?
Conditional Access policies in Microsoft Entra decide who can sign in, from where and on which devices. Ask whether the same discipline applies to service accounts and agent identities, including least privilege and regular review. An agent with broad Graph permissions and no owner is a gap whether or not you ever buy Agent 365.
Question three: who owns each agent?
Every agent should have a named human owner responsible for its permissions and its retirement. When an employee leaves, their agents and flows should be reviewed with the rest of their access. This is a process question, and it costs nothing to put in place.
Why Purview Data Security for Copilot Matters Before Any New Purchase
Purview data security for Copilot matters because AI assistants surface whatever a user can already access, and most organizations have far more overshared content than they realize. Copilot does not create new permissions; it makes existing ones easier to use. A file shared with everyone in the company years ago becomes something Copilot can summarize for any employee who asks.
Question four: where is your sensitive data overshared?
Run a sharing review in SharePoint and OneDrive. Look for sites shared with everyone, anonymous links that never expire, and folders holding financial, HR or client records with broad access. Sensitivity labels and data loss prevention in Microsoft Purview can then restrict what Copilot and agents may read. Our guide to Microsoft 365 hardening settings that expose SMBs covers several of the defaults behind oversharing.
Labels only work if people apply them
Automatic labeling helps, but it depends on license tier and careful setup. Pair it with short security awareness training so staff know what each label means and when to use it.
Backups cover the agent mistakes
Agents can delete or overwrite content as easily as people can. Confirm that your Microsoft 365 backup covers mail, SharePoint and Teams with retention that matches your needs; our Microsoft 365 backup guide explains the gaps native retention leaves.
What the Agentic SOC Means for Microsoft Sentinel SIEM and Defender Users
The agentic SOC that Ignite promotes means Microsoft Sentinel SIEM and Microsoft Defender will automate more alert triage and response, with AI agents investigating incidents before a human looks. Session titles such as “The Alert Is Dead” and “Winning the Race Against Time with Autonomous Protection” signal where the products are heading.
Question five: who acts on what the automation finds?
Automation shortens triage, but someone still has to approve containment, talk to users and decide on business impact. For a team of two or three, that usually means a managed security services partner covering nights and weekends. Ask any provider how they will use new Defender and Sentinel automation, and what decisions stay with your staff.
Cost follows data volume
Sentinel pricing is driven by the data you ingest. Before adding agent activity logs and new connectors, estimate the volume and decide which logs truly need SIEM retention and which can live in cheaper storage.
Test before trusting autonomous actions
Autonomous containment can isolate a device or disable an account in seconds. Run it in report-only mode first, review its decisions for a few weeks, and then enable automatic actions for the clearest cases.
How to Apply Zero Trust for AI Without an Enterprise Budget
Zero Trust for AI means verifying every agent and user explicitly, granting the least access needed, and assuming a breach is possible, which are the same principles applied to people for years. Ignite offers a hands-on Zero Trust for AI workshop, but most of the work for an SMB uses tools already in its Microsoft 365 subscription.
Question six: what do your current licenses already include?
Many businesses on Microsoft 365 Business Premium already have Entra Conditional Access, Intune device management, Defender for Business and core Purview features. Before buying new add-ons announced at Ignite, confirm which of these are configured and enforced. Our Office 365 services team often finds paid features that were never switched on.
Require compliant devices for sensitive access
Use Intune to mark devices as compliant and Conditional Access to require them for mail, files and admin portals. This blocks many credential theft attacks and limits where agents can run with your data.
Review cloud permissions quarterly
Extend the same review to Azure subscriptions and other cloud services; our cloud security team can help set up a quarterly cadence that keeps permissions from drifting.
Frequently Asked Questions
When is Microsoft Ignite 2026?
Microsoft Ignite 2026 runs November 17 to 20, 2026, in San Francisco and online, with a Security Pre-Day on November 16. The opening keynote is on November 17.
What is Agent 365?
Agent 365 is Microsoft’s management layer for discovering, governing and securing AI agents across an organization. Microsoft says its own security team uses it as customer zero.
Does a small business need Agent 365 right away?
Not necessarily. Most SMBs get more value first from inventorying existing agents and connected apps, tightening Entra Conditional Access, and fixing overshared data in Purview.
Will Copilot expose files employees should not see?
Copilot respects existing permissions, so it can surface any file a user already has access to. Fixing oversharing before rollout is the most effective protection.
Which Microsoft 365 plan covers the security basics?
Microsoft 365 Business Premium includes Conditional Access, Intune, Defender for Business and core Purview features, which cover most SMB fundamentals when configured properly.
Who Is Behind This Guidance
Mindcore Technologies helps small and midsize organizations secure Microsoft 365, Azure and the AI tools built on them, from Conditional Access design to Purview data protection and round-the-clock monitoring. Our team configures the features clients already pay for and plans sensible next steps when new capabilities arrive, and our cyber security audits give leadership a clear baseline before any purchase. Mindcore is led by CEO Matt Rosenthal, who focuses on helping organizations adopt new technology while keeping cyber risk measurable and under control.
Turn Ignite Announcements Into a Short, Practical Plan
Microsoft Ignite 2026 security announcements will center on AI agents, Agent 365, agent identity in Entra, Purview data protection for Copilot and an increasingly automated SOC in Defender and Sentinel. For an SMB, the right response is a short list of questions rather than a shopping list. Know which agents already exist, hold them to the same sign-in rules as people, give each one an owner, fix overshared data before Copilot finds it, decide who acts on automated alerts, and confirm what your current licenses already include. Those steps reduce risk now and make any later investment far more effective. If you want help answering the six questions for your own environment, our team can review your Microsoft 365 configuration with you. Book a free strategy call and we will show you which Ignite announcements matter for your business and which settings to fix first.

